

What Is HIPAA and Why Is It Essential for Healthcare Organizations?
What Is HIPAA and Why Is It Essential for Healthcare Organizations?
What Is HIPAA and Why Is It Essential for Healthcare Organizations?
>What Is HIPAA and Why Is It Essential for Healthcare Organizations?
What Is HIPAA and Why Is It Essential for Healthcare Organizations?
What Is HIPAA and Why Is It Essential for Healthcare Organizations?
Organizations in the healthcare industry handle some of the most sensitive information on a daily basis. Information ranging from patient records to insurance and billing information must be protected not only to follow proper procedures but also to comply with applicable laws.
That’s where HIPAA compliance becomes important. Regardless of whether you are a healthcare provider, a health tech startup, or even SaaS serving healthcare providers, understanding HIPAA is crucial for you.This article explains the significance of HIPAA and HIPAA compliance.
What Is HIPAA?
The Health Insurance Portability and Accountability Act of 1996 (HIPAA) is an act of US Federal Law enacted to ensure the protection of sensitive health data of individuals. This legislation establishes national standards for the privacy, security, and exchange of health information and grants increased rights to the patient over their own health care information.
It applies to healthcare organizations that handle Protected Health Information (PHI).
Why Was HIPAA Introduced?
Prior to HIPAA, healthcare facilities maintained inconsistent standards in regards to data security, raising the risk of its improper usage and access.
HIPAA was introduced to:
- Protect patient privacy
- Secure electronic health information
- Standardize healthcare data exchange
- Reduce healthcare fraud
- Improve efficiency within the healthcare industry
In the modern-day world, HIPAA has become the base for ensuring data security within the healthcare industry.
What Is HIPAA Compliance?
HIPAA compliance involves implementing administrative, physical, and technical safeguards that meet HIPAA requirements for protecting PHI and ePHI.
Compliance is not only about the implementation of security measures; it requires organizations to have written policies, educate their employees, manage risks, and ensure that their business associates follow the same standards.
Why Is HIPAA Important?
HIPAA matters as it provides for patient privacy, improves cybersecurity in the healthcare industry, mitigates the risk of data breaches, guarantees regulatory compliance, and allows for building up patients’ trust.
In general, HIPAA creates a safe environment in which sensitive information can be processed through its entire life cycle.
Why Is HIPAA Compliance Essential for Healthcare Organizations?
It should be noted that healthcare organizations are one of the industries under the strongest attacks from cybercriminals as medical information is extremely valuable.
Adopting HIPAA for healthcare organizations has a number of advantages.
1. Protects Patient Privacy
Healthcare professionals have access to confidential information of patients.
HIPAA ensures organizations:
- Limit unnecessary access
- Protect sensitive records
- Maintain confidentiality
- Respect patient rights
Maintaining privacy strengthens long-term patient relationships.
2. Reduces Cybersecurity Risks
Healthcare ransomware infections keep increasing.
In order to promote security, HIPAA advises healthcare organizations to consider:
- Multi-factor authentication
- Encryption
- Access controls
- Audit logging
- Secure backups
- Continuous monitoring
They provide substantial protection against security threats.
3. Helps Avoid Regulatory Penalties
Consequences of non-compliance with HIPAA requirements include:
- Investigations
- Action plans
- Penalties
- Legal consequences
- Damage to reputation
A compliance strategy will help you avoid all of these.
4. Improves Organizational Reputation
There is a rising tendency of patients preferring organizations with robust privacy and security measures.
Compliance with HIPAA will aid healthcare organizations:
- Increase patient confidence
- Build credibility
- Strengthen brand reputation
- Improve partnerships with insurers and vendors
5. Supports Digital Healthcare Innovation
The rise of the healthcare sector in the use of cloud solutions, telemedicine, mobile apps, and AI-driven technologies necessitates the HIPAA compliance policy.
Who Must Comply with HIPAA?
HIPAA applies to several categories of organizations.
Covered Entities
These include:
- Hospitals
- Clinics
- Physicians
- Dentists
- Pharmacies
- Health insurance companies
- Healthcare clearinghouses
Business Associates
Business associates are third-party companies that process or access Protected Health Information on behalf of covered entities.
Examples include:
- Cloud service providers
- Medical billing companies
- Data analytics firms
- IT managed service providers
- SaaS vendors
- Telehealth platforms
Business associates are also required to meet HIPAA obligations.
What Information Does HIPAA Protect?
HIPAA provides protection to the Protected Health Information (PHI), which is defined as all information, which can be used to identify any person and is related to the individual’s health status or services.
These include:
Personal Information
- Patient name
- Address
- Phone number
- Email address
- Date of birth
Medical Information
- Medical history
- Diagnoses
- Lab reports
- Prescriptions
- Treatment records
Financial Information
- Insurance details
- Billing records
- Payment history
Electronic Protected Health Information (ePHI)
- Electronic medical records (EMR)
- Electronic health records (EHR)
- Digital imaging
- Patient portals
- Cloud-stored healthcare data
Understanding the HIPAA Rules
Several key rules make up HIPAA compliance.
HIPAA Privacy Rule
The Privacy Rule governs how Protected Health Information may be used and disclosed.
It also grants patients rights to:
- Access their records
- Request corrections
- Receive privacy notices
- Know how their information is used
HIPAA Security Rule
The Security Rule focuses on protecting electronic Protected Health Information (ePHI).
It requires organizations to implement:
- Administrative safeguards
- Physical safeguards
- Technical safeguards
HIPAA Breach Notification Rule
Organizations must notify affected individuals and, in many cases, government authorities when a breach involving unsecured PHI occurs.
A documented incident response process is essential.
HIPAA Requirements for Healthcare Providers
Organizations should build their compliance program around these core requirements.
Administrative Safeguards
Include:
- Risk assessments
- Security policies
- Employee training
- Workforce management
- Incident response planning
Physical Safeguards
Protect facilities and devices through:
- Controlled facility access
- Locked server rooms
- Device security
- Secure disposal procedures
Technical Safeguards
Technical controls include:
- Encryption
- Multi-factor authentication
- Audit logs
- Automatic logoff
- Secure user authentication
- Data integrity monitoring
HIPAA Compliance Checklist
The following HIPAA compliance checklist provides a practical roadmap for healthcare organizations and SaaS providers.
✔ Conduct a Risk Assessment
Identify vulnerabilities affecting PHI and ePHI.
✔ Develop Written Policies
Document:
- Privacy policies
- Security procedures
- Access management
- Incident response
✔ Train Employees
Employees should understand:
- Privacy responsibilities
- Phishing awareness
- Password security
- Data handling procedures
✔ Secure Systems
Implement:
- Encryption
- Endpoint protection
- Firewalls
- Secure cloud infrastructure
- Backup solutions
✔ Manage User Access
Grant access only to employees who require patient information to perform their roles.
Apply the principle of least privilege.
✔ Monitor Systems
Continuously review:
- Audit logs
- Security alerts
- User activity
- System vulnerabilities
✔ Sign Business Associate Agreements (BAAs)
Healthcare organizations should establish Business Associate Agreements with vendors handling PHI.
✔ Perform Regular Compliance Reviews
HIPAA compliance requires continuous improvement rather than one-time implementation.
HIPAA Compliance for SaaS Companies
Many SaaS companies mistakenly assume HIPAA only applies to hospitals.
If your software stores, processes, or transmits Protected Health Information, your company may qualify as a Business Associate.
Examples include:
- Electronic Health Record (EHR) platforms
- Patient engagement software
- Appointment scheduling tools
- Medical billing applications
- Telemedicine platforms
- Healthcare CRM systems
- AI-powered clinical software
Best Practices for SaaS Companies
Successful HIPAA compliance for SaaS companies includes:
- Secure cloud architecture
- Encryption at rest and in transit
- Role-based access control
- Comprehensive logging
- Vendor security reviews
- Regular penetration testing
- Employee security awareness training
- Disaster recovery planning
Privacy and security should be incorporated into product development from the beginning.
Real-World Example
Imagine a SaaS startup offering appointment scheduling software to hospitals.
The platform stores:
- Patient names
- Contact details
- Appointment history
- Insurance information
- Medical reminders
In order to be HIPAA compliant, the firm does the following:
- It encrypts all the information that is either stored or transmitted.
- It provides role-based access control.
- It creates audit trails.
- It Signs Business Associate Agreements with its health care clients.
- It conducts annual risk assessments.
- It trains its staff about HIPAA requirements.
- It develops an incident response plan.
These measures help protect patient information while meeting regulatory expectations.
Common HIPAA Compliance Mistakes
Organizations frequently encounter compliance issues due to preventable mistakes.
Common examples include:
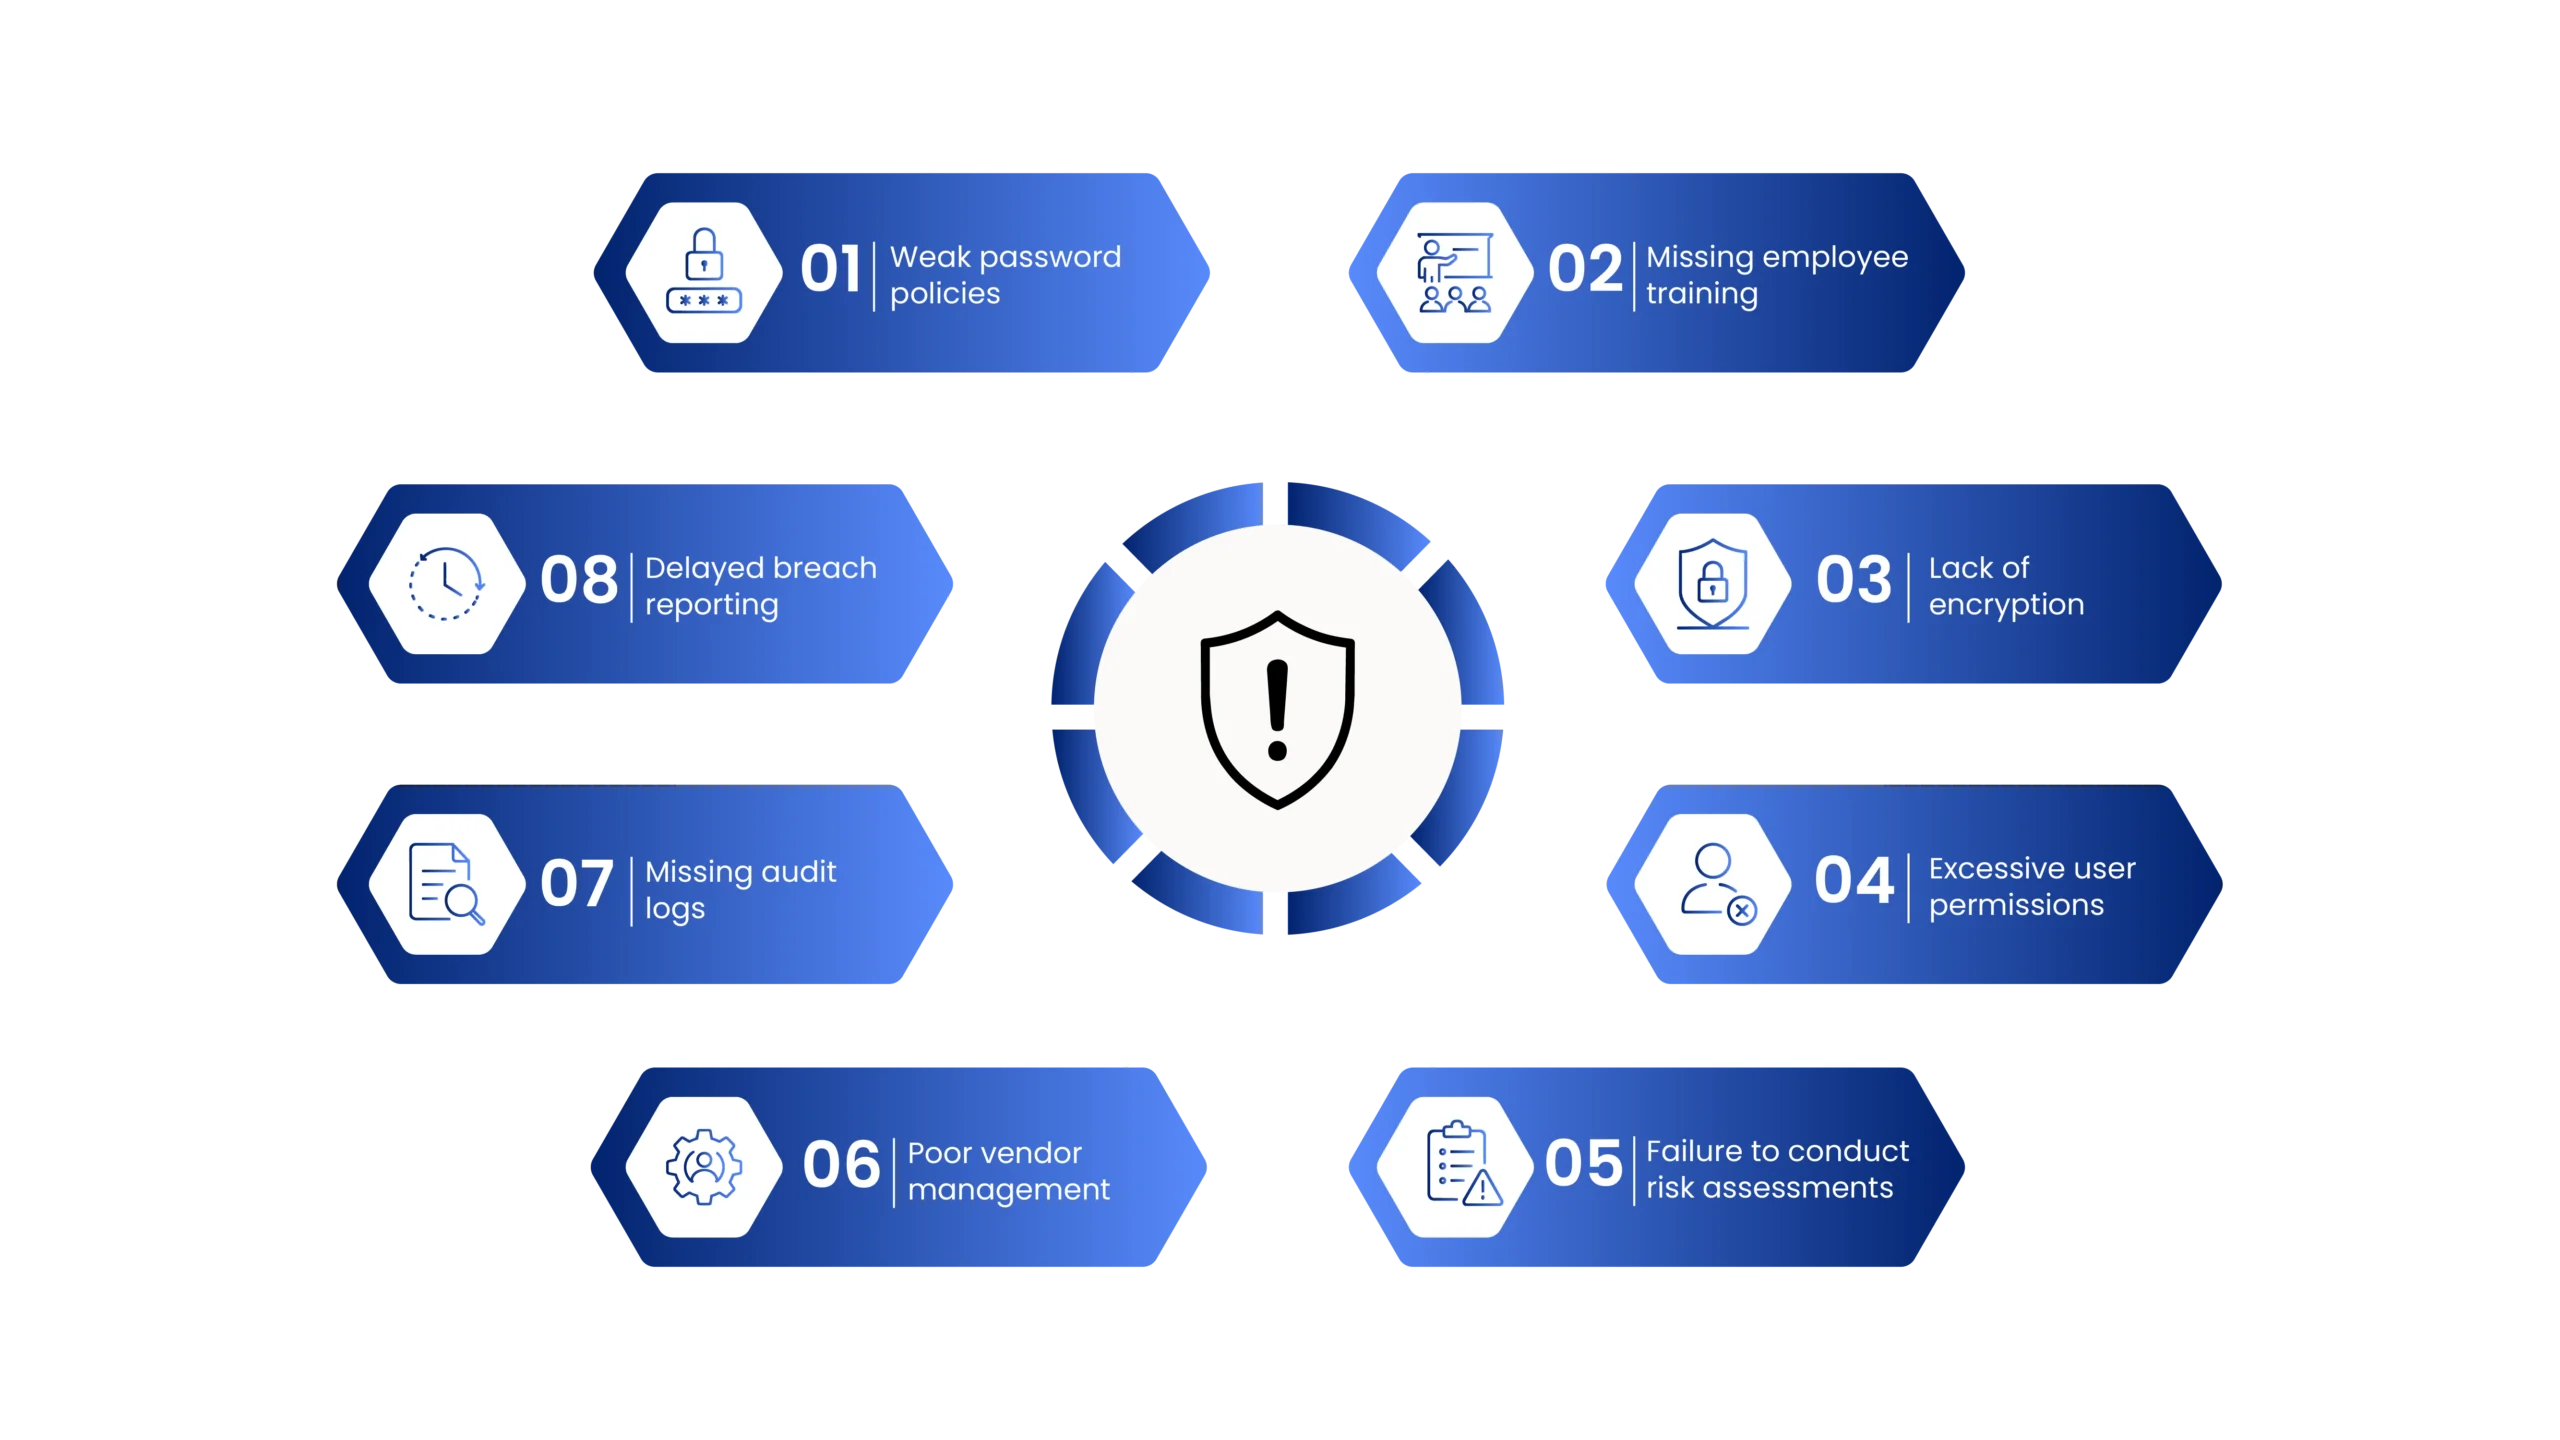
Addressing these gaps significantly improves security and compliance.
Why SOCLY.io Makes It Easier To Be HIPAA Compliant
Being HIPAA compliant can be difficult for healthcare organizations as well as SaaS providers when conducting risk assessments, implementing security controls, documenting policies, and performing ongoing compliance monitoring. SOCLY.io makes it easy to become HIPAA compliant with a platform that can help organizations in assessing their security posture, collecting centralized evidence, tracking compliance obligations, and maintaining compliance readiness at all times. For SaaS startups servicing the healthcare sector and existing healthcare organizations, SOCLY.io allows them to make their HIPAA compliance easier and more efficient.
Frequently Asked Questions (FAQs)
1. What is HIPAA and why is it important?
HIPAA is an act in the United States that ensures the safety of the health care information of the patients in terms of their privacy and the safety of data management
2. Who must comply with HIPAA?
There are a number of organizations that are known as covered entities including insurance companies, businesses associated with healthcare, clinics, and other facilities that must be HIPAA compliant.
3. What are the HIPAA requirements for healthcare providers?
HIPAA requirements for health care professionals:
Health care professionals should implement security measures including administrative, physical and technical safeguards; perform risk assessment; educate employees; protect electronic Protected Health Information and document policies and procedures.
4. How can healthcare organizations become HIPAA compliant?
The organization needs to conduct risk assessment, develop security policies, provide training for employees, encrypt confidential data, have continuous monitoring of systems, and check for compliance.
5. Is HIPAA applicable to SaaS vendors?
Yes. SaaS vendors have to be HIPAA-compliant if they use their software for storing, processing or transmitting PHI on behalf of healthcare organizations.
6. What is a part of a HIPAA Compliance Checklist?
A HIPAA Compliance Checklist usually covers risk assessment, policies and procedures, employee training, encryption, access control, audit trail, vendor management, Business Associate Agreements, and continued compliance.
Final Thoughts
As cloud computing, AI and digital healthcare experiences become ever more common, protecting health data has never been more critical. With the help of HIPAA compliance, healthcare companies and SaaS businesses get an opportunity to provide necessary protection to their patient information, lower cybersecurity risks and create sustainable trust.
Following the guidelines on HIPAA compliance for healthcare organizations, using a practical HIPAA compliance checklist and incorporating security into all aspects of operations helps organizations to be more resilient and follow the regulations.
For any healthcare provider, health-tech startup or SaaS company working with the medical industry, HIPAA compliance is a necessary step to take today in order to ensure success in the future.
Looking to Enhance Your HIPAA Compliance?
Protect your patient data and comply with the regulations by developing a HIPAA compliance strategy.
Visit Our Website to learn more about HIPAA compliance, Book a Consultation with our experts or Contact Us for assistance.