Categories
DPDPA

DPDP Rules 2025: Key Requirements and What Businesses Need to Know

DPDP Rules 2025: Key Requirements and What Businesses Need to Know
DPDP Rules 2025: Key Requirements and What Businesses Need to Know

DPDP Rules 2025: Key Requirements and What Businesses Need to Know

>DPDP Rules 2025: Key Requirements and What Businesses Need to Know

DPDP Rules 2025: Key Requirements and What Businesses Need to Know

Learn how the DPDP Rules 2025 translate India's data protection law into practical compliance requirements, helping businesses manage consent, protect personal data, meet retention obligations, and prepare for enforcement.

DPDP Rules 2025: Key Requirements and What Businesses Need to Know

DPDP Compliance

India’s Digital Personal Data Protection Rules 2025 are finally here, and if you run a business that handles personal data of Indian users, this directly affects you.

The DPDP Rules 2025 are meant to bridge any shortcomings in the DPDP Act 2023, translating vague provisions into something actionable. Think of the Act as the “what” and the Rules as the “how.” With the DPDP Rules 2025 now in effect, there is no more excuse for businesses to delay figuring out what compliance entails.

This document will provide compliance professionals, legal advisors, startup founders and business owners with a comprehensive and practical understanding of DPDP Act Rules 2025.

Here’s what you’ll find inside:

  • What the DPDP Rules 2025 actually say – an overview of the main points covered, including the need for consent, data retention policies, and how the Rules are different from the Act
  • Special obligations you may not have heard about – including specific protections for children’s data and persons with disabilities that carry their own compliance requirements
  • What to do right now – the operational steps your business needs to take before enforcement kicks in, plus a look at the penalties if you don’t

Let’s get into it.

Understanding the DPDP Rules 2025

What the DPDP Rules 2025 Are and Why They Were Notified

The DPDP Rules 2025 are the set of operational rules released by the Ministry of Electronics and Information Technology (MeitY) that make the DPDP Act, 2023 functional. Consider them to be the guidelines that convert broad principles from legislation into concrete, actionable procedures of data protection that include data collection, processing, security, retention, and deletion.

This was not an initiative taken in isolation by the Ministry. The MeitY received 6,915 public submissions and organized consultations in Delhi, Mumbai, Guwahati, Kolkata, Hyderabad, Bengaluru, and Chennai before releasing them, which makes it one of the most consultative processes of regulation in India. With DPDP Rules 2025 explained through this level of public engagement, the framework carries significant institutional weight.

Source: Digital Personal Data Protection Rules, 2025 — full text (MeitY)

How the DPDP Rules 2025 Relate to the DPDP Act 2023
DPDP Rules 2025 Relate to the DPDP Act 2023

The Act sets out the principles; the Rules set the mechanics. While the Act defines rights and obligations at a high level, the Rules specify how those obligations must actually be met, a distinction explored in greater depth in the next section.

Why These Rules Matter for Businesses Operating in India

The New DPDP Rules 2025 make compliance non-negotiable. Enforcement is no longer theoretically defined, deadlines now exist. Crucially, these Rules apply equally to Indian and foreign businesses serving Indian users, regardless of where they’re incorporated.

DPDP Act 2023 vs. DPDP Rules 2025: What’s the Difference

A. Key Distinctions Between the Act and the Rules

DPDP Act 2023

DPDP Rules 2025

Passed August 2023; Presidential assent 11 August 2023

Notified 13 November 2025 via G.S.R. 846(E)

Defines rights of Data Principals

Specifies how those rights are operationalised

Establishes penalty structure (up to ₹250 crore)

Defines consent notice formats (Rule 3)

Sets principles: purpose limitation, data minimisation

Details breach notification procedures (Rule 7)

Creates the Data Protection Board

Prescribes data retention periods (Third Schedule)

Think of the DPDP Act 2023 as the “what” — the legal framework, rights, and consequences. The Rules are the “how” — the practical mechanisms your organisation must implement.

Sources: DPDP Act, 2023 — full text (MeitY) · DPDP Rules, 2025 — full text (MeitY)

B. Why You Need Both to Achieve Full Compliance

Reading only the Act tells you that consent is required  but not the exact format, language requirements, or approved verification methods. Reading only the Rules without the Act leaves you without the legal context for penalties and rights.

“DPDP Act Rules 2025” and “DPDP Rules 2025” are different ways to describe the exact same set of rules, and are interchangeable in all official communications.Now that this naming confusion is resolved, understanding both documents together gives your compliance programme its complete legal and operational foundation.

When Were the DPDP Rules 2025 Notified? Full Timeline

Official Notification Date

When were the DPDP Rules 2025 notified? The DPDP Rules 2025 were notified in the Official Gazette on 13 November 2025, via Gazette notification G.S.R. 846(E), with MeitY’s public announcement following the next day, on 14 November 2025. This marks India’s formal entry into a structured, rights-driven data protection era.

Source: DPDP Rules, 2025 official notification (PIB press release)

Phase I – What’s Effective Immediately

The DPDP Rules 2025 effective date begins from the notification date itself. Rules 1, 2, and 17–21 came into force immediately, establishing the Data Protection Board’s purpose, appointment process, and operational functioning. You don’t get a grace period here — these obligations apply from day one.

Phase II – Consent Manager Registration (~12 Months)

Approximately one year from publication (~November 2026), Rule 4 activates. This is your DPDP Rules 2025 implementation date for Consent Manager registration, eligibility criteria, and oversight requirements. If your business involves managing user consent at scale, this deadline directly affects your operating model.

Full Compliance Obligations (~18 Months)

Around 18 months from publication (~May 2027), Rules 3, 5–16, 22, and 23 come into full effect covering the bulk of day-to-day Data Fiduciary obligations. This is the deadline you should anchor your compliance roadmap around.

Phase

Timeline

Key Rules Activated

Phase I

Immediate (13 Nov 2025)

Rules 1, 2, 17–21

Phase II

~12 months (~Nov 2026)

Rule 4

Full Compliance

~18 months (~May 2027)

Rules 3, 5–16, 22, 23

Please note that a proposal to reduce the 18-month period to 12 months has informally been made by MeitY. At the time of writing, there is no formal notification of this through the Gazette. Please take the 18-month timeframe into account, but watch out for any official communication in case it changes.

Key Highlights of the DPDP Rules 2025

A. Who the Rules Apply To

Understanding DPDP Rules 2025 applicability is your first step toward compliance. The Rules apply to:

  • Data Fiduciaries – entities that determine the purpose and means of processing personal data
  • Data Processors – entities processing data on behalf of fiduciaries
  • Significant Data Fiduciaries (SDFs) – those designated by the government, carrying heightened obligations

Critically, there is no turnover or company-size threshold. Whether you are a startup or an enterprise, the Rules apply equally to your organization based on your processing activities.

B. Consent Notice Requirements

Each Data Fiduciary needs to provide a separate and distinct notice of consent, which shall be drafted in language that is clear and simple to understand by the Data Principal. This notice cannot be buried inside your general terms of service or privacy policy. It must itemize the specific purposes for which personal data is being collected and processed.

C. Data Protection Board Structure and Functioning

The Data Protection Board is an office functioning digitally wherein everything from filing of complaints to conducting proceedings would take place online. This streamlined structure makes it accessible and efficient for handling grievances under the DPDP Rules 2025.

D. Appellate Tribunal and Appeal Process

If you disagree with a Board decision, the Rules establish a structured appeal procedure through a designated Appellate Tribunal, a procedural detail most compliance guides overlook but one that significantly affects your risk management strategy.

Core Compliance Requirements Under DPDP Rules 2025

A. Data Fiduciary Obligations and Responsibilities

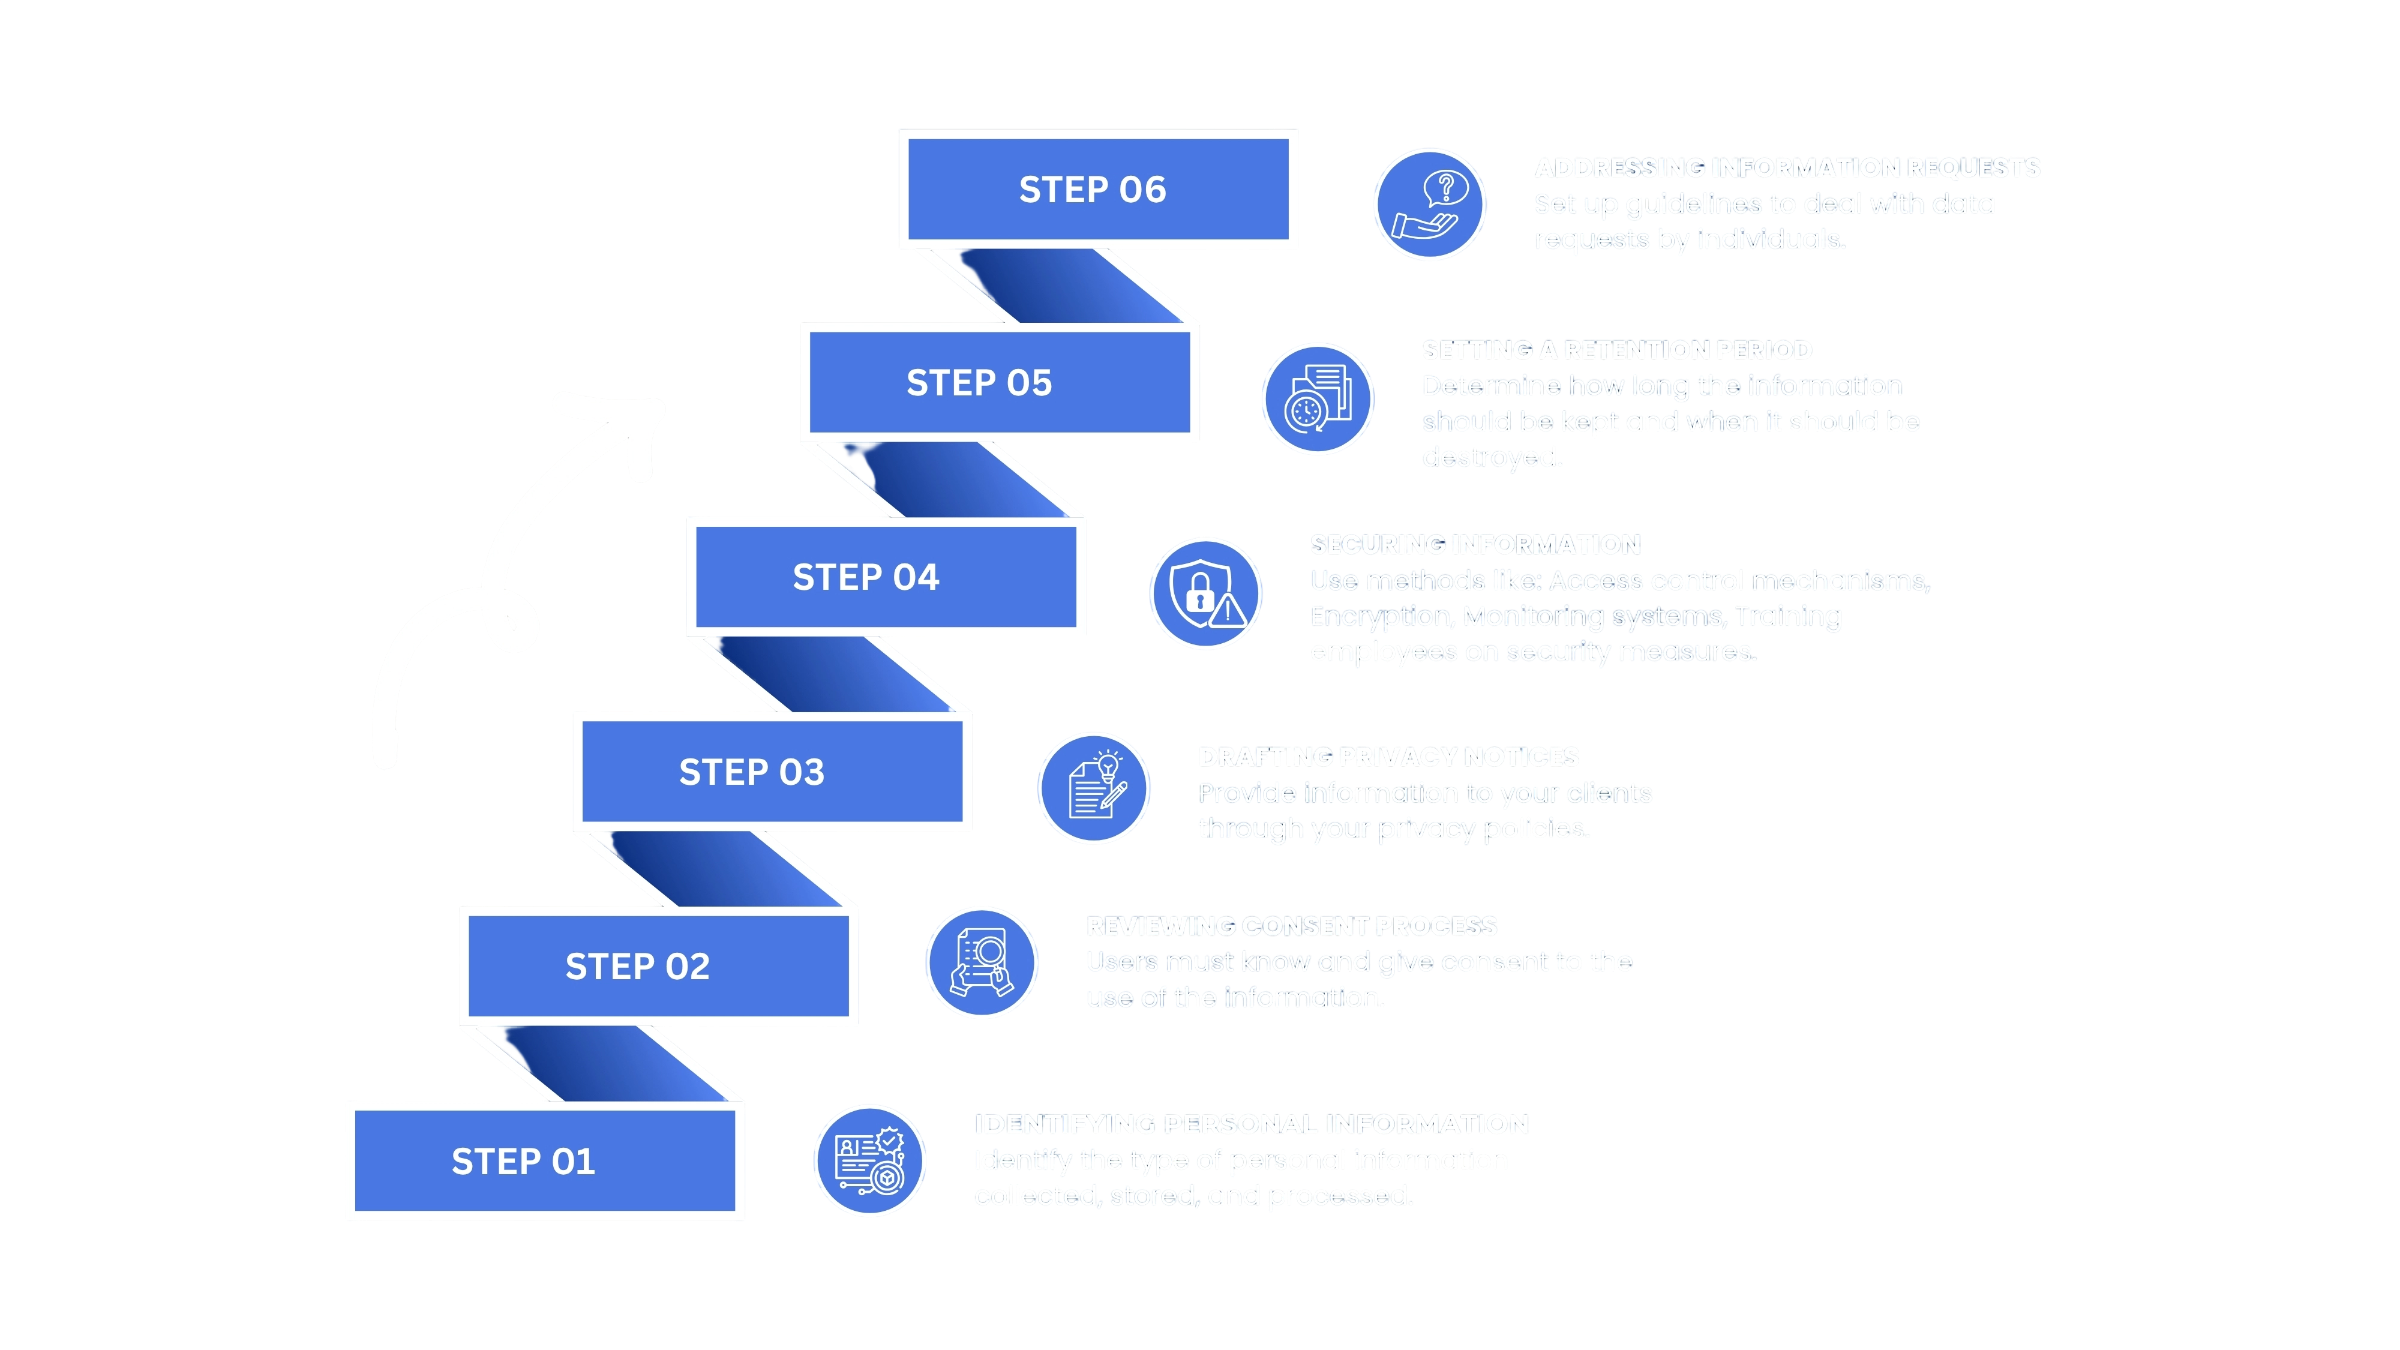
As a Data Fiduciary, you must collect only the personal data necessary for a clearly defined purpose, nothing beyond that. The DPDP Rules 2025 hold you accountable for ensuring data is used strictly within that stated purpose and deleted once it is no longer needed.

B. Consent Management and Lawful Basis for Processing

Your consent mechanisms must meet a high standard. Consent under DPDP Rules 2025 must be:

  • Free – no coercion or conditional access
  • Specific – tied to a defined purpose
  • Informed – clearly explained before collection
  • Unconditional and unambiguous – no bundled or implied consent
  • Easy to withdraw – as simple as it was to give

C. Data Principal Rights Businesses Must Uphold

You are obligated to honour the following rights for every individual whose data you process:

  • Access – provide data summaries upon request
  • Correction – update inaccurate personal data
  • Erasure – fulfil erasure requests within 90 days (Rule 14), including data held by your Data Processors
  • Grievance Redressal – maintain a functional complaint mechanism

D. Cross-Border Data Transfer Restrictions and Approvals

With this in mind, cross-border transfers are permitted by default under DPDP Rules 2025. No countries are restricted yet, but the Government retains authority to block specific destinations. You should monitor official notifications regularly to stay ahead of any future restrictions.

Special Provisions for Children’s Data and Persons with Disabilities

A. Verifiable Parental Consent Requirements

Before processing personal data of any child under 18  or a person with a disability who has a lawful guardian you must obtain verifiable parental or guardian consent. This is a non-negotiable prerequisite under the DPDP Rules 2025, not a best-practice recommendation. Non-compliance here carries penalties of up to ₹200 crore.

B. DigiLocker-Based Identity Verification

Here’s a detail most compliance guides overlook: Rule 10 of the DPDP Rules 2025 explicitly permits DigiLocker-based verification as a mechanism to confirm a parent’s identity and establish the parent-child relationship. This gives you a practical, government-backed method to meet the verifiability requirement without building complex custom verification infrastructure.

C. Prohibited Practices: Tracking, Profiling, and Targeted Ads

As a Data Fiduciary, you are strictly prohibited from:

  • Tracking children’s online behaviour
  • Profiling children for any purpose
  • Serving targeted advertisements directed at children

In addition to the above constraints on processing, you need to implement technical age-gate measures to ensure that children do not access services inappropriate for their age group. This is not an optional set of controls but one expected by regulators to be backed up with technical solutions.

Data Retention Requirements Under the Third Schedule

Sector-Specific Retention Periods

The Third Schedule of the DPDP Rules 2025 lays out clear data retention timelines for large-scale platforms. Once the purpose for which data was collected is fulfilled, these platforms must erase personal data within the defined period with no exceptions.

Here’s what the current retention periods look like:

Platform Type

User Threshold

Retention Period

E-commerce platforms

2 crore+ registered users

3 years from last transaction or login

Online gaming platforms

50 lakh+ registered users

3 years from last transaction or login

Social media platforms

2 crore+ registered users

3 years from last interaction

Note: Always verify these figures against the latest official gazette notification before building your compliance calendar, as rules may be updated.

Which Businesses This Applies To

This schedule does not apply to every business operating in India. Your obligations under the Third Schedule kick in only if your platform crosses the user thresholds specified above.

If you run a small or mid-sized operation well below these numbers, this particular schedule doesn’t bind you though your general data minimization and erasure duties under DPDP Rules 2025 still apply.

Operational Steps Businesses Must Take Immediately
Operational Steps Businesses

A. Conducting a Data Audit and Mapping Exercise

To begin with, it is necessary to create a comprehensive list of all the personal data collected, stored, processed, and disclosed by the organization. The process will provide an understanding of all the areas where there are vulnerabilities. The inventory created is going to serve as the basis for all the further actions related to compliance with the DPDP Rules 2025.

B. Updating Privacy Notices and Consent Mechanisms

Your privacy notices should now be written in clear language and not be too general and vague. You need to review all data gathering points and ensure that consent is sought for purposes which are clearly stated prior to any processing. It should also be easy to withdraw consent.

C. Establishing a Grievance Redressal System

Establish an exclusive communication channel through which data principals can communicate their concerns and requests for correction. The DPDP Rules 2025 have specified specific deadlines for the response to such queries. This can be as simple as a ticketing system with an escalation route.

D. Appointing a Data Protection Officer Where Required

A DPO is mandatory only for Significant Data Fiduciaries as designated by the government. That said, many businesses voluntarily appoint one to manage compliance proactively and build trust with customers, a smart move even if you’re not legally required to do so.

Penalties and Enforcement Businesses Must Prepare For

Financial Penalties for Non-Compliance

The DPDP Rules 2025 come with a sharp penalty structure you cannot afford to ignore. Here’s what’s at stake:

Violation Type

Maximum Penalty

Security safeguard failures

₹250 crore

Breach notification failures

₹200 crore

Children’s data violations

₹200 crore

Significant Data Fiduciary failures

₹150 crore

General non-compliance

₹50 crore

These aren’t theoretical numbers, they’re the actual caps defined under Schedule I of the DPDP Act, 2023.

Source: Schedule I, DPDP Act, 2023 (full text, MeitY)

Regulatory Authority Powers and Oversight Mechanisms

The Data Protection Board of India holds real teeth. It can investigate complaints, summon records, conduct inquiries, and issue binding decisions against your organization. The Board also has the authority to impose penalties and direct remediation all without requiring a court order.

How to Reduce Risk of Enforcement Action

Getting your compliance in order now costs a fraction of what a breach investigation or penalty proceeding will. When you build data governance practices proactively  consent management, breach response, retention policies, you’re not just avoiding fines; you’re protecting your customers and your reputation. Waiting until something goes wrong is always the more expensive option.

How SOCLY.io Simplifies DPDP Rules 2025 Compliance
DPDP Rules 2025 Compliance

Automating Consent Tracking and Data Subject Requests

Manually tracking consent across thousands of users is a nightmare waiting to happen especially when the DPDP Rules 2025 require you to respond to erasure and access requests within a 90-day window. 

SOCLY.io replaces those messy spreadsheets and email chains with automated consent logs that update in real time. When a Data Principal submits a request, the platform routes, tracks, and timestamps it automatically, so you never miss a deadline.

Integrating DPDP Requirements into Existing Security Frameworks

If your organization already runs on SOC 2 or ISO 27001 controls, you don’t need a separate compliance stack for DPDP. SOCLY.io maps DPDP Act Rules 2025 obligations directly onto your existing security framework, giving you a single dashboard to manage data protection requirements alongside your current controls. This means less duplication, fewer gaps, and a cleaner audit trail.

For a deeper look at how SOCLY.io handles end-to-end DPDP compliance automation from breach notifications to Data Fiduciary obligations. 

check out our dedicated DPDP compliance guide. 

If you’re also working on ISO 42001, SOC 2, or ISO 27001, those guides cover how each framework overlaps with your DPDP obligations.

Frequently Asked Questions

When Were the DPDP Rules 2025 Notified? 

The DPDP Rules 2025 were notified in the Official Gazette on 13 November 2025, via Gazette notification G.S.R. 846(E), with MeitY’s public press release following on 14 November 2025. (The draft Rules were published for consultation to the public on 3 January 2025. This was the draft stage, and not the final notice of rules.) The Rules will now be implemented through three phases up to May 2027.

What Are the Requirements for Compliance with the DPDP Act in India? 

Your compliance checklist starts with obtaining free, informed, and specific consent before processing personal data. You also need robust security safeguards, a clear grievance redressal mechanism, and a process to honor data principal rights including the right to access, correct, and erase personal data. Head back to the Core Compliance Requirements section for a full breakdown.

Can You Provide a Summary of the DPDP Rules 2025? 

The Digital Personal Data Protection Rules, 2025 further elaborate on the workings of the DPDP Act, 2023. The Rules deal with issues related to the management of consent, data protection for children, security, and retention of personal data. Significant Data Fiduciaries have to adhere to additional requirements such as conducting audits and DPIAs.

What’s the Difference Between the DPDP Act and DPDP Rules? 

The DPDP Act 2023 sets the legal framework and broad principles. The DPDP Rules 2025 are the operational rulebook spelling out exactly how your business must implement those principles day to day.

Who Is a Significant Data Fiduciary? 

Significant Data Fiduciary is an organization that is designated by the government as a data fiduciary due to the nature, quantity, or risks associated with the data being processed. If your business qualifies for being a significant data fiduciary, you have the obligation of appointing a Data Protection Officer and conducting DPIAs every year.

The DPDP Rules 2025 represent a major change in the way that businesses functioning within the Indian jurisdiction need to deal with personal data. From getting explicit consent to handling data about children, creating retention timelines, and facing stringent fines – the requirements of compliance are very real, very detailed, and very non-negotiable. If you are a business in India – regardless of your size – you cannot ignore this anymore.

Getting compliant doesn’t have to be difficult. It’s all about being aware of the requirements of the laws, taking the appropriate actions, and  leveraging platforms built for this purpose. You can build a strong data privacy framework that protects your users and your business. 

Tools like SOCLY.io are designed to simplify exactly this journey, helping you stay on top of your DPDP obligations without losing focus on what matters most: running your business with trust and accountability at its core.

Ready to Simplify Your Compliance Journey?
Categories
DPDPA

Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

>Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

Why the DPDP Act Matters for Indian Startups and SaaS Companies?

Learn how the DPDP Act helps Indian Start-ups and SaaS companies protect customer data, strengthen privacy practices, reduce data security risks, and build trust with customers.

Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

DPDP Act Matters for Indian Startups

For Indian startups, customer data is one of their most valuable business assets. It is also a major responsibility.

The DPDP Act for startups makes data privacy an important business priority. Startups shouldn’t wait until they grow into big businesses to handle privacy.

It is more important for SaaS companies. An average SaaS company could be collecting data such as customer names, emails, phone numbers, employee details, payment methods, and other forms of data.

The startups who have knowledge about Digital Personal Data Protection Act early will benefit in terms of good privacy practices and risk reduction.

What Is the DPDP Act?

Digital Personal Data Protection Act 2023 (DPDP Act) is the primary legislation in India for regulating digital personal data.

This Act specifies the obligations of enterprises for processing digital personal data. Besides, it establishes individual rights over their personal data.

In plain language, the DPDP Act obliges enterprises to know:

  • What personal data they collect
  • Why they collect it
  • How they use it
  • How they protect it
  • Who they share it with
  • How long they keep it
  • What they do when something goes wrong

The above issues should form part of business practice. This is more so to startups who handle customer information in bulk.

Why Is the DPDP Act Important for Indian Startups?

Many startups believe that data privacy is mainly a concern for large companies. That approach is becoming difficult to maintain.

Startups may start off with just a few people using the product. But soon enough, they may have thousands or even millions of users.

As the organization expands, the personal information increases. Fixing privacy problems later can be costly.

The DPDP Act for startups matters for several key reasons.

1. Startups Handle More Personal Data Than They Realize

A SaaS startup may collect personal data through many different systems.

For example:

  • Website forms
  • Product registrations
  • User accounts
  • Customer support
  • Marketing campaigns
  • HR systems
  • Analytics tools
  • Payment systems
  • CRM platforms

Data collection may not be the main purpose of the business. Still, personal data can exist across different parts of the technology stack. Knowing where this data exists is the first step toward protecting it.

2. Privacy Builds Customer Trust

Consumers want to know how organizations treat their personal information. It may influence their purchasing decisions. It becomes especially relevant in the case of SaaS startups offering products to other enterprises.

Enterprise buyers may ask vendors about:

  • Data management
  • Security controls
  • Breach response
  • Compliance practices

Strong privacy practices can therefore become a competitive advantage for Indian startups.

3. Privacy Risks Can Become Business Risks

A data privacy issue can create problems beyond regulatory concerns.

For a startup, a personal data incident could lead to:

  • Customer complaints
  • Loss of customer trust
  • Contractual problems
  • Higher security costs
  • Business disruption
  • Reputation damage

Building privacy practices early can help startups reduce these risks.

Key DPDP Act Requirements Startups Should Understand

The Act introduces several concepts that SaaS companies should understand when building their privacy programs.

Consent and Lawful Processing

Organizations need a valid legal basis to process personal data. This may include obtaining consent where required.

There must be meaningful consent related to an intended use.

For instance, when a software-as-a-service firm collects an individual’s email address to create a user account, there must be a specific reason for doing this.

Notice and Transparency

Organizations need to communicate to individuals how their personal data will be used.

The privacy notice provided by organizations needs to be understandable.

A startup should clearly explain:

  • What data it collects
  • Why it collects the data
  • How it uses the data
  • How individuals can exercise applicable rights

Data Security

Organizations should use reasonable security safeguards to protect personal data.

For SaaS companies, these safeguards may include:

  • Access controls
  • Authentication
  • Encryption
  • Security monitoring
  • Vulnerability management
  • Employee security training
  • Incident response procedures
  • Secure software development practices

The right controls will depend on the company’s size, systems, risks, and data processing activities.

Data Retention

Startups should not keep personal data forever without a valid reason.

A practical data retention process should define:

  1. What data is stored
  2. Why the data is needed
  3. How long the data should be kept
  4. When the data should be deleted or disposed of

This is especially important for SaaS companies.

They may keep information from former customers or inactive accounts. Clear retention rules can help prevent unnecessary data storage.

DPDP Compliance for SaaS Companies

DPDP compliance for SaaS companies involves more than publishing a privacy policy.

A SaaS application can use many systems and third-party vendors. Each system may process personal data.

For example, customer information may move through:

Website
CRM
SaaS applications
Cloud infrastructure
Analytics platform
Analytics platform
Customer support system

Each part of this data flow should be considered when building a privacy program.

Map Your Data

Start by identifying the personal data your business collects.

Then, identify where that data goes.

Create a simple data inventory that includes:

  • Data type
  • Data source
  • Processing purpose
  • Storage location
  • Access permissions
  • Third-party recipients
  • Retention period

A data inventory gives your team a clearer view of its data environment.

Review Third-Party Vendors

SaaS companies often rely on third-party vendors for:

  • Hosting
  • Analytics
  • Payments
  • Communications
  • Customer support
  • Other business activities

Review each vendor that processes personal data.

Check:

  • What data the vendor receives
  • Why the vendor processes it
  • What security measures it uses
  • What contractual protections apply
  • What happens when the relationship ends

Vendor management should be part of your overall privacy and security program.

How Indian Startups Can Comply With the DPDP Act

Indian startups can become compliant with DPDPA on a phased basis.

Start with getting an idea of the kind of personal data collected by your firm. Next, examine the processes involved with such personal data.

Step 1: Identify Personal Data

Create a list of the personal data your organization processes, stores, or transfers.

Include data managed through:

  • Employees
  • Applications
  • Databases
  • Vendors
  • Marketing systems

This gives your team a starting point for its privacy program.

Step 2: Understand Why You Collect It

The purpose of every main type of personal data should be known.

Ask a basic question:

Is this data needed at all? And if some data is not needed, think about whether it is necessary to collect it. Reduced data collection will decrease privacy threats as well.

Step 3: Review Your Privacy Notices

Check your privacy notices from time to time. Ensure that they provide clear information about your processing operations.Don’t use confusing terminologies which might be difficult for the users to comprehend.

Step 4: Establish Data Retention Rules

Establish time frames for keeping each category of personal data. Develop policies on deleting information once it is no longer required. This will involve the processes for handling data in the systems and through the vendors using the data.

Step 5: Strengthen Security Controls

Review the technical and organizational measures used to protect personal data.
Depending on your environment, these may include:

  • MFA
  • Role-based access
  • Encryption
  • Logging
  • Vulnerability management
  • Backup procedures
  • Security awareness training

Review these controls as your startup grows and your systems change.

Step 6: Prepare for Data Breaches

Create an incident response process for personal data breaches.
Your team should know what to do when an incident occurs.

Define:

  • Who investigates the incident
  • Who makes key decisions
  • Who communicates internally
  • How affected systems are contained
  • What regulatory or contractual notifications may be required

A clear process can help your team respond faster and more consistently.

Step 7: Document Your Compliance Program

Keep records of important privacy and security activities.
Your documentation may include:

  • Privacy policies
  • Risk assessments
  • Vendor evaluations
  • Security measures
  • Compliance activities
  • Other relevant records

Good documentation can help demonstrate that your startup actively manages privacy risks.

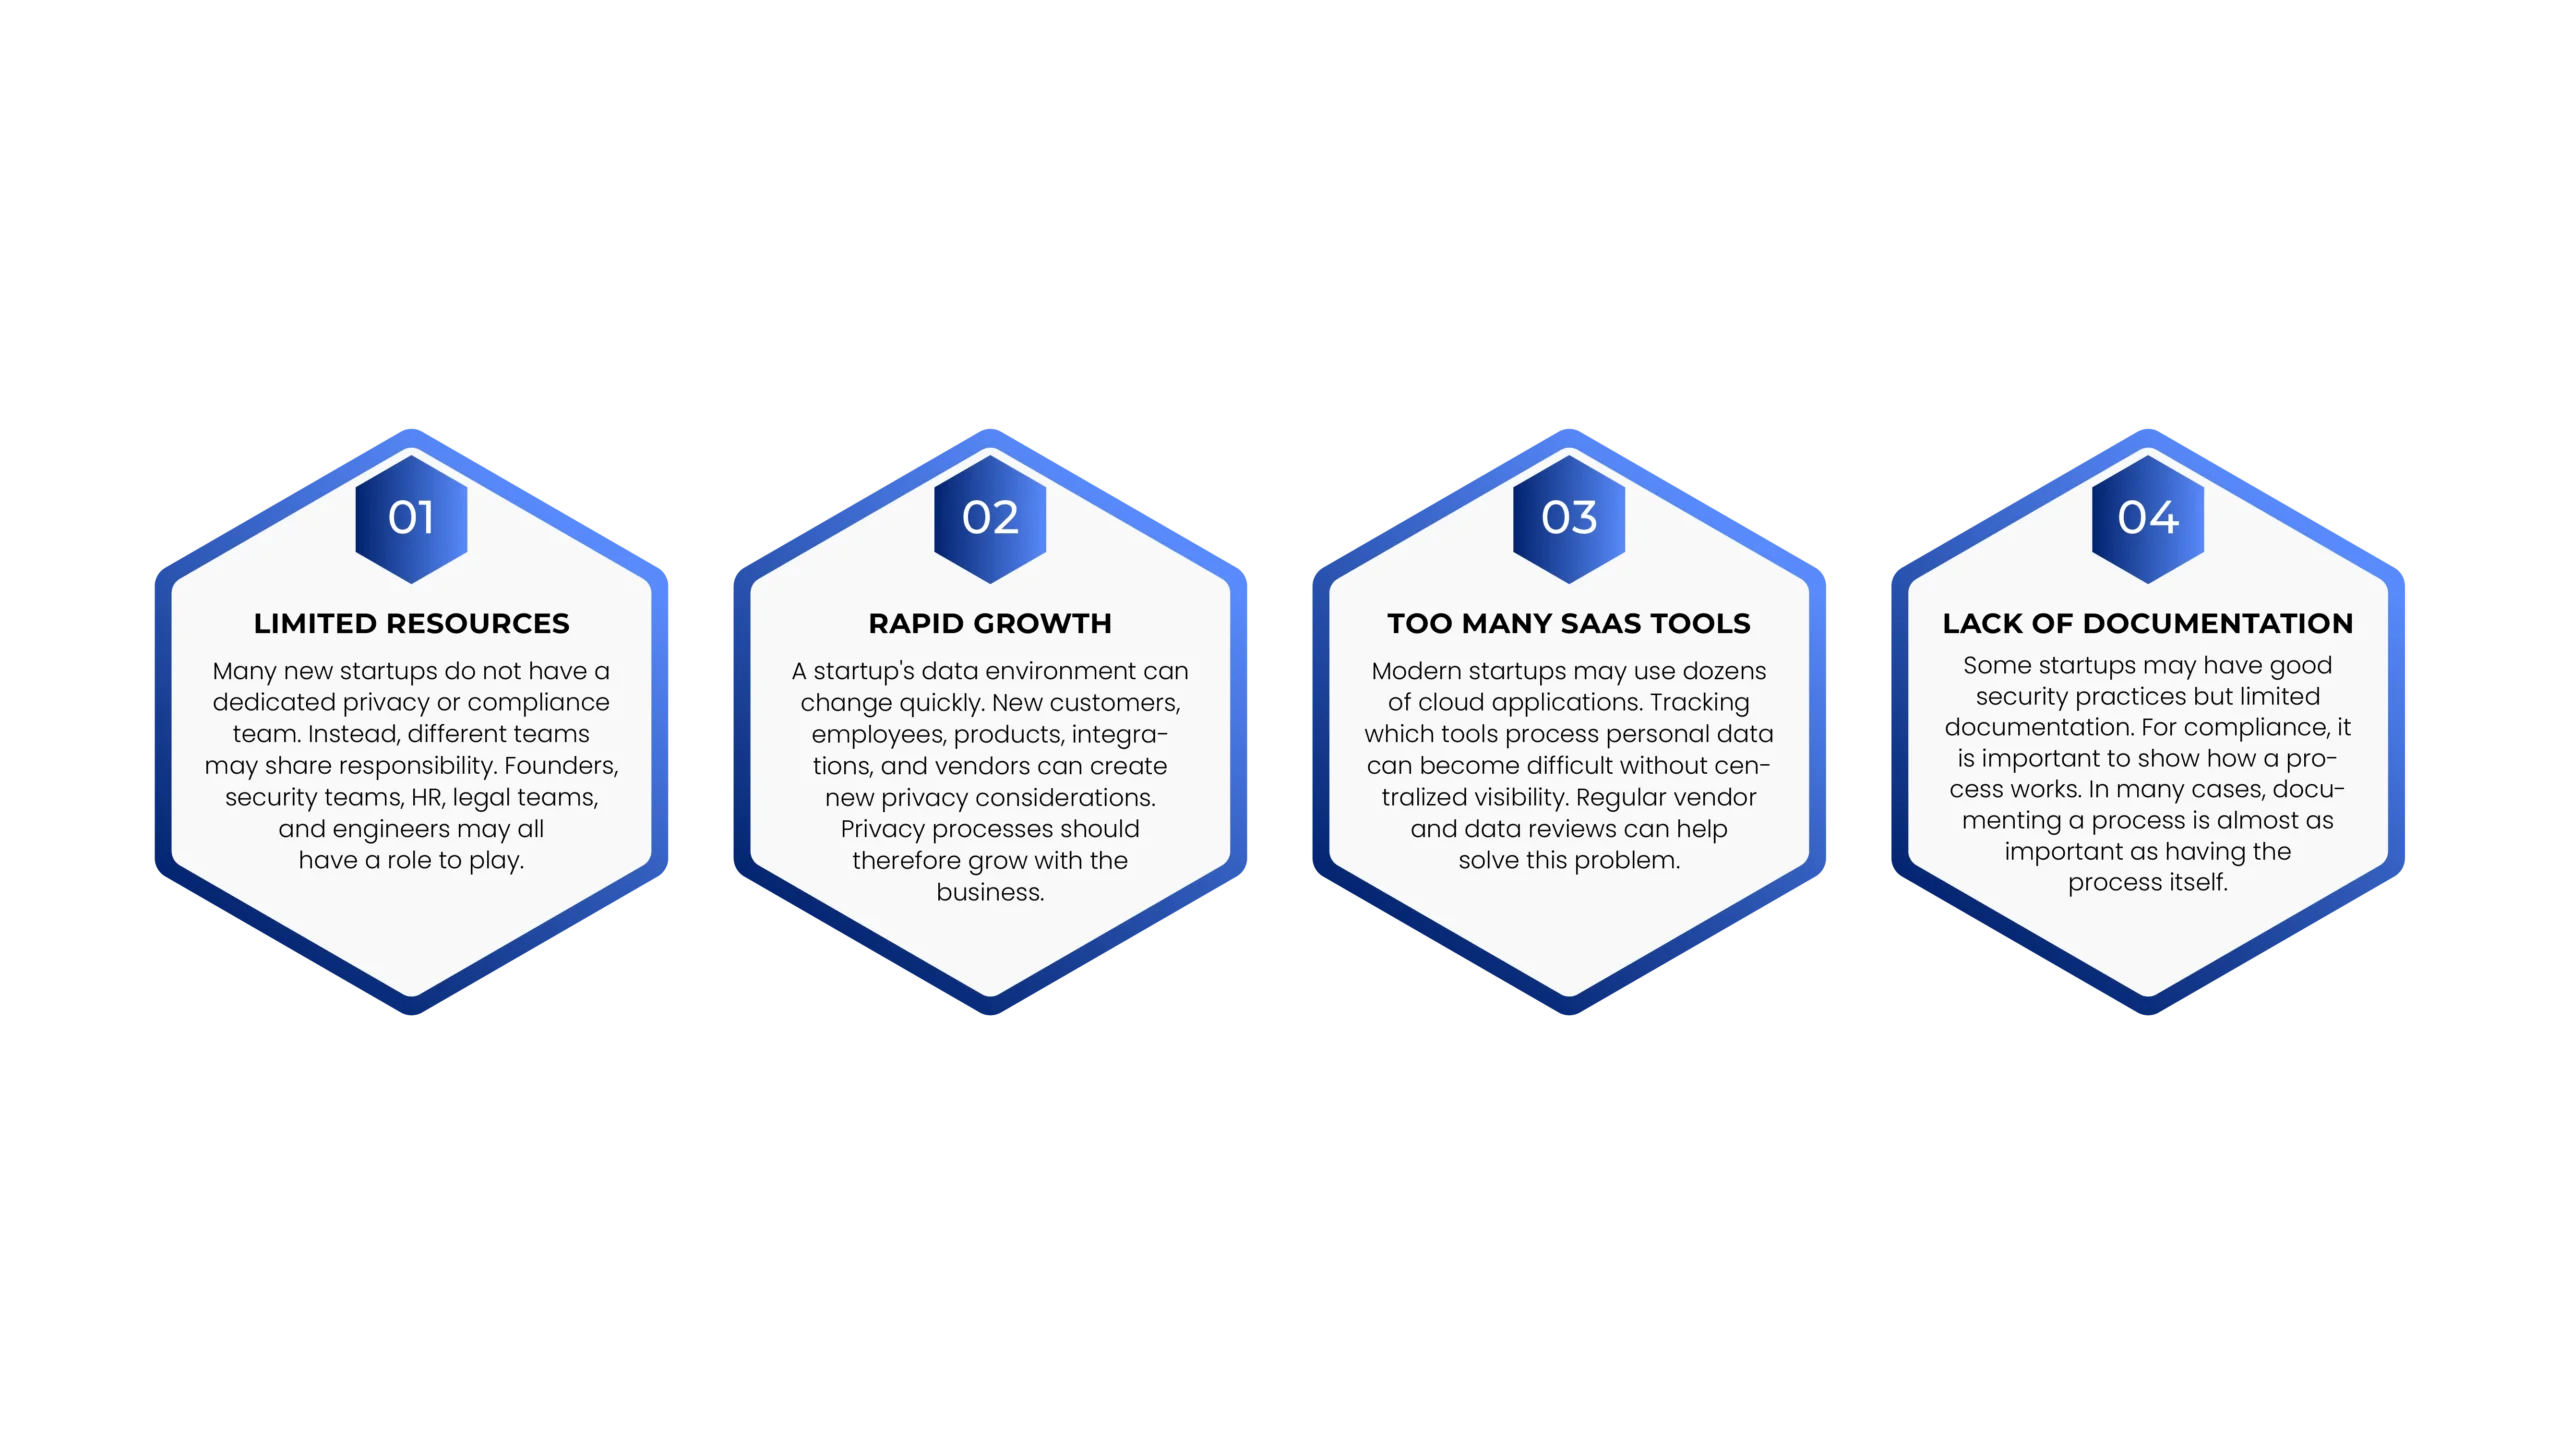
DPDP Act Compliance for Indian Startups: Common Challenges

Startups often face similar challenges when they begin their privacy journey.

DPDP Act Compliance for Indian Startups

DPDP Act vs. GDPR: Are They the Same?

The DPDP Act and the European Union’s GDPR both focus on protecting personal data. However, there are different laws.

They differ in areas such as:

  • Scope
  • Terminology
  • Individual rights
  • Organizational responsibilities
  • Regulatory requirements

Therefore, GDPR compliance does not automatically mean DPDPA compliance.

Companies should review their existing privacy framework against the requirements that apply to their Indian operations. They should then identify and address any gaps.

For SaaS companies that operate in multiple countries, a privacy program should consider the requirements of each relevant jurisdiction. This can also make customer due diligence easier.

What Happens If Startups Ignore Data Privacy?

Ignoring privacy can create problems as a startup grows.

A company may initially think:

“We’re too small for this to matter.”

However, customers, investors, enterprise procurement teams, and business partners may expect evidence of responsible data handling.

Poor privacy practices can also create operational problems.

For example, a startup may suddenly need to:

  • Respond to a customer data request
  • Investigate a data incident
  • Remove data from multiple systems
  • Review a vendor’s data access
  • Explain its data practices to an enterprise customer

Building a privacy foundation early is usually easier than fixing gaps later.

How SOCLY.io Helps With DPDP Act Compliance

Managing privacy policies, risks, controls, evidence, and compliance tasks in spreadsheets can become difficult as a SaaS startup grows.

SOCLY.io helps startups organize these activities through a more structured and centralized workflow.

With SOCLY.io, teams can:

  • Organize compliance requirements and tasks
  • Track risks and security controls
  • Manage policies and documentation
  • Monitor compliance gaps
  • Centralize evidence
  • Improve visibility into their compliance posture
  • Reduce repetitive manual compliance work

This can help startups maintain more consistent compliance processes as they grow.

The goal is not to treat compliance as a one-time project.

Instead, privacy and security should become part of regular business operations.

A Practical DPDPA Compliance Checklist for SaaS Startups

Before considering your privacy program mature, check whether your startup has addressed the following:

This checklist is not a substitute for legal advice.

However, it can provide a useful starting point for building a structured privacy program.

Frequently Asked Questions

1. Why is the DPDP Act important for Indian startups?

Indian startups usually deal with personal information of their customers, employees, prospects, and other users. Applying proper privacy principles could be beneficial for startups when dealing with such information.

2. What is DPDPA compliance for Indian startups?

The adherence to DPDPA will entail the establishment of processes in relation to collecting, utilizing, safeguarding, storing and managing digital personal data. This will depend on the organization and its operations.

3. Does the DPDP Act apply to SaaS companies in India?

The DPDP Act may be relevant to the firms managing digital personal data in India based on the applicability of the Act. SaaS firms need to consider the type of personal data that is handled by them and its processing.

4. How can Indian startups comply with the DPDP Act?

These startups can start with checking on their personal data and the use of it. They will need to check on privacy notices, consents, security, data retention, vendors, incident response, and compliance documents.

5. What kind of data does the DPDP Act protect?

The DPDP Act is concerned with personal data in a digital environment. Personal data is defined as information that is identifiable to a person. Start-ups must take into consideration their methods of collecting, storing, processing, and utilizing personal data.

6. Does DPDPA compliance require a dedicated privacy team?

Not necessarily. The requirements could vary based on the company’s size, activities, data processing techniques, and duties. For smaller startups, they can start by delegating their responsibilities for privacy and security and setting processes in place.

7. How is DPDPA compliance different from GDPR compliance?

DPDP Act and GDPR are two different regulations with different obligations and terminologies. If organizations are required to comply with both, they need to analyze each regulation independently. Adherence to one regulation does not guarantee adherence to another.

Conclusion: 

The DPDP Act for startups is not only a legal or compliance issue. It can affect product development, customer data, vendor selection, system security, and customer trust. For Indian startups, starting early is important.As your startup grows, your data environment will grow too.

Building a strong privacy foundation early can make compliance easier in the future.

Ready to organize your compliance efforts in a SaaS startup?
Categories
DPDPA

What Is the DPDPA Act? A Beginner’s Guide for Businesses

What Is the DPDPA Act? A Beginner’s Guide for Businesses

What Is the DPDPA Act? A Beginner’s Guide for Businesses

What Is the DPDPA Act? A Beginner’s Guide for Businesses

>What Is the DPDPA Act? A Beginner’s Guide for Businesses

What Is the DPDP Act? A Beginner's Guide for Businesses

Learn how the Digital Personal Data Protection (DPDP) Act helps businesses collect, process, store, and protect personal data responsibly while ensuring compliance with India's evolving privacy regulations..

What Is the DPDPA Act? A Beginner’s Guide for Businesses

DPDP Compliance

Data is one of the most valuable assets a business owns today. From personal data of customers and employees to payment information and data related to user activity, businesses process huge volumes of personal data every single day. Given the rising concerns regarding personal privacy, organizations must start managing personal data with great care and responsibility.

Here come the provisions of the DPDP Act. Digital Personal Data Protection Act is a unique Indian privacy law that addresses how organizations process, collect, store and secure personal data. For any SaaS startup or business growing rapidly, learning about the DPDP Act and its provisions becomes absolutely necessary.

This guide will help you to understand what the DPDP Act is, why you should know it, and how to proceed further.

What Is the DPDP Act?

“DPDP Act” is an abbreviation for “Digital Personal Data Protection Act, 2023.” This act represents the full name for the legislation that deals with data protection in India in relation to the processing of digital personal data.

This act contains all necessary provisions concerning the collection, use, storage, and transmission of personal data.

The primary goal of the DPDP Act is to create a balance between:

  • Protecting individual privacy rights
  • Supporting innovation and digital growth
  • Encouraging responsible data processing
  • Promoting trust in digital services

Quick Definition

Digital Personal Data Protection Act can be defined as legislation that lays down rules for businesses about how personal data should be dealt with in order to ensure transparency, accountability, and privacy. 

Why is the DPDP Act important?

With businesses moving into the digital space, the amount of personal data being collected is increasing day by day.

The different kinds of information include: 

  • Personal Information
  • Customer information
  • Contact Details
  • Payment information
  • Employee information
  • Usage information
  • Marketing preferences

Without appropriate protection measures, there could be risks of exposure and misuse of the personal information gathered from customers.

Understanding what is the DPDP Act and why it is important gives an organization a clear idea of how to use the personal information of customers.

Who Needs to Comply with the DPDP Act?

The Data Privacy and Data Protection Bill affects entities who process digital personal data in India.

These include:

  • SaaS firms
  • Startups
  • E-commerce companies
  • Tech firms
  • Firms in finance
  • Healthcare companies
  • Digital platforms and applications

Whether you are a startup catering to hundreds of users or a developing company processing thousands of records, there may be a need to comply with the DPDP law.

Basic Principles of the DPDP Act

The Act relies on some basic principles that provide guidelines for responsible data processing.

Data Processing Based on Consent

It requires obtaining proper consent from individuals before processing their personal data.

They should know:

  • What data will be collected from them
  • Why the organization collects such data
  • How the collected data will be used
  • For how long will the collected data be stored

Purpose Limitation

Firms must have a specific purpose when processing personal data.

If the firm uses personal data for any other activity than initially planned, it requires consent from the individual.

Data Accuracy

Businesses must keep personal data updated at all times when it is necessary.

Data Protection

Businesses should use appropriate security measures to prevent unauthorized access to personal data.

Accountability

They must always make sure that the processing of personal data is done legally.

Introduction to Data Privacy Compliance

Data Privacy Compliance involves the measures put in place by organizations to comply with laws and regulations regarding personal data protection.

For businesses, compliance goes beyond just avoiding punishment and allows for the following:

  • Establishing customer trust
  • Enhancing data governance
  • Improving cybersecurity
  • Facilitating growth
  • Boosting brand reputation

Businesses that ensure personal privacy gain an edge in today’s digitally competitive market.

Personal Data Protection: An Important Element

Personal Data Protection is fast becoming an important business issue.

In today’s world, customers require that companies show how they protect their information. Personal data protection enables businesses to:

  • Minimize security threats
  • Avoid data breaches
  • Enhance customer trust
  • Comply with regulations
  • Enable sustainable growth

For software as a service (SaaS) startups, securing personal data could be the main consideration when attracting enterprise clients.

Achieving DPDP Act Compliance for Businesses

It is common for businesses to wonder about ways to meet DPDP Act compliance requirements without making their operations difficult.

The best part is that one can approach the issue in a stepwise manner.

Common Compliance Challenges Faced by Businesses

Startups may face difficulties regarding data privacy due to:

  • Rapid growth
  • Lack of compliance capacity
  • Complicated IT infrastructure
  • Integration of third-party solutions
  • Inadequate processes

Nonetheless, proper compliance ensures future success.

Practical Example: Why the DPDP Act Matters

Imagine a SaaS company collecting customer information through its platform.

Without proper privacy controls:

  • Consent records may be missing
  • Customer requests may go unanswered
  • Data retention practices may be unclear
  • Security risks may increase

With proper DPDP compliance:

  • Data processing becomes transparent
  • Customer trust improves
  • Security controls strengthen
  • Regulatory readiness increases

The result is a more resilient and trustworthy business.

Case Study: Significance of DPDP Act Compliance

Take an example of a SaaS firm gathering data from customers via its portal.

In case of inadequate privacy policies:

  • Lack of consent logs could exist
  • Requests by the customers may not be fulfilled
  • Data retention policies may be unclear
  • Risk exposure will increase

With adequate DPDP compliance:

  • Data processing activities become visible
  • Trust of the customers enhances
  • Security policies become robust
  • Regulation compliance level rises
How to Comply with the DPDP Act

Companies seeking guidance for complying with the DPDP Act can concentrate on developing a privacy-focused mindset.

  • The following steps are essential:
  • Mapping personal data flows
  • Getting consent
  • Writing down privacy policies
  • Securing data
  • Educating staff
  • Monitoring compliance processes on a consistent basis

Instead of seeing compliance as a one-off process, companies must approach compliance as a continuous effort.

How SOCLY.io Assists Organizations in Ensuring Easy DPDP Compliance

Compliance with privacy policies can be difficult, particularly for startups that are expanding and have fewer resources to comply with the policies. The SOCLY.io platform assists organizations to comply easily using automation.

Through SOCLY.io, organizations will be able to:

  • Consolidate all policies relating to privacy
  • Manage consent management tasks
  • Ensure continuous monitoring of compliance policies
  • Detect any risks and loopholes associated with privacy
  • Simplify preparation for audits and reporting of findings
  • Achieve continuous compliance through automation

With SOCLY.io, organizations will be able to achieve continuous compliance in a more efficient manner.

Future of Data Privacy in India

Privacy is becoming one of the key priorities for every organization irrespective of their industry sector.

Consumers, regulatory authorities, and business partners have started expecting the companies to manage personal data in a responsible manner.

Organizations that take privacy seriously today would benefit from:

  • Building customer trust
  • Improving security
  • Compliance preparedness
  • Business expansion
  • Regulatory risk management

The DPDP Act is indeed a great initiative towards building a secure and privacy-friendly digital environment in India.

Frequently Asked Questions

What is the DPDP Act and why is it important?

The DPDP Act is India’s data privacy law that regulates how organizations collect, process, and protect personal data. It helps safeguard privacy rights while promoting responsible data handling.

Who does the DPDP Act target?

The act targets organizations involved in processing digital personal data and includes startups, SaaS companies, technology organizations, and other firms present in India. 

What is personal data under the DPDP Act?

Personal data refers to any information that can identify an individual, either directly or indirectly.

What is data privacy compliance?

Data privacy compliance involves implementing policies, processes, and controls that ensure personal data is handled according to applicable privacy laws and regulations.

How can businesses comply with the DPDP Act?

Businesses can comply by identifying personal data, obtaining consent, implementing security controls, maintaining privacy policies, and establishing procedures for managing data requests.

Why is personal data protection important for startups?

Personal data protection helps startups build trust, improve security, meet compliance obligations, and strengthen relationships with customers and investors.

Conclusion

In light of the ever-growing dependency of organizations on data, privacy must no longer take a backseat. With the passing of the DPDP Act, organizations now have a legal and ethical framework under which they can process personal data while fostering trust with their consumers.

By adopting the provisions of the DPDP Act, adhering to strong Data Privacy Compliance measures, and prioritizing Personal Data Protection, startups and organizations can gain a competitive edge over other companies within the same industry.

Are you ready to take your privacy program and DPDP compliance to the next level?

Please do not hesitate to Contact Us,  visit our website, or Get Started Now to see how your organization can leverage its personal data.

Let's Talk

Tell us about your compliance needs and we’ll get back to you within 24 hours.

By submitting, you agree to our Privacy Policy and Terms of Service