Categories
SOC 2

DPDP Act Compliance Checklist: Everything You Need to Meet the Digital Personal Data Protection Act
DPDP Act Compliance Checklist: Everything You Need to Meet the Digital Personal Data Protection Act

DPDP Act Compliance Checklist: Everything You Need to Meet the Digital Personal Data Protection Act

DPDP Act Compliance Checklist: Everything You Need to Meet the Digital Personal Data Protection Act

>DPDP Act Compliance Checklist: Everything You Need to Meet the Digital Personal Data Protection Act

DPDP Act Compliance Checklist: Everything You Need to Meet the Digital Personal Data Protection Act

Learn how to achieve DPDP Act compliance with a practical checklist covering data protection obligations, consent management, security safeguards, and key steps to protect personal data and reduce compliance risks.

DPDP Act Compliance Checklist: Everything You Need to Meet the Digital Personal Data Protection Act

DPDP Act Compliance Checklist
Why DPDP Compliance Matters

India’s Digital Personal Data Protection Act (DPDPA) is no longer a distant concept. For every company that collects, stores, or uses personal data in India, DPDP compliance is now a core business requirement. And with the Data Protection Board of India now operational, DPDPA compliance is moving from “eventually” to “this year.”

  • Builds customer trust
  • Fends off large monetary fines
  • Keeps board members and investors happy
  • Simplifies cross-border operations

If your business also builds or deploys AI systems, it’s worth reading this alongside our ISO 42001 certification guide — the data governance requirements under DPDP compliance in India overlap significantly with AI governance obligations.

Digital Personal Data Protection Act 2023 in a Nutshell
The Act, passed in August 2023, sets rules for the entire life cycle of digital personal data. Below is a quick snapshot:
Area What the DPDP Act Says
Scope Applies to personal data collected online or digitised later, if the processing is in India or relates to Indian residents.
Principles Lawful purpose, consent or legitimate use, data minimisation, accuracy, storage limits, security, accountability.
Roles Data Fiduciary (controller) and Data Processor.
Regulator Data Protection Board of India.
Who Must Comply With the DPDP Act?
  1. Indian companies of all sizes
  2. Foreign firms that target Indian users
  3. Start-ups, MSMEs, large conglomerates
  4. NGOs and government bodies that process personal data

There is no turnover threshold. If you handle personal data digitally, DPDP Act compliance is a must.

Key DPDP Act Requirements

Below are the practical requirements businesses must meet

 1. Lawful processing

  • Identify a clear purpose.
  • Avoid incompatible secondary uses.

2. Valid consent management

  • Obtain consent that is free, specific, informed, unconditional, and unambiguous.
  • Make withdrawing consent just as easy as giving it.

3.Transparent privacy notice

  • Draft notices in plain language, available in English and local languages.
  • Include purpose, categories of data, retention period, grievance contact.

4. Honour Data Principal rights

  • Right to information, correction, erasure, revoke consent, and grievance redressal.
  • Set up a simple portal or email channel for requests.

5. Security safeguards

  • Risk-based technical and organisational measures.
  • Encryption at rest & transit, regular audits, role-based access.

6. Breach notification

  • Report personal data breaches to the Data Protection Board and affected users without delay, with a more detailed report typically expected within 72 hours.
  • Maintain an incident response plan.

7.Cross-border transfers

  • Allowed by default, except to countries the Government may restrict in the future.
  • No countries have been restricted as of this writing, but the mechanism exists, so monitor for updates.

Tip: Align the above with ISO/IEC 27001 controls for faster DPDP Act compliance. If you’re building out security safeguards from scratch, our ISO 27001 certification guide covers the same underlying controls in more depth.

DPDP Compliance Checklist for Businesses

Use the quick list below to track progress:

S.NoAction Item
1Map personal data flows
2Classify data & identify high-risk processing
3Draft/update privacy policy & consent forms
4Appoint a Grievance Officer (and DPO if Significant Data Fiduciary)
5Deploy a consent-management platform
6Update contracts with Data Processors
7Conduct Data Protection Impact Assessment (DPIA)
8Run security gap assessment
9Set up breach response playbook
10Launch employee awareness programme

In practice, task number 1 – mapping personal data flows  – is the one that tends to be underestimated the most by any team. It may seem formal, but in practice, it turns out to be the one that brings up the most unexpected issues: some marketing tool storing email addresses of its customers secretly, or a support system sending out its data to a shared spreadsheet.

DPDP Act 2023 Compliance Checklist (Downloadable)

Need a printable copy?

DPDP Act Penalties at a Glance

The Act introduces a tiered penalty system under Schedule I, with maximum penalties assessed per instance of violation:

ViolationMaximum Penalty
Failure to take reasonable security safeguards (leading to a data breach)Up to ₹250 crore
Failure to notify the Board / affected individuals of a breachUp to ₹200 crore
Non-fulfilment of additional obligations towards children’s dataUp to ₹200 crore
Significant Data Fiduciary failing its additional obligations (DPO, DPIA, audits)Up to ₹150 crore
General/residual non-compliance — any other breach of the Act or Rules not listed aboveUp to ₹50 crore


A few things worth understanding about how this actually works in practice:

  • These are maximums, not fixed fines. The Data Protection Board considers the nature, gravity, duration, and repetition of the violation, along with mitigation efforts, before setting the actual amount.
  • Penalties stack. A single incident can trigger multiple violations at once for example, a breach caused by weak safeguards (up to ₹250 crore) combined with a late notification (up to ₹200 crore) so real exposure can be higher than any single row in this table suggests.
  • There’s no size exemption on paper. The statutory maximums apply regardless of company size, though the Board’s actual enforcement approach is expected to weigh an organization’s scale, intent, and remediation efforts.

Penalties can quickly exceed annual profits for a growing business. Staying DPDP compliant in India is a fraction of the cost of paying even one of these fines.

We found out that the founders are more concerned about the big figure of ₹250 crores and think it is only for the large businesses. The truth of the matter is that the ₹50 crores figure is the residual which tends to affect small firms since it covers almost anything not specifically listed above, including things as ordinary as an outdated privacy notice. 

Source: Schedule I, Digital Personal Data Protection Act, 2023 (full text, MeitY)  

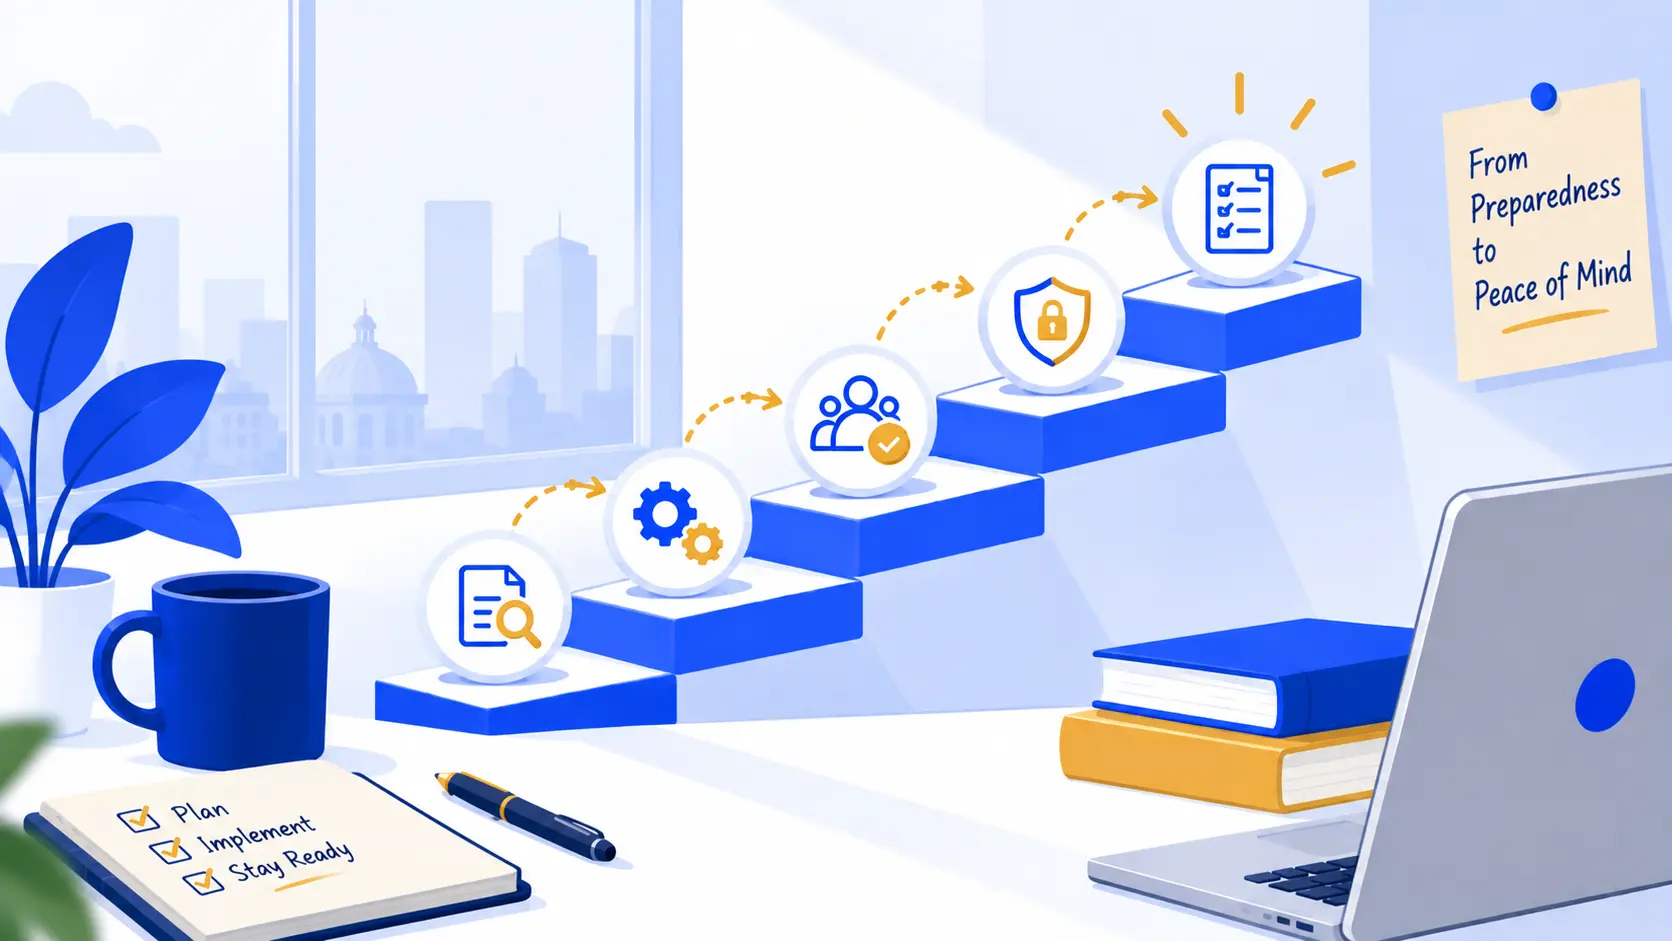
How to Comply With DPDP Act: Step-by-Step Roadmap

Follow the roadmap below, especially if you’re starting late.

A quick, honest note before you dive in: most companies underestimate Step 1. It looks like the “easy” part, but it’s usually where the real timeline gets set. You can’t fix what you haven’t found yet.

Step 1  Assessment (Week 1–4)

  • Inventory data systems.
  • Interview process owners.
  • Identify overseas transfers.

Step 2  Gap analysis (Week 5–6)

  • Compare current practice with DPDP compliance requirements for businesses.
  • Prioritise high-risk gaps (e.g., children’s data).

Step 3  Remediation (Week 7–16)

  • Update notices and contracts.
  • Configure technical controls (MFA, encryption).
  • Launch consent collection flows.

Step 4  Audit & certification (Week 17–20)

  • Conduct internal audit or hire external assessor.
  • Keep audit reports for regulators.

Step 5  Ongoing monitoring (Monthly/Quarterly)

  • Periodic risk assessments.
  • Refresh training.
  • Test breach drills.

Not sure where to start? Get a free DPDP Act gap assessment and get a clear, prioritized starting point instead of guessing.

DPDP Compliance Automation Tools

Manual spreadsheets break down fast, data flows change, consent records go stale, and by the time an audit or a Board inquiry comes around, nobody’s confident the paperwork actually matches reality.

Rather than stitching together separate tools for each function, platforms like SOCLY.io are built to cover multiple pieces of DPDP compliance from one place:

  • Data mapping – automatically inventory where personal data lives and flows
  • Consent record management – centralized, audit-ready consent trails instead of scattered logs
  • Rights request handling – a structured way to log and resolve Data Principal requests
  • Breach readiness – real-time monitoring so you’re prepared before an incident, not scrambling after one
  • Reporting dashboards – one view of your compliance status instead of exporting from five different tools

Benefits of automation, generally:

  • Saves time on repetitive tasks
  • Creates audit-ready evidence trails
  • Reduces human error

If you’re currently piecing together point solutions for data mapping, consent, and reporting separately, it’s worth asking whether a single platform could replace that stack — see how SOCLY.io automates DPDP compliance →

Sector-Specific Considerations
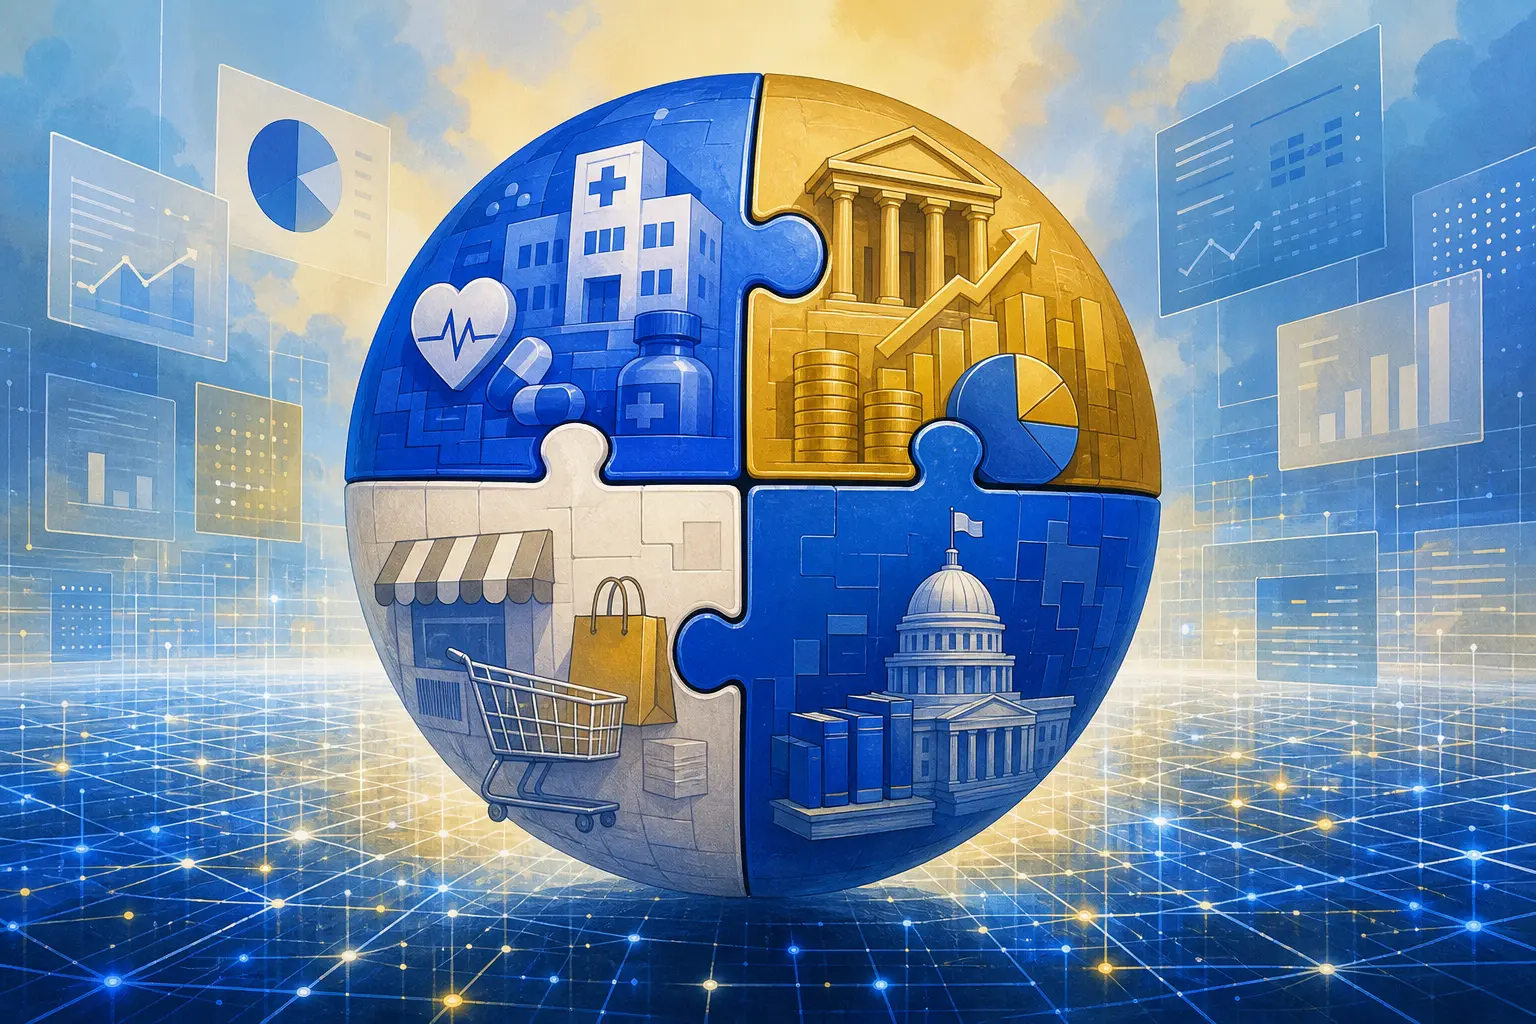
  1. FinTech – Align DPDPA with the RBI Cyber Security Framework.
  2. Health-tech – Map with the upcoming Digital Information Security in Healthcare Act (DISHA).
  3. E-commerce – Combine DPDPA consent requirements with Consumer Protection (E-commerce) Rules.
  4. Ed-tech – Extra care for children’s data & parental consent.
DPDP Compliance Date & Timelines

Unlike when this guide was first drafted, the DPDP Rules are no longer pending — they were formally notified, and the compliance runway is now clearly defined in phases:

MilestoneDate
DPDP Act passedAugust 2023
DPDP Rules, 2025 notified; Data Protection Board establishedNovember 13, 2025
Consent Manager registration opens; mandatory DPO for Significant Data FiduciariesBy November 13, 2026
Full substantive compliance enforceable (consent, notices, safeguards, breach protocols)May 13, 2027


What this means practically: 2026 is the working year. The gap between “the law exists” and “the law is actively enforced” is closing, and the businesses that wait until early 2027 to start will be doing in weeks what should have taken months. Keep an eye on MeitY updates for any further procedural notifications as the Consent Manager framework rolls out.

Source: DPDP Rules, 2025 and enforcement notifications, Gazette of India, November 13, 2025 (PIB press release) 

Frequently Asked Questions (FAQ)

1. Is DPDP compliance mandatory for small start-ups?

Yes, there are no exceptions with regards to size of companies. However, micro-companies are expected to have slightly less complicated requirements under the Rules in some respects.

2. Do we need a Data Protection Officer?

Only those data fiduciaries who are identified as Significant Data Fiduciaries by the government are mandatorily required to have a DPO. However, most companies choose to do so voluntarily in order to be well-organized.

3. How long can we keep user data?

As long as it is necessary for achieving the initial purpose or until required by law, whichever is shorter.

4.What happens if users withdraw consent?

You will have to cease the processing of their data unless there is any other legal basis, and notify the recipients of such withdrawal.

5. Is anonymised data outside the Act?

Anonymized and irreversibly changed data does not come under the scope of this Act, while pseudonymized data is personal data.

6. What’s the difference between DPDP compliance and DPDPA compliance?

Nothing “DPDP compliance” and “DPDPA compliance” refer to the same thing. Both are shorthand for compliance with the Digital Personal Data Protection Act, 2023.

Final Thoughts & Next Steps

DPDP compliance is not a one-time project; it’s an ongoing commitment to transparency and accountability. Map your data, close the gaps early, and keep records ready for the Board.

Get your free DPDP Act gap assessment and see exactly where your business stands. Or, if you’re also working on ISO 42001, SOC 2, or ISO 27001, check out our other compliance guides to see how these frameworks overlap.

Stay informed, stay secure, and make DPDP Act compliance your competitive edge in 2026 with SOCLY.io.

Ready to Simplify Your Compliance Journey?
Categories
HIPAA

HIPAA Risk Assessment: A Step-by-Step Guide

HIPAA Risk Assessment: A Step-by-Step Guide

HIPAA Risk Assessment: A Step-by-Step Guide

HIPAA Risk Assessment: A Step-by-Step Guide

>HIPAA Risk Assessment: A Step-by-Step Guide

HIPAA Risk Assessment: A Step-by-Step Guide

Learn how to conduct a HIPAA risk assessment, identify potential threats to electronic protected health information (ePHI), evaluate security vulnerabilities, and strengthen your organization's healthcare data protection practices.

HIPAA Risk Assessment: A Step-by-Step Guide

HIPAA Risk Assessment

A security incident can compromise electronic protected health information (ePHI), disrupt operations, affect patient care, and create compliance risks. A thorough HIPAA risk assessment helps healthcare organizations identify and evaluate risks to their ePHI.

The HIPAA Security Rule requires regulated entities to conduct an accurate and thorough assessment of potential risks and vulnerabilities to the confidentiality, integrity, and availability of the ePHI they create, receive, maintain, or transmit. HHS identifies risk analysis as a foundational part of the Security Rule’s security management process.

A risk assessment for organizations managing ePHI does not only mean filling up a list of questions. There is an in-depth analysis of the organizational environment that encompasses potential risks and weaknesses in addition to their effects on the organization.

What Is a HIPAA Risk Assessment?

A HIPAA risk assessment refers to the process of analyzing all the possible threats and weaknesses concerning confidentiality, integrity, and availability of the ePHI.

This should be done based on ePHI created, received, maintained, or transmitted by the covered entity. This involves ePHI that is stored or maintained on systems, applications, devices, networks, and electronic media.

One helpful method for conducting a risk analysis involves:

What do you have? → What could possibly go wrong? → What are the risks involved? → What has to change? → Record and review it.

The HIPAA Security Rule has no set methodology prescribed for doing the risk analysis. However, the chosen method must meet the Rule’s requirements and account for the organization’s size, complexity, capabilities, and environment.

Why Is a HIPAA Risk Assessment Important?

Risk assessment provides an organization with a real image of its surrounding environment in terms of security.

It can help identify issues such as:

Moreover, it will aid in providing information for the organization’s risk management efforts. HHS makes the distinction between the two clear: risk analysis assesses risks, while risk management entails taking the necessary security measures to mitigate such risks to an acceptable level.

HIPAA Risk Assessment Requirements

Knowing about HIPAA Risk Assessment Requirements is essential prior to conducting the assessment.

An adequate strategy for the assessment would be the one that evaluates the threats and vulnerabilities to the security of the ePHI.

Some important elements to consider according to HHS include:

  1. Defining the scope of the analysis
  2. Identifying where ePHI exists
  3. Identifying and documenting threats and vulnerabilities
  4. Assessing existing security measures
  5. Determining the likelihood of threats occurring
  6. Determining potential impact
  7. Determining the level of risk
  8. Documenting the analysis
  9. Reviewing and updating the assessment as necessary

HIPAA does not prescribe a single template or scoring method. The assessment must reflect the organization’s environment and address the required elements of a thorough risk analysis.

HIPAA Risk Assessment Step by Step

Step 1: Define the Scope

Start by establishing what the assessment covers.

Determine what systems, applications, devices, locations, individuals, and processes create, receive, store, or transmit ePHI.

For example, a healthcare SaaS provider may need to consider:

  • Production applications
  • Cloud infrastructure
  • Databases
  • Employee devices
  • Backup systems
  • APIs
  • Email systems
  • Third-party platforms
  • Remote access systems

This helps ensure that the assessment covers all relevant ePHI. According to HHS, the analysis must account for ePHI regardless of where or how it is created, received, maintained, or transmitted.

Step 2: Identify and Map ePHI

Next, determine what ePHI your organization handles and where it goes.

Document:

  • What ePHI is collected
  • Where it is stored
  • How it is processed
  • Who can access it
  • Where it is transmitted
  • Which vendors handle it
  • How it is backed up
  • When it is deleted

Use of data flow diagrams will also assist in such cases since these will help in depicting the flow of information in applications and personnel and contractor areas.

Step 3: Identify Threats and Vulnerabilities

Now ask two related questions:

What could cause harm?

That is the threat.

What weakness could allow that threat to cause harm?

That is the vulnerability.

These can include anything from unauthorized access, to viruses and phishing, accidental loss of data, system failure, natural disasters and other forms of dangers. As stated by HHS, the sources of threats are human, natural or environmental.

The vulnerabilities are technical or non-technical and include software that is outdated, improper configuration or absence of security policies.

Step 4: Review Existing Security Measures

Just because you have found a vulnerability does not mean that there are no controls to protect from the vulnerability. Look at the current controls being implemented.

For instance:

Risk: Unauthorized access to the patient database.

Current controls: Authentication, access controls, logging, and monitoring.

Then determine if the above security controls are properly implemented to handle the risk. The HHS has recommended doing the above evaluation of existing security controls.

Step 5: Evaluate Likelihood

Determine how likely each identified threat is to occur or exploit a vulnerability.

Your organization might use categories such as:

  • Low
  • Medium
  • High

Or it may use a numerical scoring model.

The methodology itself may differ depending on the particular organization. The crucial point is to use the chosen methodology and record why a certain methodology is used for this assessment. HHS states that there is no particular methodology which Security Rule prescribes to conduct risk analysis.

Step 6: Evaluate Potential Impact

Next, determine what could happen if the risk occurs.

Consider potential effects on:

  • Confidentiality of ePHI
  • Integrity of ePHI
  • Availability of ePHI
  • Patient care
  • Business operations
  • Systems and services
  • Regulatory obligations

For example, a short outage affecting a non-critical internal application may have a different impact from an outage affecting a system required for patient care.

HHS guidance calls for consideration of the potential impact, or criticality, associated with threats affecting ePHI.

Step 7: Determine the Risk Level

Combine your likelihood and impact assessments to determine the overall level of risk.

A simple model might look like:

Risk Level = Likelihood × Impact

For example:

Risk

Likelihood

Impact

Overall Risk

Phishing leading to account compromise

High

High

High

Loss of an encrypted backup device

Low

Medium

Medium

Temporary outage of a non-critical system

Medium

Low

Low

This was only a simple illustration. Use methodology appropriate to your situation.

HHS recommends that a risk level be defined for every possible combination of threats and vulnerabilities.

Step 8: Create a Risk Management Plan

A risk assessment identifies problems. The next step is deciding how to address them.

For each significant risk, document:

  • Risk description
  • Risk rating
  • Existing controls
  • Recommended action
  • Responsible owner
  • Target completion date
  • Status
  • Residual risk

For example:

Risk: Unauthorized access to ePHI
Rating: High
Action: Strengthen privileged access controls and MFA
Owner: IT Security Manager
Target: 60 days
Status: In progress

This turns your HIPAA security risk assessment into an actionable security program.

Step 9: Document Everything

Documentation is an important part of the process.

HHS states that the Security Rule requires the risk analysis to be documented but does not require a particular format.

Your documentation should make it possible to understand:

  • What was assessed
  • What systems were included
  • Which risks were identified
  • How risks were evaluated
  • What controls already existed
  • What actions were planned
  • Who was responsible
  • When the assessment was performed

Step 10: Review and Update the Assessment

A risk assessment for HIPAA compliance should not be done only once.

The organization must conduct updates on the analysis based on any changes in its environment and operations. According to HHS, there might be situations like use of new technology, security incidents, change in business operations, among others, which will make it necessary to redo the risk analysis and security procedures.

For example, reassess risks when you:

  • Launch a new application
  • Move systems to a new cloud provider
  • Introduce new medical technology
  • Add a significant vendor
  • Experience a security incident
  • Change how ePHI is processed
  • Make major infrastructure changes
Common HIPAA Risk Assessment Mistakes
HIPAA Risk Assessment
 HIPAA Risk Assessment Checklist

Before completing your assessment, confirm that you have:

  • Defined the assessment scope
  • Identified all relevant ePHI
  • Mapped systems and data flows
  • Identified threats and vulnerabilities
  • Reviewed existing safeguards
  • Assessed likelihood
  • Assessed potential impact
  • Assigned risk levels
  • Documented risks and findings
  • Assigned remediation owners
  • Tracked corrective actions
  • Established a review and update process
 Frequently Asked Questions 

What is a HIPAA Risk Assessment?

A HIPAA risk assessment evaluates potential risks and vulnerabilities affecting the confidentiality, integrity, and availability of ePHI that a regulated entity creates, receives, maintains, or transmits.

How to conduct a HIPAA risk assessment?

To conduct a HIPAA risk assessment, define the scope, identify ePHI and map its flows, identify threats and vulnerabilities, evaluate existing safeguards, assess likelihood and potential impact, determine risk levels, document findings, and address identified risks through risk management.

How often should a HIPAA risk assessment be performed?

The HIPAA Security Rule does not prescribe one fixed schedule for all organizations. Risk analysis should be ongoing, with reviews and updates as needed based on changes in the organization’s environment, operations, technology, and security risks.

Is a HIPAA risk assessment required?

Yes. Under the Security Rule of HIPAA, a comprehensive risk assessment of threats and vulnerabilities to electronic protected health information must be carried out.

What is the difference between HIPAA risk analysis and risk management?

Risk analysis is concerned with identifying and analyzing risks and vulnerabilities. On the other hand, risk management entails putting in place various security controls to bring down the risks to an acceptable level.

Can a HIPAA risk assessment be automated?

Technology is useful in helping organizations identify their assets, risks, assign corrective actions, gather evidence, and monitor changes. However, technology does not mean that humans are exempt from making decisions.

Conclusion

HIPAA Risk Assessment is a systematic approach for an organization to assess the risks associated with the ePHI environment. It begins with defining the environment and identifying the ePHI, followed by threat identification, vulnerability assessment, likelihood and impact assessment, risk prioritization, documentation, and risk management.

The main thing to remember here is that risk assessment must be done according to your environment and not simply based on a checklist. Your risk assessment must keep up with changes in your systems, vendors, technology, and operations.

If you need a more structured approach for HIPAA Security and Compliance Program Management, Contact Us to learn about your needs and Get Started Today.

Ready to Simplify Your Compliance Journey?
Categories
GDPR

How Compliance Automation Simplifies GDPR Documentation

How Compliance Automation Simplifies GDPR Documentation

How Compliance Automation Simplifies GDPR Documentation

How Compliance Automation Simplifies GDPR Documentation

>How Compliance Automation Simplifies GDPR Documentation

How Compliance Automation Simplifies GDPR Documentation

Learn how GDPR compliance automation helps businesses organize privacy documentation, streamline compliance workflows, maintain accurate records, and improve visibility across data protection activities.

How Compliance Automation Simplifies GDPR Documentation

Compliance Automation Simplifies GDPR Documentation

Management of GDPR documentation may quickly become challenging if privacy files are scattered between spreadsheets, email messages, cloud drive files, etc. GDPR Compliance Automation integrates the above activities into an organized workflow process, assisting organizations in managing their privacy documentation.

The reason why this is crucial for businesses is that GDPR compliance is not a simple task of documentation. Businesses have to know what information they are processing, for what purpose, who can access it, where it goes, and how it is secured. And they also have to ensure that their records stay up-to-date.

Automation will be able to eliminate some of the repetitive tasks and make management of this information easier. The idea is not to automate responsibilities away, but rather to provide greater visibility and consistency for the privacy and compliance teams.

 What Is GDPR Compliance Automation?

GDPR Compliance Automation makes use of software and automated workflows to assist in managing the repetitive privacy and compliance tasks.

These include, among others:

The capabilities differ from one platform to another. Automation has to be such that it helps to support the organization’s privacy program and the right people have to make decisions.

Why Is GDPR Documentation Difficult to Manage Manually?

Documentation under GDPR is not limited to just a privacy policy.

There is information relating to processing operations, categories of data, purposes, recipients, retention periods, and many other aspects of the privacy program.

The challenge becomes greater as a business grows.

For instance, a SaaS business could implement a new customer support portal. This could lead to the addition of a new data processor along with issues concerning the type of data that is shared, reasons for processing such data, and retention period.

Where documentation is done manually, it becomes difficult for employees to deal with:

Outdated records
Duplicate information
Missing documentation
Unclear ownership
Manual follow-ups
Inconsistent review schedules
Difficult evidence collection
Limited visibility into compliance status

This is where automation can make a practical difference.

How Compliance Automation Simplifies GDPR Documentation

1. Centralizes GDPR Documentation

The main benefits of automation are having privacy information in one system.

Without having to search across several spreadsheets and folders, all the necessary compliance information can be managed in one place.

A GDPR compliance software solution may offer such sections for processing activities, vendors, assessments, policies, tasks, and evidence.

This way, there will be a more structured source of information for privacy and compliance teams.

2. Automates Repetitive Compliance Tasks

Many documentation activities are repetitive.

For example, a privacy manager may need to:

  1. Assign a documentation task.
  2. Notify the responsible employee.
  3. Follow up before the deadline.
  4. Review the completed information.
  5. Record approval.
  6. Schedule a future review.

Most of the processes can be automated.

Instead of manually reminding and tracking tasks, it can automate all these processes using workflows that have been defined beforehand.

This way, compliance officers will have more time for analyzing privacy risks and will spend less time on administrative processes.

3. Makes Records of Processing Easier to Maintain

A Record of Processing Activities, commonly called a ROPA, is an important part of GDPR compliance documentation for organizations where the relevant Article 30 requirements apply.

Article 30 of the GDPR sets out the requirements for records of processing activities, including the information these records must contain and the circumstances in which they must be maintained.

A ROPA can contain information such as:

  • Processing purposes
  • Categories of personal data
  • Categories of data subjects
  • Recipients
  • International transfers
  • Retention information
  • Security measures

Accuracy of the record keeping may be difficult when the process is constantly changing.

Automation will enable a systematic workflow for creating, reviewing, assigning ownership, and updating the records of the process.

The organization will have to make sure that the information is accurate. This is not what automation does.

4. Improves Vendor and Processor Tracking

Personal data is usually not processed solely by the company itself.

Cloud service providers, analytics platforms, payment processors, customer relationship management software, email providers, and many other vendors may be processing personal data on behalf of an organization.

A compliance automation platform can assist in maintaining an up-to-date vendor inventory and linking vendors to processing activities.

It becomes much easier to answer questions like:

  • Which vendors process personal data?
  • What information do they process?
  • What is their role?
  • Where is the data transferred?
  • When is it time to review the vendor relationship?

Even a workflow will help in tracking the privacy reviews and documentation of third party processors.

How to Automate GDPR Documentation Step by Step

If you are wondering how to automate GDPR compliance documentation, avoid trying to automate everything at once.

Step 1: Identify Your Documentation

Start by listing the privacy records your organization maintains.

These may include:

  • Records of processing activities
  • Privacy policies
  • Data protection assessments
  • Vendor records
  • Data retention information
  • Data subject request records
  • Consent records where applicable
  • International transfer documentation
  • Security and privacy procedures

Step 2: Identify Ownership

All important records must have an accountable owner.

For instance, a processing activity may have a department manager as its owner and the privacy and legal teams can be tasked to review privacy policies.

The best way for automation is where there are well-defined responsibilities before creation of workflows.

Step 3: Map Recurring Activities

Identify tasks that happen repeatedly.

Examples include:

  • Quarterly vendor reviews
  • Annual policy reviews
  • New processing assessments
  • Employee privacy training
  • Periodic documentation reviews

These activities are strong candidates for automated reminders and workflows.

Step 4: Establish Review Triggers

Not every update should depend on a calendar reminder.

Some changes should trigger a documentation review.

For example:

New Software → New Vendor → Personal Data Processed → Privacy Assessment → Update Documentation

Establishing these connections may enable organizations to react more uniformly to changes in their processing environment.

Step 5: Monitor and Improve

Automation should not be considered a “set it and forget it” process.

Look at whether workflows are functioning, whether the records are current, and whether tasks have been accomplished by employees.

Identify any overdue processes using compliance dashboards and reports.

GDPR Compliance Automation for Businesses: A Practical Example

Imagine a scaling SaaS business that has more than 50 third-party applications. 

The business uses spreadsheets to record all vendor information, and the process activities are recorded in a separate document. Every time a new service comes into play, somebody needs to find out if it processes any personal data and update the documents accordingly.

Using GDPR compliance automation for businesses, the company will be able to develop an organized workflow.

When a new vendor appears:

Vendor added → Privacy review assigned → Data processing assessed → Relevant records updated → Owner notified → Review scheduled

The workflow doesn’t determine whether the process is legal or not. Instead, it ensures that the correct information is communicated to the correct person at the right time.

That distinction is important.

Benefits of GDPR Compliance Automation

When implemented properly, automation can help organizations achieve several practical benefits.

Benefits of GDPR Compliance Automation
What GDPR Compliance Automation Cannot Do

Automatization is great, but it doesn’t take the place of privacy knowledge or organizational responsibility.

No matter what software solution you employ, you can’t always know the legal requirements.

Organizations still need people to:

  • Make privacy decisions
  • Evaluate risks
  • Review processing activities
  • Approve policies
  • Assess contractual requirements
  • Determine appropriate safeguards
  • Respond to unusual or complex situations

So, automation should be complemented by governance and people’s assessment.

GDPR Documentation Checklist

Before implementing an automation solution, check whether your organization has:

  • A clear inventory of personal data processing
  • Documented processing purposes
  • Identified data categories and recipients
  • A current vendor and processor inventory
  • Defined documentation owners
  • Review schedules
  • Data retention information
  • International transfer information where relevant
  • Privacy risk assessment processes
  • Procedures for updating records after business changes

Automation works much better when the information and responsibilities are already well-defined.

 Frequently Asked Questions 

What is GDPR Compliance Automation?

GDPR Compliance Automation is a process of automation of privacy compliance processes and activities via technology.

How does compliance automation simplify GDPR documentation?

It helps to centralize the records, automate the workflows, assign the tasks, send notifications, track the changes, and get the visibility of the documentation status. Thus, teams save time on administrative work.

Can GDPR documentation be fully automated?

No. Many administrative processes can be automated, but there is always the need for humans to provide oversight into matters related to privacy.

What is GDPR compliance software?

GDPR compliance software is a type of software that assists organizations in carrying out various privacy-related activities such as record processing, assessment, vendor management, task management, policies, and compliance documentation.

What GDPR documents can be automated?

Based on the type of software used, an organization can automate its workflow for record processing, privacy assessment, vendor records, policy review, data subject requests, and many more documentation activities.

Is GDPR automation suitable for small businesses?

Yes. Small organizations can use automation to set up structured privacy workflows without necessarily having to depend on spreadsheets and reminders alone.

Conclusion

GDPR documentation will get more complex as the company gains more customers, employees, applications, vendors, and data processing operations. Manual processes may become a hindrance when ensuring accuracy in documentation and timely execution of critical reviews.

GDPR Compliance Automation will offer a more organized process through consolidation of information, process automation, ownership and visibility of privacy operations.

The trick here is to ensure that automation works as part of a privacy program and not as a substitute for judgment and responsibility.

To simplify GDPR documentation and implement more efficient privacy processes, you can Contact us today for more information on how compliance automation will enhance your compliance program.

Ready to Simplify Your Compliance Journey?
Categories
DPDPA

DPDP Rules 2025: Key Requirements and What Businesses Need to Know

DPDP Rules 2025: Key Requirements and What Businesses Need to Know

DPDP Rules 2025: Key Requirements and What Businesses Need to Know

DPDP Rules 2025: Key Requirements and What Businesses Need to Know

>DPDP Rules 2025: Key Requirements and What Businesses Need to Know

DPDP Rules 2025: Key Requirements and What Businesses Need to Know

Learn how the DPDP Rules 2025 translate India's data protection law into practical compliance requirements, helping businesses manage consent, protect personal data, meet retention obligations, and prepare for enforcement.

DPDP Rules 2025: Key Requirements and What Businesses Need to Know

DPDP Compliance

India’s Digital Personal Data Protection Rules 2025 are finally here, and if you run a business that handles personal data of Indian users, this directly affects you.

The DPDP Rules 2025 are meant to bridge any shortcomings in the DPDP Act 2023, translating vague provisions into something actionable. Think of the Act as the “what” and the Rules as the “how.” With the DPDP Rules 2025 now in effect, there is no more excuse for businesses to delay figuring out what compliance entails.

This document will provide compliance professionals, legal advisors, startup founders and business owners with a comprehensive and practical understanding of DPDP Act Rules 2025.

Here’s what you’ll find inside:

  • What the DPDP Rules 2025 actually say – an overview of the main points covered, including the need for consent, data retention policies, and how the Rules are different from the Act
  • Special obligations you may not have heard about – including specific protections for children’s data and persons with disabilities that carry their own compliance requirements
  • What to do right now – the operational steps your business needs to take before enforcement kicks in, plus a look at the penalties if you don’t

Let’s get into it.

Understanding the DPDP Rules 2025

What the DPDP Rules 2025 Are and Why They Were Notified

The DPDP Rules 2025 are the set of operational rules released by the Ministry of Electronics and Information Technology (MeitY) that make the DPDP Act, 2023 functional. Consider them to be the guidelines that convert broad principles from legislation into concrete, actionable procedures of data protection that include data collection, processing, security, retention, and deletion.

This was not an initiative taken in isolation by the Ministry. The MeitY received 6,915 public submissions and organized consultations in Delhi, Mumbai, Guwahati, Kolkata, Hyderabad, Bengaluru, and Chennai before releasing them, which makes it one of the most consultative processes of regulation in India. With DPDP Rules 2025 explained through this level of public engagement, the framework carries significant institutional weight.

Source: Digital Personal Data Protection Rules, 2025 — full text (MeitY)

How the DPDP Rules 2025 Relate to the DPDP Act 2023
DPDP Rules 2025 Relate to the DPDP Act 2023

The Act sets out the principles; the Rules set the mechanics. While the Act defines rights and obligations at a high level, the Rules specify how those obligations must actually be met, a distinction explored in greater depth in the next section.

Why These Rules Matter for Businesses Operating in India

The New DPDP Rules 2025 make compliance non-negotiable. Enforcement is no longer theoretically defined, deadlines now exist. Crucially, these Rules apply equally to Indian and foreign businesses serving Indian users, regardless of where they’re incorporated.

DPDP Act 2023 vs. DPDP Rules 2025: What’s the Difference

A. Key Distinctions Between the Act and the Rules

DPDP Act 2023

DPDP Rules 2025

Passed August 2023; Presidential assent 11 August 2023

Notified 13 November 2025 via G.S.R. 846(E)

Defines rights of Data Principals

Specifies how those rights are operationalised

Establishes penalty structure (up to ₹250 crore)

Defines consent notice formats (Rule 3)

Sets principles: purpose limitation, data minimisation

Details breach notification procedures (Rule 7)

Creates the Data Protection Board

Prescribes data retention periods (Third Schedule)

Think of the DPDP Act 2023 as the “what” — the legal framework, rights, and consequences. The Rules are the “how” — the practical mechanisms your organisation must implement.

Sources: DPDP Act, 2023 — full text (MeitY) · DPDP Rules, 2025 — full text (MeitY)

B. Why You Need Both to Achieve Full Compliance

Reading only the Act tells you that consent is required  but not the exact format, language requirements, or approved verification methods. Reading only the Rules without the Act leaves you without the legal context for penalties and rights.

“DPDP Act Rules 2025” and “DPDP Rules 2025” are different ways to describe the exact same set of rules, and are interchangeable in all official communications.Now that this naming confusion is resolved, understanding both documents together gives your compliance programme its complete legal and operational foundation.

When Were the DPDP Rules 2025 Notified? Full Timeline

Official Notification Date

When were the DPDP Rules 2025 notified? The DPDP Rules 2025 were notified in the Official Gazette on 13 November 2025, via Gazette notification G.S.R. 846(E), with MeitY’s public announcement following the next day, on 14 November 2025. This marks India’s formal entry into a structured, rights-driven data protection era.

Source: DPDP Rules, 2025 official notification (PIB press release)

Phase I – What’s Effective Immediately

The DPDP Rules 2025 effective date begins from the notification date itself. Rules 1, 2, and 17–21 came into force immediately, establishing the Data Protection Board’s purpose, appointment process, and operational functioning. You don’t get a grace period here — these obligations apply from day one.

Phase II – Consent Manager Registration (~12 Months)

Approximately one year from publication (~November 2026), Rule 4 activates. This is your DPDP Rules 2025 implementation date for Consent Manager registration, eligibility criteria, and oversight requirements. If your business involves managing user consent at scale, this deadline directly affects your operating model.

Full Compliance Obligations (~18 Months)

Around 18 months from publication (~May 2027), Rules 3, 5–16, 22, and 23 come into full effect covering the bulk of day-to-day Data Fiduciary obligations. This is the deadline you should anchor your compliance roadmap around.

Phase

Timeline

Key Rules Activated

Phase I

Immediate (13 Nov 2025)

Rules 1, 2, 17–21

Phase II

~12 months (~Nov 2026)

Rule 4

Full Compliance

~18 months (~May 2027)

Rules 3, 5–16, 22, 23

Please note that a proposal to reduce the 18-month period to 12 months has informally been made by MeitY. At the time of writing, there is no formal notification of this through the Gazette. Please take the 18-month timeframe into account, but watch out for any official communication in case it changes.

Key Highlights of the DPDP Rules 2025

A. Who the Rules Apply To

Understanding DPDP Rules 2025 applicability is your first step toward compliance. The Rules apply to:

  • Data Fiduciaries – entities that determine the purpose and means of processing personal data
  • Data Processors – entities processing data on behalf of fiduciaries
  • Significant Data Fiduciaries (SDFs) – those designated by the government, carrying heightened obligations

Critically, there is no turnover or company-size threshold. Whether you are a startup or an enterprise, the Rules apply equally to your organization based on your processing activities.

B. Consent Notice Requirements

Each Data Fiduciary needs to provide a separate and distinct notice of consent, which shall be drafted in language that is clear and simple to understand by the Data Principal. This notice cannot be buried inside your general terms of service or privacy policy. It must itemize the specific purposes for which personal data is being collected and processed.

C. Data Protection Board Structure and Functioning

The Data Protection Board is an office functioning digitally wherein everything from filing of complaints to conducting proceedings would take place online. This streamlined structure makes it accessible and efficient for handling grievances under the DPDP Rules 2025.

D. Appellate Tribunal and Appeal Process

If you disagree with a Board decision, the Rules establish a structured appeal procedure through a designated Appellate Tribunal, a procedural detail most compliance guides overlook but one that significantly affects your risk management strategy.

Core Compliance Requirements Under DPDP Rules 2025

A. Data Fiduciary Obligations and Responsibilities

As a Data Fiduciary, you must collect only the personal data necessary for a clearly defined purpose, nothing beyond that. The DPDP Rules 2025 hold you accountable for ensuring data is used strictly within that stated purpose and deleted once it is no longer needed.

B. Consent Management and Lawful Basis for Processing

Your consent mechanisms must meet a high standard. Consent under DPDP Rules 2025 must be:

  • Free – no coercion or conditional access
  • Specific – tied to a defined purpose
  • Informed – clearly explained before collection
  • Unconditional and unambiguous – no bundled or implied consent
  • Easy to withdraw – as simple as it was to give

C. Data Principal Rights Businesses Must Uphold

You are obligated to honour the following rights for every individual whose data you process:

  • Access – provide data summaries upon request
  • Correction – update inaccurate personal data
  • Erasure – fulfil erasure requests within 90 days (Rule 14), including data held by your Data Processors
  • Grievance Redressal – maintain a functional complaint mechanism

D. Cross-Border Data Transfer Restrictions and Approvals

With this in mind, cross-border transfers are permitted by default under DPDP Rules 2025. No countries are restricted yet, but the Government retains authority to block specific destinations. You should monitor official notifications regularly to stay ahead of any future restrictions.

Special Provisions for Children’s Data and Persons with Disabilities

A. Verifiable Parental Consent Requirements

Before processing personal data of any child under 18  or a person with a disability who has a lawful guardian you must obtain verifiable parental or guardian consent. This is a non-negotiable prerequisite under the DPDP Rules 2025, not a best-practice recommendation. Non-compliance here carries penalties of up to ₹200 crore.

B. DigiLocker-Based Identity Verification

Here’s a detail most compliance guides overlook: Rule 10 of the DPDP Rules 2025 explicitly permits DigiLocker-based verification as a mechanism to confirm a parent’s identity and establish the parent-child relationship. This gives you a practical, government-backed method to meet the verifiability requirement without building complex custom verification infrastructure.

C. Prohibited Practices: Tracking, Profiling, and Targeted Ads

As a Data Fiduciary, you are strictly prohibited from:

  • Tracking children’s online behaviour
  • Profiling children for any purpose
  • Serving targeted advertisements directed at children

In addition to the above constraints on processing, you need to implement technical age-gate measures to ensure that children do not access services inappropriate for their age group. This is not an optional set of controls but one expected by regulators to be backed up with technical solutions.

Data Retention Requirements Under the Third Schedule

Sector-Specific Retention Periods

The Third Schedule of the DPDP Rules 2025 lays out clear data retention timelines for large-scale platforms. Once the purpose for which data was collected is fulfilled, these platforms must erase personal data within the defined period with no exceptions.

Here’s what the current retention periods look like:

Platform Type

User Threshold

Retention Period

E-commerce platforms

2 crore+ registered users

3 years from last transaction or login

Online gaming platforms

50 lakh+ registered users

3 years from last transaction or login

Social media platforms

2 crore+ registered users

3 years from last interaction

Note: Always verify these figures against the latest official gazette notification before building your compliance calendar, as rules may be updated.

Which Businesses This Applies To

This schedule does not apply to every business operating in India. Your obligations under the Third Schedule kick in only if your platform crosses the user thresholds specified above.

If you run a small or mid-sized operation well below these numbers, this particular schedule doesn’t bind you though your general data minimization and erasure duties under DPDP Rules 2025 still apply.

Operational Steps Businesses Must Take Immediately
Operational Steps Businesses

A. Conducting a Data Audit and Mapping Exercise

To begin with, it is necessary to create a comprehensive list of all the personal data collected, stored, processed, and disclosed by the organization. The process will provide an understanding of all the areas where there are vulnerabilities. The inventory created is going to serve as the basis for all the further actions related to compliance with the DPDP Rules 2025.

B. Updating Privacy Notices and Consent Mechanisms

Your privacy notices should now be written in clear language and not be too general and vague. You need to review all data gathering points and ensure that consent is sought for purposes which are clearly stated prior to any processing. It should also be easy to withdraw consent.

C. Establishing a Grievance Redressal System

Establish an exclusive communication channel through which data principals can communicate their concerns and requests for correction. The DPDP Rules 2025 have specified specific deadlines for the response to such queries. This can be as simple as a ticketing system with an escalation route.

D. Appointing a Data Protection Officer Where Required

A DPO is mandatory only for Significant Data Fiduciaries as designated by the government. That said, many businesses voluntarily appoint one to manage compliance proactively and build trust with customers, a smart move even if you’re not legally required to do so.

Penalties and Enforcement Businesses Must Prepare For

Financial Penalties for Non-Compliance

The DPDP Rules 2025 come with a sharp penalty structure you cannot afford to ignore. Here’s what’s at stake:

Violation Type

Maximum Penalty

Security safeguard failures

₹250 crore

Breach notification failures

₹200 crore

Children’s data violations

₹200 crore

Significant Data Fiduciary failures

₹150 crore

General non-compliance

₹50 crore

These aren’t theoretical numbers, they’re the actual caps defined under Schedule I of the DPDP Act, 2023.

Source: Schedule I, DPDP Act, 2023 (full text, MeitY)

Regulatory Authority Powers and Oversight Mechanisms

The Data Protection Board of India holds real teeth. It can investigate complaints, summon records, conduct inquiries, and issue binding decisions against your organization. The Board also has the authority to impose penalties and direct remediation all without requiring a court order.

How to Reduce Risk of Enforcement Action

Getting your compliance in order now costs a fraction of what a breach investigation or penalty proceeding will. When you build data governance practices proactively  consent management, breach response, retention policies, you’re not just avoiding fines; you’re protecting your customers and your reputation. Waiting until something goes wrong is always the more expensive option.

How SOCLY.io Simplifies DPDP Rules 2025 Compliance
DPDP Rules 2025 Compliance

Automating Consent Tracking and Data Subject Requests

Manually tracking consent across thousands of users is a nightmare waiting to happen especially when the DPDP Rules 2025 require you to respond to erasure and access requests within a 90-day window. 

SOCLY.io replaces those messy spreadsheets and email chains with automated consent logs that update in real time. When a Data Principal submits a request, the platform routes, tracks, and timestamps it automatically, so you never miss a deadline.

Integrating DPDP Requirements into Existing Security Frameworks

If your organization already runs on SOC 2 or ISO 27001 controls, you don’t need a separate compliance stack for DPDP. SOCLY.io maps DPDP Act Rules 2025 obligations directly onto your existing security framework, giving you a single dashboard to manage data protection requirements alongside your current controls. This means less duplication, fewer gaps, and a cleaner audit trail.

For a deeper look at how SOCLY.io handles end-to-end DPDP compliance automation from breach notifications to Data Fiduciary obligations. 

check out our dedicated DPDP compliance guide. 

If you’re also working on ISO 42001, SOC 2, or ISO 27001, those guides cover how each framework overlaps with your DPDP obligations.

Frequently Asked Questions

When Were the DPDP Rules 2025 Notified? 

The DPDP Rules 2025 were notified in the Official Gazette on 13 November 2025, via Gazette notification G.S.R. 846(E), with MeitY’s public press release following on 14 November 2025. (The draft Rules were published for consultation to the public on 3 January 2025. This was the draft stage, and not the final notice of rules.) The Rules will now be implemented through three phases up to May 2027.

What Are the Requirements for Compliance with the DPDP Act in India? 

Your compliance checklist starts with obtaining free, informed, and specific consent before processing personal data. You also need robust security safeguards, a clear grievance redressal mechanism, and a process to honor data principal rights including the right to access, correct, and erase personal data. Head back to the Core Compliance Requirements section for a full breakdown.

Can You Provide a Summary of the DPDP Rules 2025? 

The Digital Personal Data Protection Rules, 2025 further elaborate on the workings of the DPDP Act, 2023. The Rules deal with issues related to the management of consent, data protection for children, security, and retention of personal data. Significant Data Fiduciaries have to adhere to additional requirements such as conducting audits and DPIAs.

What’s the Difference Between the DPDP Act and DPDP Rules? 

The DPDP Act 2023 sets the legal framework and broad principles. The DPDP Rules 2025 are the operational rulebook spelling out exactly how your business must implement those principles day to day.

Who Is a Significant Data Fiduciary? 

Significant Data Fiduciary is an organization that is designated by the government as a data fiduciary due to the nature, quantity, or risks associated with the data being processed. If your business qualifies for being a significant data fiduciary, you have the obligation of appointing a Data Protection Officer and conducting DPIAs every year.

The DPDP Rules 2025 represent a major change in the way that businesses functioning within the Indian jurisdiction need to deal with personal data. From getting explicit consent to handling data about children, creating retention timelines, and facing stringent fines – the requirements of compliance are very real, very detailed, and very non-negotiable. If you are a business in India – regardless of your size – you cannot ignore this anymore.

Getting compliant doesn’t have to be difficult. It’s all about being aware of the requirements of the laws, taking the appropriate actions, and  leveraging platforms built for this purpose. You can build a strong data privacy framework that protects your users and your business. 

Tools like SOCLY.io are designed to simplify exactly this journey, helping you stay on top of your DPDP obligations without losing focus on what matters most: running your business with trust and accountability at its core.

Ready to Simplify Your Compliance Journey?
Categories
ISO 27001

ISO 27001 Risk Treatment Plan: How to Identify, Evaluate and Treat Security Risks
ISO 27001 Risk Treatment Plan: How to Identify, Evaluate and Treat Security Risks
ISO 27001 Risk Treatment Plan: How to Identify, Evaluate and Treat Security Risks
ISO 27001 Risk Treatment Plan: How to Identify, Evaluate and Treat Security Risks
>ISO 27001 Risk Treatment Plan: How to Identify, Evaluate and Treat Security Risks
ISO 27001 Risk Treatment Plan: How to Identify, Evaluate and Treat Security Risks
Learn how to create an ISO 27001 Risk Treatment Plan by identifying security risks, selecting appropriate controls, assigning responsibilities, and defining practical actions to strengthen your organization's information security.

ISO 27001 Risk Treatment Plan: How to Identify, Evaluate and Treat Security Risks
ISO 27001 Risk Treatment Plan

An ISO 27001 Risk Treatment Plan translates identified security risks into practical actions. Without one, an organization may understand what could happen but lack a clear plan for how to address the risk, who is responsible, and whether the residual risk is acceptable. 

Risk treatment is a required part of implementing an Information Security Management System (ISMS). ISO/IEC 27001:2022 requires organizations to establish and implement an information security risk assessment and risk treatment process. 

 What Is an ISO 27001 Risk Treatment Plan?

ISO 27001 Risk Treatment Plan means documentation that shows how an organization is going to treat risks related to information security during its risk assessment process.

It links identified risks with the chosen treatment, required controls or actions, risk owners, target dates, and expected residual risk. 

A risk treatment does not necessarily involve getting rid of the risk; the organization can choose to either avoid, mitigate, transfer, or accept a risk according to certain criteria.

 Why Is Risk Treatment Important in ISO 27001?

Risk assessment lets you know what can go wrong and the significance of the risk. Risk treatment then asks: what will you do about it?

A process-oriented risk treatment process under ISO 27001 will help organizations:

  • Prioritize risks
  • Assign accountability
  • Select appropriate controls
  • Track remediation actions
  • Document security decisions
  • Evaluate residual risks
  • Showcase a systematic approach to ISO 27001 risk management

ISO/IEC 27001 integrates risk assessment and treatment in the ISMS planning process. It also requires organizations to compare the controls they determine to be necessary with the controls in Annex A and produce a Statement of Applicability (SoA). 

 ISO 27001 Risk Assessment vs. Risk Treatment

These activities are connected but have different purposes.

Risk assessment focuses on understanding risk. It involves identifying risks, analyzing them, and evaluating them against the organization’s criteria.

Risk treatment focuses on deciding what to do with those risks.

Think of it this way:

Risk assessment = “How serious is this risk?”

Risk treatment = “What action should we take?”

Risk management is the broader process that brings these activities together, including identifying, analyzing, evaluating, treating, monitoring, and reviewing risks.

 How to Create an ISO 27001 Risk Treatment Plan

The following ISO 27001 risk treatment process can be used as a practical starting point.

1.Information Security Risk Identification 

Begin with your assets, systems, processes, people, and outside dependencies.

Identify any threats or vulnerabilities that may impact confidentiality, integrity, or availability.

Examples include:

  • Unauthorized access to customer data
  • Phishing and compromised credentials
  • Cloud misconfiguration
  • Ransomware affecting production systems
  • Loss of a critical supplier
  • Accidental deletion of important information

Document the cause, event, affected asset or process, and potential consequence for each risk.

2. Analyze and Evaluate the Risks

Identify the probability and possible effect of the risk according to the method determined by your company.

One way is by assessing the level as low, medium, and high. More sophisticated firms may use numerical ratings or some other criterion.

Consistency is important here. Risks that are similar must have the same criteria.

Afterwards, compare each assessment to your risk acceptance standards. This will help you identify the risks that need treatment and the ones that can be accepted.

3. Select a Risk Treatment Option

Treatments commonly available are:

Avoid the risk: Avoid taking the risk by altering or stopping the activity that presents the risk.

Mitigate the risk: Undertake controls that will decrease the probability and/or consequence of the risk.

Transfer the risk: Transfer part of the risk to a third party through contracts or insurance.

Accept the risk: Accept the risk when it lies within the criteria for acceptance.

The choice of which option to follow would depend on the nature of the risk, the needs of the business, the resources, and the level of risk exposure accepted. Risk treatment affects the risk in many ways.

4. Determine the Necessary Controls

Identify the necessary controls required to implement the chosen response.

This may include, for instance, where the threat is unauthorized access to the production environment, authentication, access review, privileged access management, logging, and monitoring.

Annex A provides a reference set of information security controls. It should not simply be treated as a checklist where every control is automatically required. ISO/IEC 27001 guidance explains that organizations compare controls determined through risk treatment with Annex A and verify that necessary controls have not been omitted.

Organizations can also use controls outside Annex A when their risk treatment requires them. Necessary controls should be reflected in the Statement of Applicability.

5. Create the Statement of Applicability

The Statement of Applicability (SoA) documents the necessary controls, the justification for their inclusion, their implementation status, and the justification for excluding any Annex A controls. 

The SoA and risk treatment plan have different purposes. The treatment plan focuses on actions for addressing risks, while the SoA provides a structured view of necessary controls and their status or justification.

6. Assign Risk Owners and Actions

Every treatment action should have clear ownership.

Record:

  • Risk description and rating
  • Treatment decision
  • Required control or action
  • Risk owner
  • Target date
  • Status
  • Expected residual risk
  • Required approval or acceptance

Clear ownership prevents the risk register from becoming a document that is updated but not acted upon.

7. Evaluate Residual Risk

After controls are implemented, reassess the risk.

The remaining exposure is called residual risk. Compare it with the organization’s risk acceptance criteria.

If the residual risk is acceptable, the appropriate risk owner can approve or accept it according to the organization’s process. If it remains unacceptable, additional treatment may be necessary.

 ISO 27001 Risk Treatment Plan Example

Consider a SaaS company that stores customer information in a cloud database.

Risk: Unauthorized access to the production database.

Initial risk: High.

Treatment: Reduce the risk.

Planned actions:

  • Enforce multi-factor authentication
  • Restrict database access
  • Review privileged accounts regularly
  • Enable security logging and monitoring
  • Remove unnecessary access

Risk owner: Head of Engineering

Target date: 60 days

Residual risk: Medium

Decision: Compare the residual risk with the organization’s acceptance criteria and obtain the required approval.

This ISO 27001 risk treatment plan example shows how a risk moves from identification to treatment and then to residual-risk evaluation.

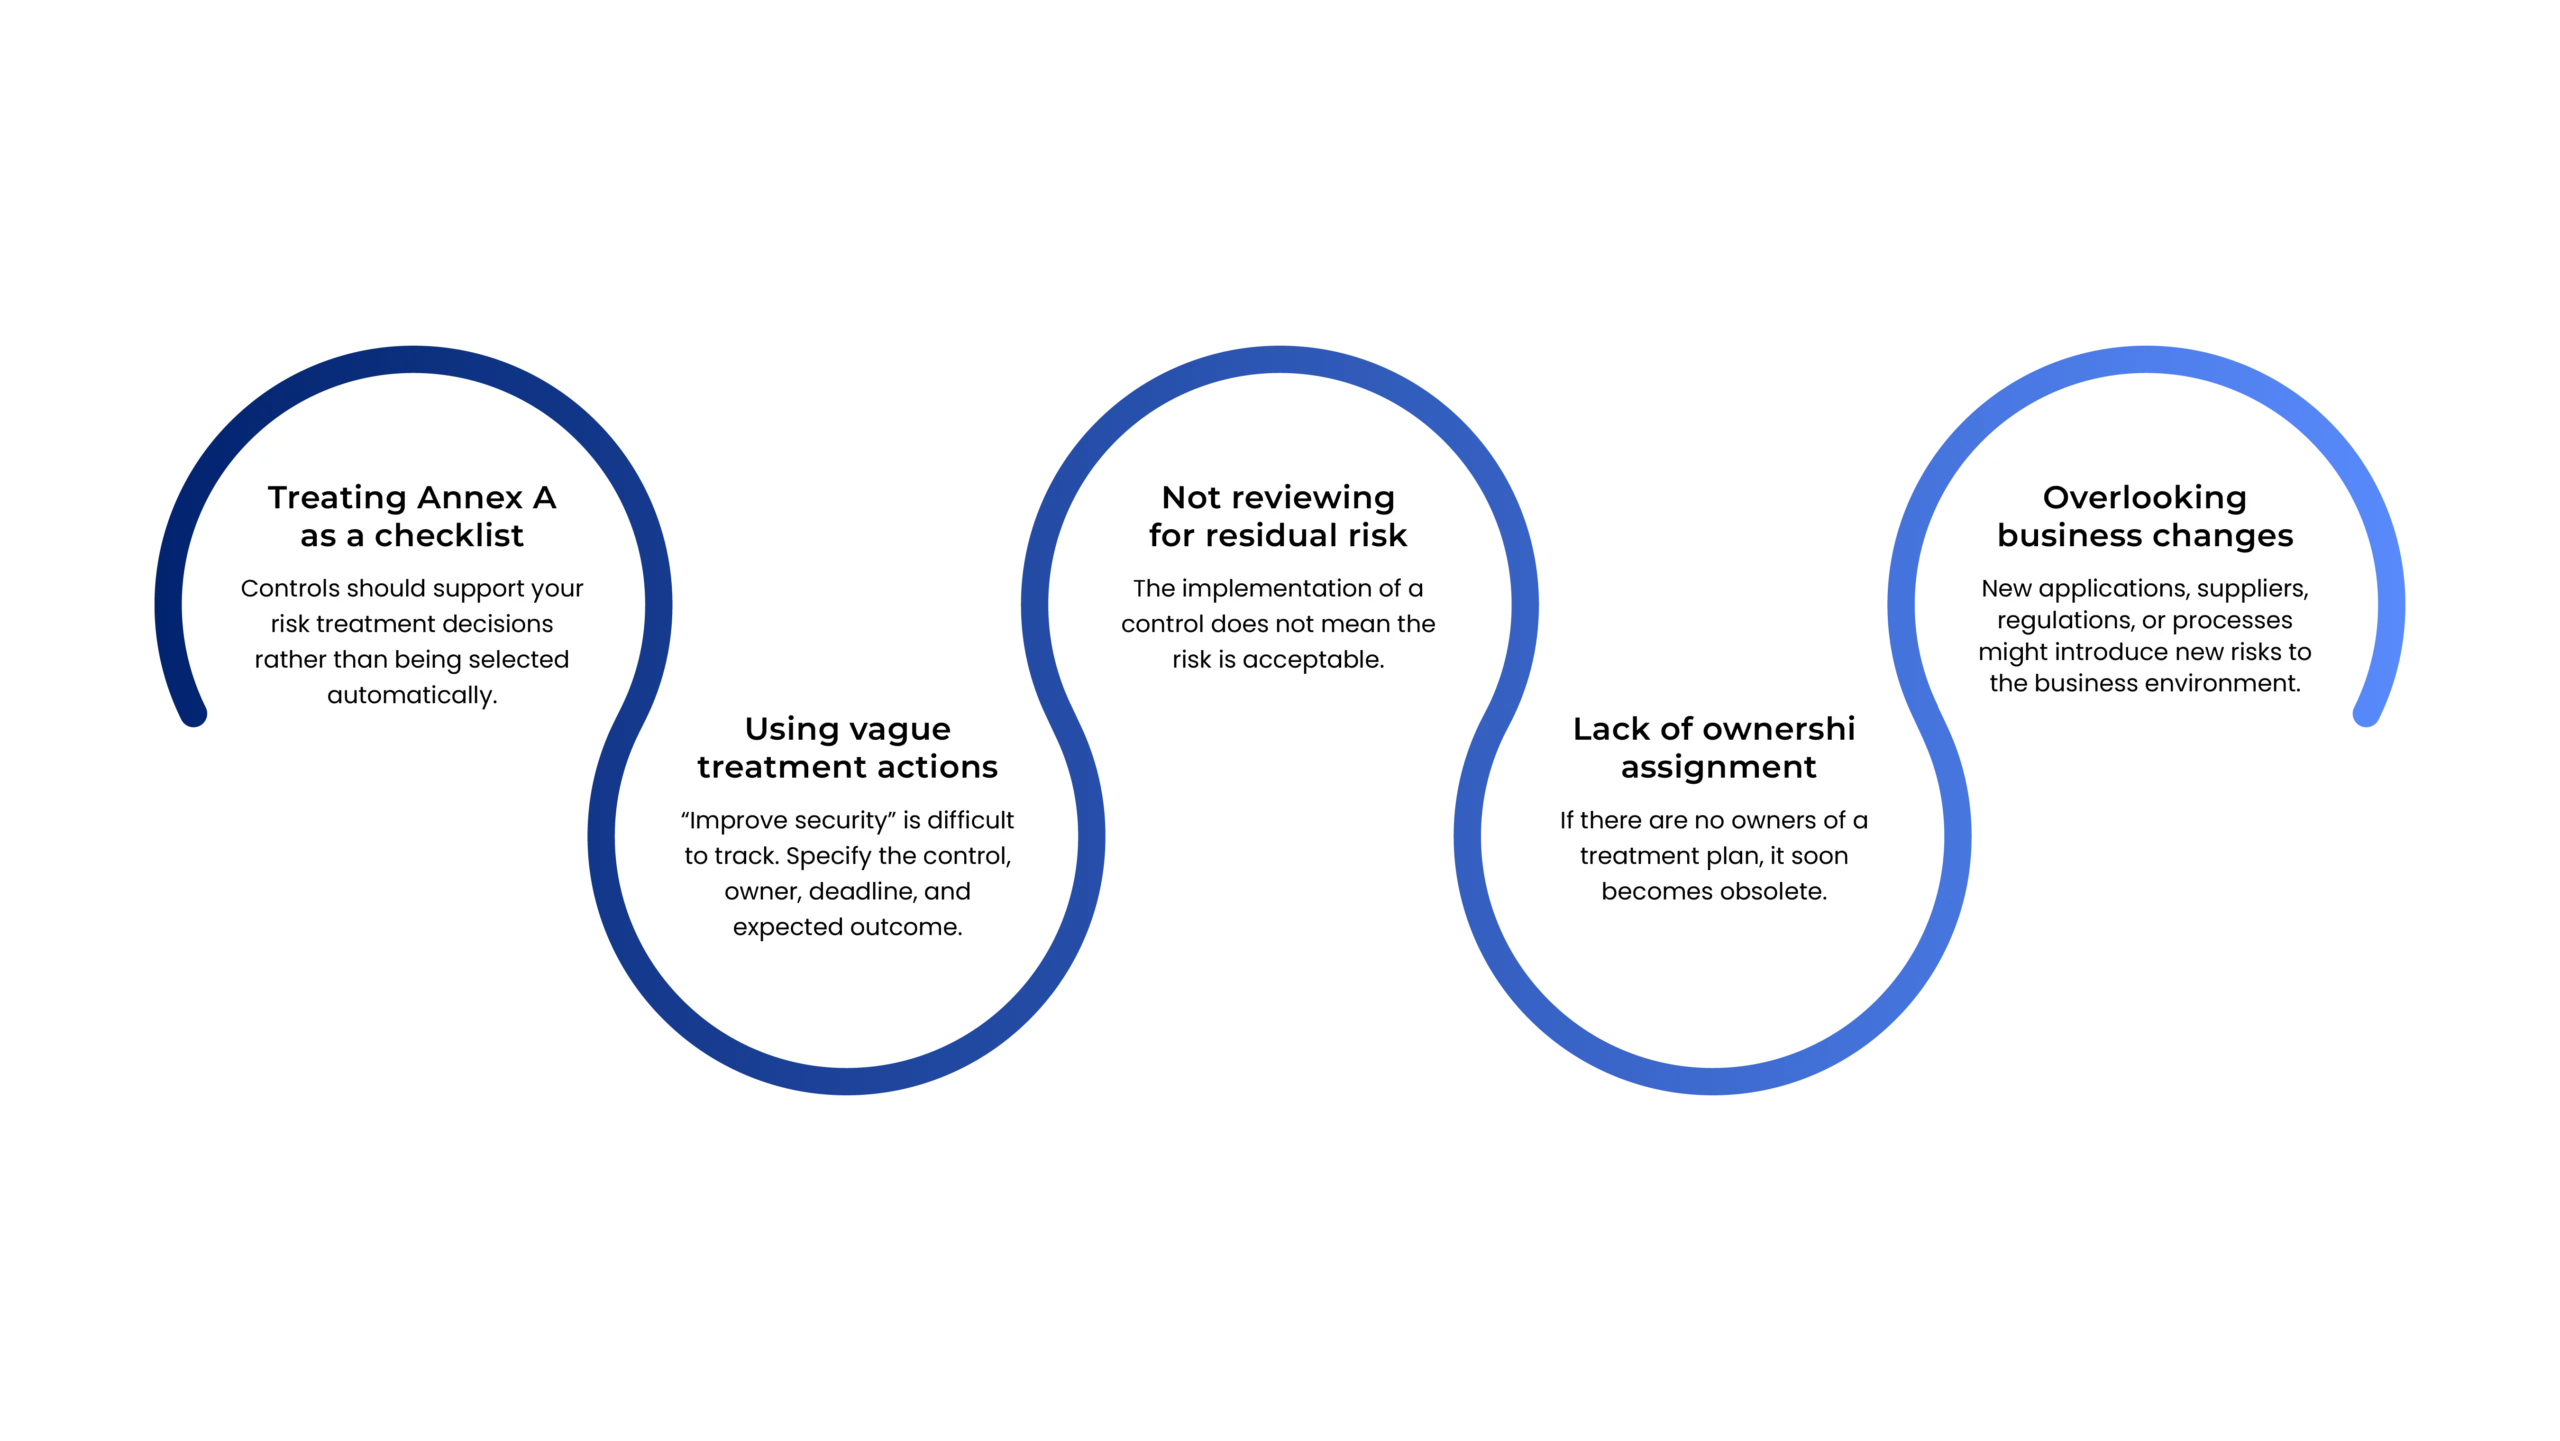
Common Mistakes to Avoid
ISO 27001 Risk Treatment Plan
 ISO 27001 Risk Treatment Plan Checklist

Before finalizing your plan, check that:

  • Risks are clearly described
  • Likelihood and impact are assessed consistently
  • Risk acceptance criteria are documented
  • Each risk has a treatment decision
  • Necessary controls are identified
  • Annex A has been considered
  • The Statement of Applicability is maintained
  • Risk owners are assigned
  • Treatment actions have deadlines
  • Residual risks are evaluated
  • Required approvals are documented
  • The plan is reviewed after significant changes
 Frequently Asked Questions 

What is an ISO 27001 Risk Treatment Plan?

It is a documented plan for deciding and tracking how identified information security risks will be addressed, including treatment actions, ownership, timelines, and residual-risk decisions.

What is ISO 27001 risk treatment?

ISO 27001 risk treatment is the process of deciding how to modify or manage identified information security risks. Options can include avoiding, reducing, sharing, or retaining risk.

How does risk assessment differ from risk treatment?

Risk assessment identifies, analyzes, and evaluates risks. Risk treatment determines what the organization will do about those risks and which controls or actions are needed.

Is an ISO 27001 Risk Treatment Plan mandatory?

ISO/IEC 27001:2022 requires organizations to establish and implement an information security risk treatment process and formulate a risk treatment plan as part of that process. The format and level of detail can be adapted to the organization’s context.

Does every ISO 27001 risk need a security control?

Not necessarily. The treatment decision depends on the organization’s risk criteria and chosen response. A risk may be accepted or addressed through another treatment option where appropriate.

What is the difference between a risk treatment plan and a Statement of Applicability?

The risk treatment plan describes how identified risks will be treated. The Statement of Applicability documents the controls determined to be necessary and explains their inclusion, implementation status, or exclusion justification.

Conclusion

A good ISO 27001 risk treatment plan turns risk assessment into concrete security action. This will help you not only identify risks but assign their owners, implement controls and make decisions regarding residual risk.

It is simple: conduct a consistent risk assessment, decide on treatment according to the criteria, pick up the right controls, record decisions, assign the risk owner and evaluate the residual risk.

If you are developing your ISMS or improving an existing one, risk treatment may be useful for ISO 27001 implementation.

Want to enhance your information security management system? Get in touch to learn more about your ISO 27001 needs.

Ready to Simplify Your Compliance Journey?
Categories
SOC 2

How to Define Your SOC 2 Scope: A Practical Guide for Startups

How to Define Your SOC 2 Scope: A Practical Guide for Startups

How to Define Your SOC 2 Scope: A Practical Guide for Startups

How to Define Your SOC 2 Scope: A Practical Guide for Startups

>How to Define Your SOC 2 Scope: A Practical Guide for Startups

How to Define Your SOC 2 Scope: A Practical Guide for Startups

Learn how to define your SOC 2 scope by identifying the systems, people, processes, and data that support your services, reduce unnecessary compliance work, and prepare your startup for a successful audit.

How to Define Your SOC 2 Scope: A Practical Guide for Startups

SOC 2 Scope

A SOC 2 audit can get unnecessarily complicated if you try to cover all the things that your business does. SOC 2 scope definition will help to limit the audit scope to those systems, individuals, processes, and data that really back up your services.

In startups, defining the scope is perhaps the most crucial step in preparing for a SOC 2 audit. An overly broad scope can lead to an increased compliance burden, whereas an excessively narrow scope may not cover some critical systems and processes.

So, what are the key aspects of defining the scope of SOC 2 for startups? Let’s consider them.

What Is SOC 2 Scope?

Scope of SOC 2 describes the components, services, premises, individuals, processes, technology, and information to be included in a SOC 2 review.

The scope in effect responds to one main question:

What is actually being examined during the SOC 2 examination? 

SOC 2 reviews involve controls associated with one or more of the five AICPA Trust Services Criteria, namely, Security, Availability, Processing Integrity, Confidentiality, and Privacy.

Take, for instance, a cloud software company that offers project management software. Its scope of SOC 2 could be:

  • The production application
  • Production databases
  • Cloud infrastructure
  • Customer data
  • Engineering and DevOps teams
  • Identity and access management
  • Incident response processes
  • Relevant third-party service providers

It may exclude unrelated internal systems, such as a separate marketing website, if those systems do not support the service being examined.

 Why SOC 2 Scope Matters for Startups

A clear SOC 2 audit scope gives your team a practical boundary for compliance work.

Without defined boundaries, startups can spend time creating controls and collecting evidence for systems that have little connection to the service being audited.

A well-defined scope can help you:

  • Reduce unnecessary compliance work
  • Identify the controls that actually matter
  • Organize evidence more efficiently
  • Clarify responsibilities across teams
  • Communicate the audit boundary to your auditor
  • Give customers a clearer understanding of what the SOC 2 report covers

The AICPA describes SOC 2 examinations as assessments of controls at a service organization relevant to security, availability, processing integrity, confidentiality, or privacy.

That makes scope an important part of establishing what your organization is actually asserting about its systems and controls.

What Should Be Included in SOC 2 Scope?

There is no single scope that works for every startup. Your scope should reflect the services you provide and the systems used to deliver them.

Here are the main areas to evaluate.

1. Products and Services

Start with the product or service your customers rely on.

Ask:

  • Which product is being audited?
  • Which services are included?
  • Which customer-facing features depend on the system?
  • Are multiple products sharing the same infrastructure?

If your company has several products, you may not need to include every product in the same SOC 2 engagement. Discuss the appropriate boundary with your auditor.

2. Systems and Technology

Identify the technology that supports the in-scope service.

This may include:

  • Cloud infrastructure
  • Production servers
  • Databases
  • Applications
  • APIs
  • Storage systems
  • Monitoring tools
  • Identity and access management platforms
  • Backup systems
  • Security tools

Create an inventory before finalizing the scope. This makes it easier to identify dependencies that could otherwise be missed.

3. Data

Next, determine what information the in-scope systems handle.

Consider:

  • Customer information
  • Authentication data
  • Business information
  • Application data
  • Confidential information
  • Personal information
  • Logs and security data

You should understand where this data is collected, processed, stored, transmitted, and deleted.

4. People and Teams

SOC 2 scope is not limited to technology.

Employees and contractors whose activities affect the in-scope service may also be relevant. Depending on your organization, this could include:

  • Engineering
  • DevOps
  • Security
  • IT
  • Customer support
  • Compliance
  • Management

For example, if engineers can deploy changes to production, their access and change-management responsibilities may be relevant to the audit.

5. Third-Party Vendors

Startups often rely heavily on cloud and SaaS providers.

Review vendors such as:

  • Cloud hosting providers
  • Payment processors
  • Authentication providers
  • Customer support platforms
  • Monitoring services
  • Data storage providers
  • Communication tools

Determine whether each vendor supports an in-scope system or process. Also identify whether the vendor’s controls affect your own control environment.

How to Define SOC 2 Scope for Startups

A practical SOC 2 scope definition can be created in five steps.

Step 1: Identify the Service Being Audited

Begin with the service customers purchase or use.

Write down exactly what the service does and which customer-facing functions are included.

This gives you a starting point instead of attempting to audit the entire company.

Step 2: Map the Supporting Systems

Create a simple flow showing how the service works.

For example:

Customer → Application → API → Database → Cloud Infrastructure

Then add the supporting components around that flow, such as identity management, monitoring, backups, deployment systems, and security tools.

This system map can reveal dependencies that should be considered when defining your scope.

Step 3: Identify People and Processes

Document the teams and processes that support those systems.

Look at areas such as:

  • User access
  • Employee onboarding and offboarding
  • Software development
  • Change management
  • Incident response
  • Risk management
  • Security monitoring
  • Backup and recovery

Ask whether each process affects the security, availability, integrity, confidentiality, or privacy of the in-scope service.

Step 4: Review the Trust Services Criteria 

While security is always an issue for SOC 2, other criteria may be included by the organization depending on its situation, such as Availability, Processing Integrity, Confidentiality, or Privacy.

Don’t just list all the criteria. Identify the criteria that are important to the service and the commitments being made.

Step 5: Test the Boundary Against Your SOC 2 Auditor

Prior to completing your scope, validate it against your SOC 2 auditor.

They can help ensure that the proposed boundary accurately reflects the system under evaluation and that any relevant dependencies have been identified and accounted for. 

This step is particularly crucial for startups with complex cloud configurations, shared infrastructure, multiple products, and heavy dependencies on third parties.

A Simple SOC 2 Scope Example

Consider a startup that provides an AI-powered customer support platform.

Its initial scope might include:

In scope:

  • Customer-facing SaaS application
  • Production AWS environment
  • Customer database
  • Application logs
  • Engineering and DevOps teams
  • Production deployment process
  • Access management
  • Incident response

Potentially out of scope:

  • Internal marketing website
  • Unrelated experimental application
  • Office facilities that do not affect the service
  • Internal tools with no connection to customer data or production systems

The exact boundary depends on how the startup’s environment is designed. The goal is not simply to exclude systems. The goal is to establish a defensible boundary that accurately represents the service and controls being examined.

Common SOC 2 Scoping Mistakes

Startups often make a few avoidable mistakes when defining scope.

SOC 2 Scope

Review your boundary regularly rather than treating it as permanent.

SOC 2 Scope Checklist for Startups

Before finalizing your scope, ask:

  • What customer-facing service is being audited?
  • Which applications support that service?
  • Which infrastructure is required?
  • What customer or sensitive data is processed?
  • Which teams operate the in-scope systems?
  • Which processes affect those systems?
  • Which third-party vendors are involved?
  • Which Trust Services Criteria are relevant?
  • What systems or services are intentionally excluded?
  • Has the proposed boundary been reviewed with the auditor?

If you can answer these questions clearly, you have a much stronger foundation for your SOC 2 preparation.

 Frequently Asked Questions About SOC 2 Scope

1. What is SOC 2 scope?

SOC 2 scope defines the services, systems, people, processes, technologies, and data covered by a SOC 2 examination.

2. How do you define the scope of a SOC 2 audit?

Start by identifying the service being examined, then map its supporting systems, data, people, processes, and vendors. Finally, determine the relevant Trust Services Criteria and validate the boundary with your auditor.

3. What should be included in SOC 2 scope?

Typically, the scope includes systems, infrastructure, applications, data, employees, processes, and third-party dependencies that support the service being examined. The exact scope depends on the organization’s environment.

4. Can a startup exclude systems from SOC 2 scope?

Yes, systems that do not support the in-scope service may potentially be excluded. However, exclusions should be based on the actual system boundary and dependencies rather than simply removing systems to reduce audit effort.

5. Should all five Trust Services Criteria be included?

Not necessarily. SOC 2 can address Security, Availability, Processing Integrity, Confidentiality, and Privacy. The relevant criteria depend on the service, risks, customer expectations, and engagement objectives.

6. Does SOC 2 scope change as a startup grows?

It can. New products, infrastructure, vendors, data flows, and business processes may change the systems supporting the service. Startups should periodically review whether their documented scope still accurately represents their environment.

Conclusion

The task of defining the scope of SOC 2 isn’t about including as many systems into the audit as possible. The goal is to define the scope of your service in a clear and correct manner.

For new businesses, the simplest way is to define the service, map out its dependencies, identify the controls and the Trust Services Criteria related to it, list exclusions, and confirm the boundaries with the help of your auditor.

A properly defined scope will help you to better prepare for SOC 2 and deal with it as your business grows.

Want to simplify SOC 2 preparation? Contact us to discuss your compliance needs.

Ready to Simplify Your Compliance Journey?
Categories
ISO 42001

ISO 42001 Certification: 2026 Guide to Requirements, Cost, Timeline & Process

ISO 42001 Certification: 2026 Guide to Requirements, Cost, Timeline & Process

ISO 42001 Certification: 2026 Guide to Requirements, Cost, Timeline & Process

ISO 42001 Certification: 2026 Guide to Requirements, Cost, Timeline & Process

>ISO 42001 Certification: 2026 Guide to Requirements, Cost, Timeline & Process

ISO 42001 Certification: 2026 Guide to Requirements, Cost, Timeline & Process

Learn how ISO 42001 certification helps AI SaaS companies manage AI risks, strengthen governance and oversight, meet evolving requirements, and build trust through responsible AI practices.

ISO 42001 Certification: 2026 Guide to Requirements, Cost, Timeline & Process

ISO 42001 Certification Cost, Timeline & Process

Getting ISO 42001 certified means demonstrating that your company manages AI systems through documented risk management, controls, oversight, and continuous monitoring, which are verified by an independent third-party auditor. ISO 42001 for AI SaaS companies is becoming increasingly important as SOC 2 already is: companies that develop, deploy, or provide AI-enabled software may benefit from understanding ISO 42001 regardless of being an AI startup with five people or a 500-people SaaS firm looking to implement AI into your product.

You may have come across this standard because of a customer security questionnaire, investor due diligence, or the growing focus on the EU AI Act and decided to prepare for potential questions from the regulators. No matter what led you here, this guide provides all the information that really matters – the cost of certification, duration of the process, expectations of the auditors, and much more.

What Is ISO 42001 Certification, Actually?

ISO/IEC 42001:2023 is the first international standard for an AI Management System (AIMS). Released in December 2023 by ISO and IEC, the standard offers companies a framework for managing the risks and responsibilities associated with the development or implementation of AI technology.

The following distinction is crucial: the standard refers to the document itself – a set of requirements, while the certification process is the procedure where an accredited independent auditor confirms compliance with the standard requirements and issues a certification valid for three years (assuming all annual surveillance audits go well).

In other words, when somebody claims that “we’re ISO 42001 certified”, they mean that an external auditor has checked that their AI governance system is implemented, not just created on paper.

Who is ISO 42001 intended for?  Any organization involved in the development, provision, or implementation of AI technology, regardless of its size and industry. This is intentionally a broad definition; there is no need to develop foundation models to require this standard. If your SaaS product has AI functionality, if you apply AI in order to make decisions regarding your customers, or if you re-sell AI-powered solutions to your customers, the ISO 42001 standard is applicable.

If you’re also processing personal data, especially of users in India alongside your AI systems, it’s worth reading our DPDPA compliance guide alongside this one, since the two increasingly overlap for AI-driven products.

Why Get ISO 42001 Certified? (The Business Case, Not Just the Compliance Case)
ISO 42001 Certified

Certification isn’t just a box to check for regulators. For most of the companies we work with, it’s a sales enabler.

Benefits of ISO 42001 Certification for Businesses

Here’s what an AI governance certification for startups and growing companies actually delivers in practice:

Enterprise clients are already demanding it. More and more enterprise customer security questionnaires now contain AI governance questions. Providing a certificate instead of a three-paragraph explanation of your internal AI policy can help streamline your sales process. 

It prepares you for regulations in advance. The EU AI Act is being implemented in phases through 2026 and beyond. ISO 42001 won’t be a mandatory regulation under the Act and it won’t necessarily prove compliance, but an existing AIMS would make compliance significantly easier.

It is a clear competitive advantage. When competing with a rival in an RFP process, and you happen to have a proper AI governance certification while they don’t have anything of the sort, that’s an actual competitive advantage you can leverage. This is similar to how SOC 2 has helped SaaS companies demonstrate security and build trust with enterprise customers. 

It replaces all the scattered documents with one framework. All scaling companies have some form of AI governance, some policy documents here, some approval processes there, but it’s always scattered and messy. ISO 42001 pushes you to build them all into a cohesive framework.

ISO 42001 Certification Cost. What to Actually Budget For

This is the question nobody seems to answer directly, so let’s break it down by component instead of throwing out one number that won’t apply to your situation.

ISO 42001 gap assessment / readiness review. Before implementation begins, you need to assess your gaps against the requirements of the standard. Typically, it is an engagement that is quite short and targeted, which may be either internal (using the time of your team) or conducted by a consultant or a platform. It is often the first item in the budget because it shows what needs to be addressed before implementation begins. 

Internal implementation effort. This is the cost that gets overlooked in planning: the time of your own people. Policies, risk registers, an inventory of your AI systems, and monitoring processes – it all takes real time from your security team, engineers, and management. This is usually the single largest cost for startups in terms of weeks of effort, rather than money.

Certification body audit fees. You will pay a certification body for both the Stage 1 and Stage 2 audits. The charges will be different depending on various factors such as the certification body, size of your business, and audit scope.

Annual surveillance audits. Certification is not a one-time cost either. Surveillance audits will be done in the first and second years, after which there will be a recertification audit in the third year. This should be budgeted as a recurring expense.

Optional: consultant or automation platform. This is where the real cost difference shows up between approaches.

Approach

Typical Cost Profile

Typical Time Investment

DIY (in-house only)

Lowest direct spend, highest hidden cost

Highest,  months of internal time, especially evidence collection

Consultant-led

Higher direct spend

Faster than DIY, but you’re still manually managing evidence and documentation long-term

Automated platform (like SOCLY.io)

Predictable subscription cost

Fastest, automation handles evidence collection and monitoring continuously, not just for the audit

However, the hidden cost in both of these methods is nearly always the same – manual data collection. Your team members will spend weeks gathering screenshots, exporting logs and compiling outdated Excel sheets. This is precisely what automation helps to solve, which we will discuss further down in this guide.

The total cost depends on your organization’s size, AI system scope, existing controls, certification body, and implementation approach.

Want a real number instead of a range? 

Get a free ISO 42001 cost estimate based on your specific setup. We’ll walk through your current AI systems and existing certifications to give you an accurate picture.

How Long Does ISO 42001 Certification Take?

Nobody publishes a straight answer to this, so here’s a realistic ISO 42001 audit timeline, broken down phase by phase based on how certification projects typically unfold:

  1. Gap assessment — 1 to 2 weeks
  2. Policy and control implementation — 4 to 12 weeks, depending on how mature your AI governance already is
  3. Internal audit and management review — 1 to 2 weeks
  4. Stage 1 audit (documentation review) — around 1 week
  5. Stage 2 audit (implementation review) — 1 to 2 weeks
  6. Certificate issuance — 2 to 4 weeks after Stage 2 completes

Taken together, these steps mean a lean startup with relatively mature security practices may be able to complete the process in three to five months. And for a bigger business with more complex artificial intelligence and more approvals, the process will take longer.

What makes it faster:

  • Existing SOC 2 and ISO 27001 means most of the underlying controls (access management, incident response, monitoring) are directly aligned with ISO 42001 requirements
  • Automation for evidence gathering and continuous monitoring right from the beginning, rather than trying to figure out how to do it for the audit

What makes it slower:

  • No existing inventory of places where artificial intelligence is actually being utilized
  • Manual evidence gathering using spreadsheets that have to be redone each time something changes

If you are working on SOC 2 or ISO 27001, it would be a good idea to work on ISO 42001 as well you’ll save yourself some time by the amount of evidence overlapping alone.

ISO 42001 Requirements Checklist

Use this as a working checklist, organized by the core pillars of an AI Management System:

Leadership & Policy

  • Documented AI policy approved by leadership
  • Clear ownership assigned for AI governance
  • AI objectives defined and tied to business goals

Risk Management

  • AI risk assessment process in place
  • Risk treatment plans documented for identified risks
  • Risks reviewed and updated on a regular cycle

Data Governance

  • Data quality and provenance controls for AI training/input data
  • Data privacy safeguards integrated into AI systems

Lifecycle Management

  • Controls covering AI system design and development
  • Deployment approval process
  • Ongoing monitoring once systems are live
  • Defined process for retiring or replacing AI systems

Transparency & Communication

  • Clear communication to stakeholders about how AI is used
  • Process for handling AI-related questions or complaints from customers

Third-Party & Vendor Management

  • Risk assessment process for AI vendors and tools you rely on
  • Contractual safeguards with AI vendors

Internal Audit & Continual Improvement

  • Scheduled internal audits against the standard
  • Management review process
  • Documented Plan-Do-Check-Act cycle for continuous improvement

Save or bookmark this list, you’ll want to revisit it as you move through implementation.

How to Get ISO 42001 Certification for Startups: Step-by-Step Process 

You don’t need a dedicated compliance team to pull this off. Here’s the realistic path for a lean team:

  1. Map where AI is actually used across your product and internal tools. Most teams underestimate this until they sit down and list it out.
  2. Run a gap assessment against the ISO/IEC 42001 clauses to see where you already meet requirements and where the gaps are.
  3. Assign an owner. This doesn’t need to be a full-time role; often, your head of security or engineering can take ownership alongside their existing responsibilities. 
  4. Build and document the required policies and controls identified in your gap assessment.
  5. Automate evidence collection instead of manually tracking it in spreadsheets. This is the step most startups skip and pay for later in audit delays.
  6. Complete an internal audit and management review before you bring in an external auditor.
  7. Choose an accredited certification body (more on how to pick one below).
  8. Pass Stage 1 and Stage 2 audits.
  9. Maintain certification through continuous monitoring, not a scramble before each surveillance audit.

Teams can move through the process more efficiently when they plan for evidence collection and monitoring from the beginning. 

This is basically the complete answer to the question of how you can achieve an ISO 42001 certification without wasting months on the effort of your team.

Not sure where your team stands on this list? Talk to a compliance specialist about your specific timeline and get a clear starting point.

How to Choose a Certification Body

This part rarely gets explained clearly, so here’s what actually matters.

“Accredited” has a specific meaning. A certification body needs to be accredited by a recognized accreditation body organizations like ANAB (in the US) or UKAS (in the UK) specifically for ISO/IEC 42001. Accreditation for ISO 42001 is still relatively new; ANAB launched its AIMS accreditation program in January 2024, and the pool of accredited certification bodies is smaller than it is for older standards like ISO 27001. Check the relevant accreditation body’s public directory before you commit to one.

Questions to ask before hiring a certification body:

  • Do they have experience certifying companies whose AI systems resemble yours?
  • What is their realistic audit turnaround for Stages 1 and 2?
  • Is their billing system straightforward, or will there be surprise charges along the way?
  • Do they provide a pre-assessment or readiness assessment prior to the formal audit?

A straight truth: SOCLY.io does not certify, no automation platform can do it. We prepare your evidence, control procedures and monitoring so you can be fast at Stage 1 and 2 with whichever certification body you select.

ISO 42001 vs Other Frameworks
ISO 42001 vs SOC 2 for AI Companies

They are not competing frameworks; they address different areas. SOC 2 is all about controls surrounding security, availability, and confidentiality in relation to your systems. On the other hand, ISO 42001 is concerned with the governance of AI including risk management, lifecycle management, and responsible usage.

The good thing is that most SaaS businesses that have their attention on AI will try to get both standards because customers will be looking for both. The good thing here is that there are many commonalities when it comes to the evidence.

If you’re starting from scratch on the security side, our SOC 2 certification guide is a good place to begin.

ISO 42001 vs. NIST AI RMF

The AI Risk Management Framework developed by NIST is the American voluntary standard that has its use but is not certifiable, meaning there is no audit and there will be no certificate issued. In case you sell your product abroad, or you need some document for your security review, you should use the ISO 42001 standard.

Framework

Certifiable?

Region Focus

Best For

ISO/IEC 42001

Yes

Global

Companies needing third-party verified AI governance

NIST AI RMF

No

US-focused

Companies wanting structured guidance without a formal audit

Companies selling internationally, or selling into enterprises that expect a real certificate, tend to need ISO 42001 specifically — NIST AI RMF alone won’t satisfy that requirement.

What Evidence Do Auditors Actually Ask For?

That is when many organizations find themselves blindsided. The auditors aren’t merely interested in your policies but in the proof that you’ve put them into practice. 

You should be prepared to supply:

  • Inventory of your AI systems and where they are in use
  • A record of risk register, outlining all of the risks and mitigation strategies employed
  • Documentation of data governance, related to the data powering your AI systems
  • Logs of monitoring activities that prove your AI systems are monitored and not merely deployed and left alone
  • Incident management documentation, including all AI-related incidents and how you’ve managed them
  • Proof that people who manage AI systems are trained and know about their responsibility in relation to AI systems

Notice the amount of overlap between this and what a SOC 2 and ISO 27001 auditor would need. This overlap is precisely why using one platform to deal with all of those frameworks saves you time.

How Automation Shortens ISO 42001 Certification
Automation Shortens ISO 42001 Certification

And here’s how manual preparation for certification really works: one person spends a week taking screenshots of access controls, one week trying to get engineering to provide system logs, and then finds out a month down the road that half the evidence is outdated since some change was made in production. Repeat that for each and every control in the standard, and you’ll understand why certification processes take three months or more.

The SOCLY.io platform automates several parts of the process: 

  • Evidence mapping automation – the evidence is collected and mapped to the ISO 42001 controls automatically and continuously, not gathered at the last minute.
  • Real-time monitoring – your AI systems are monitored 24/7, so you won’t find gaps in coverage only when the auditor does;
  • Centralized dashboard – all your controls status in one place, no need to dig through a bunch of documents;
  • Human expertise support – compliance specialists who will help you before, during, and after the audit.

This is not an attempt to replace judgment with technology; rather, this is the removal of mundane aspects of compliance that cause errors and take your time away from focusing on decisions where human judgment is necessary.

Maintaining Certification: What Happens After You Pass

However, certification is not the end of the process. The validity of your certificate lasts three years, but there will be surveillance audits in the first year and second year to check whether you meet the standard, after which there will be a recertification audit in the third year.

In practice, that means:

  • Constant monitoring of your AI systems, not just during the audit period
  • Updating risk assessments when you introduce changes to existing AI systems or add new ones 
  • Periodic internal audits to detect the problems ahead of an external auditor

And it is exactly the reason why a platform is more likely to work better than a one-time consulting project. A consultant will help you become certified. A platform can help you remain audit-ready continuously, making each next surveillance audit easier and less time-consuming.

Frequently Asked Questions

Is ISO 42001 certification mandatory? 

ISO 42001 is not mandatory. However, it is becoming more relevant to enterprise customers and can provide a structured governance framework as organizations prepare for regulations such as the EU AI Act. It does not automatically demonstrate legal compliance but gives rewards to companies having governance systems in place.

How much does ISO 42001 certification cost for a small startup? 

The costs will vary depending on the certification body, scope of AI systems, and implementation method (in-house, consultant, or automated). The biggest cost underestimated by startups is the cost of manual data gathering, which automation tries to minimize.

How long does ISO 42001 certification take? 

The period from kickoff to certificate for most organizations is generally between three and five months, based on how advanced their AI governance and security practices are.

Who can issue ISO 42001 certification? 

ISO/IEC 42001 can only be certified by accredited certification bodies for ISO/IEC 42001 through a recognized accreditation body such as ANAB and UKAS. Always verify that the accreditation is valid first.

Does ISO 42001 apply to companies that use AI tools but don’t build them? 

Yes. The standard applies to any organization that provides or uses AI systems; you don’t need to be building your own models to need an AI management system.

Can one platform manage ISO 42001 alongside SOC 2 or ISO 27001? 

Yes, and it’s something that will definitely be worth your while. There is substantial similarity in the basic data and controls between the different systems, which makes it quicker to coordinate them as opposed to working on them separately.

What happens if you fail a Stage 2 audit?

You will normally be provided with a certain amount of time to rectify any non-conformities, after which you may be subject to re-evaluation, rather than having to start everything from scratch. Another good reason why it is important to prepare thoroughly for the audit.

How does ISO 42001 relate to the EU AI Act? 

ISO 42001 is not a harmonized standard by the EU AI Act and does not guarantee any legal compliance for that matter. All ISO 42001 does is provide you with an operational governance framework that would make it much easier for you to showcase your risk management and oversight efforts.

Ready to Get Started?

ISO 42001 certification doesn’t have to mean months of manual work and scattered spreadsheets. The right process and automation will allow you to complete the task much faster than you anticipated.

Get your free ISO 42001 gap assessment and see exactly where you stand. Or, if you’re also working on SOC 2, ISO 27001, or DPDPA, check out our other compliance guides to see how these frameworks overlap.

Ready to Simplify Your Compliance Journey?
Categories
CCPA

Who Needs to Comply With CCPA? A Guide for SaaS Businesses

Who Needs to Comply With CCPA? A Guide for SaaS Businesses

Who Needs to Comply With CCPA? A Guide for SaaS Businesses

Who Needs to Comply With CCPA? A Guide for SaaS Businesses

>Who Needs to Comply With CCPA? A Guide for SaaS Businesses

Who Needs to Comply With CCPA? A Guide for SaaS Businesses

Learn who needs to comply with the CCPA, understand its key requirements for SaaS companies, and discover how to protect California consumers’ personal data while strengthening privacy practices and customer trust.

Who Needs to Comply With CCPA? A Guide for SaaS Businesses

Comply With CCPA

Even if your SaaS startup is not based in California, it can still be subject to the CCPA if it meets the applicable requirements. What is crucial is not only the location of your business, but whether your business falls under the category of a covered business according to the CCPA.

The California Consumer Privacy Act (CCPA) grants rights to Californian citizens in relation to personal data and imposes duties on certain covered businesses. It is essential for SaaS companies to understand who needs to comply with the CCPA, because customer data might go through various online tools such as websites, applications, CRMs, analytics software, payment systems, and third-party service providers.

In general, the CCPA is applicable to profit-making companies that conduct business in California, handle personal information about California consumers, determine the purposes and means of processing such personal information and satisfy at least one of the statutory thresholds.

The key thresholds are:

  • An annual gross revenue of $26.625 million or more on the basis of the relevant 2025 inflation-adjusted threshold.
  • Purchase, sale or sharing of the personal information of 100,000 or more California residents or households in the relevant year.
  • Generating 50% or more annual revenues through selling or sharing personal information of California residents.

This means that the CCPA could also be applicable to entities under control of the covered business and joint ventures.

In regard to SaaS startup companies, the critical point to remember is very straightforward: just because you’re a small company or not based in California doesn’t mean you’re exempt from the CCPA.

What Is the CCPA?

The California Consumer Privacy Act, or CCPA, is California’s major consumer privacy law. It gives California residents rights concerning the personal information businesses collect, use, and share about them.

The law was originally enacted in 2018 and was later amended by the California Privacy Rights Act (CPRA). The CPRA amendments became effective January 1, 2023, and the California Privacy Protection Agency (CPPA) now plays a major role in implementing and enforcing the law.

Among other rights, California consumers can have rights to:

  • Know what personal information a business collects
  • Know how that information is used and shared
  • Request deletion of personal information, subject to exceptions
  • Opt out of the sale or sharing of personal information
  • Limit certain uses and disclosures of sensitive personal information
  • Receive equal treatment for exercising their privacy rights

This makes CCPA compliance more than simply adding a privacy policy to a website.

Who Is Subject to CCPA Compliance?

One such misconception is the assumption that all companies doing business in California need to adhere to the CCPA.

That is not true. The CCPA usually applies to companies that satisfy certain requirements.

1. For-Profit Businesses That Do Business in California

The CCPA generally applies to for-profit businesses that:

  1. Do business in California.
  2. Collect California consumers’ personal information, or have it collected on their behalf.
  3. Determine the purposes and means of processing that personal information.
  4. Meet at least one applicable statutory threshold.

This implies that a business does not necessarily have to have a physical office in California in order to be bound by the CCPA.

For instance, consider a SaaS startup based in Texas selling project management software to businesses all over the U.S. If such a firm has users from California and hits one of the CCPA thresholds, it could be covered by the law.

The Three Main CCPA Thresholds

Understanding the thresholds is one of the easiest ways to determine whether your business may be covered.

Threshold 1: Annual Revenue

Whether or not the CCPA applies to a business depends on whether its gross annual income meets the statutory threshold.

The CCPA threshold for 2025 has been adjusted due to inflation and stands at $26.625 million. It is important to keep in mind that the threshold gets adjusted due to inflation.

Example:

The SaaS firm makes annual gross revenue of $30 million and has a subscription service that is being used by the customers in California.

It doesn’t matter how many customers come from California – if the business meets the applicable revenue threshold and the other requirements for CCPA coverage, it may be subject to the CCPA regardless of the number of California customers.

Threshold 2: Processing Personal Information of 100,000+ Consumers or Households

An organization could also be subject to the CCPA if it buys, sells, or shares the personal information of 100,000 or more California residents or households, subject to the applicable statutory requirements.

This threshold is critical for many SaaS organizations that have large numbers of users.

As an illustration, take into account a free SaaS product that has 150,000 users from California.

While the organization might lack $26.625 million in income, the nature of its activities can imply CCPA applicability.

Threshold 3: 50% or More Revenue From Selling or Sharing Personal Information

Another way that a company could fall under CCPA is if more than half of its yearly revenue comes from selling or sharing the personal information of California residents.

This standard is especially applicable for companies whose business models involve selling or sharing personal information.

While this scenario is probably less applicable to most B2B SaaS startups, it should nevertheless not be overlooked.

Does CCPA Apply to Small Businesses?

Yes, potentially, but not all small businesses are covered by the CCPA.

The size of the organization does not automatically make compliance with CCPA mandatory.

A small SaaS startup may not be covered by the law if it fails to meet certain criteria. Conversely, a small organization may still be subject to the CCPA if it meets the applicable requirements.

Take, for instance, two SaaS startups:

Startup A

  • $5 million annual revenue
  • 15,000 California users
  • Doesn’t sell or share personal information

It may not meet the main CCPA business thresholds.

Startup B

  • $8 million annual revenue
  • 150,000 California users
  • Buys, sells, or shares qualifying personal information at the applicable threshold

Its data-processing activities could trigger CCPA coverage even though its revenue is well below the revenue threshold.

The lesson is important: don’t use employee count or startup size as your only compliance test.

What Businesses Need to Comply With CCPA?

For businesses operating under the SaaS model, the first step is to determine whether the business meets the applicable criteria.

If it does, the next step is understanding the practical CCPA requirements for businesses.

Covered businesses may need processes for handling consumer privacy rights, including requests related to:

  • Accessing personal information
  • Deleting personal information
  • Correcting certain personal information
  • Opting out of sale or sharing
  • Limiting certain uses of sensitive personal information

Businesses should also maintain an appropriate privacy notice and processes for handling consumer requests.

This will entirely depend upon the nature of the business as well as the applicable CCPA requirements.

CCPA Compliance for SaaS Companies: What Does It Look Like?

For a SaaS startup, CCPA compliance isn’t limited to the marketing website.

Personal information can move through the entire technology environment.

A typical data flow might look like:

Website
CRM
SaaS Application
Cloud Infrastructure
Analytics
Customer Support

Each system can create privacy considerations.

1. Map the Personal Information You Collect

Start by identifying what personal information enters your environment.

For example:

  • Names
  • Email addresses
  • Phone numbers
  • Account information
  • IP addresses
  • Device information
  • Online identifiers
  • Usage information
  • Geolocation information
  • Customer support records

The CCPA definition of personal information is broad and can include information that identifies, relates to, or could reasonably be linked with a consumer or household.

2. Understand Why You Collect It

Ask a simple question for every major data category:

Why do we need this information?

If your product gathers data without a clearly defined business rationale, then ask yourself if it is really necessary.

For instance, a software as a service (SaaS) tool for managing projects might require an email address in order to make an account, but gathering additional unnecessary data could create privacy risks.

3. Review Your Third-Party Vendors

SaaS startups rarely operate alone.

They may use:

  • Cloud providers
  • CRM platforms
  • Email marketing tools
  • Analytics platforms
  • Payment processors
  • Customer-support software
  • Advertising platforms

Review what personal information these vendors receive and understand the contractual and operational relationship between your company and those providers.

The CCPA also establishes separate requirements and definitions concerning service providers and contractors, so vendor management should be part of your compliance program.

4. Build a Consumer Request Process

A customer shouldn’t have to send emails to five different departments to exercise a privacy right.

Create a documented process for:

  1. Receiving a request
  2. Verifying the consumer where required
  3. Identifying relevant information
  4. Coordinating with internal teams and vendors
  5. Responding within the applicable timeframe
  6. Documenting the request and response

This becomes particularly important as your startup grows.

What Happens If a SaaS Startup Ignores CCPA Compliance?

Ignoring privacy requirements can create more than a legal problem.

For SaaS companies, poor privacy practices can affect:

Comply With CCPA compliance

Enterprise customers may ask vendors detailed questions about privacy and security during procurement.

A business that cannot clearly explain what personal information it collects, where that information goes, who can access it, and how privacy requests are handled may face greater scrutiny during enterprise sales and procurement.

In other words, CCPA compliance for businesses can become part of the customer experience and sales process, not just a legal requirement.

A Practical CCPA Compliance Checklist for SaaS Startups

If your startup may be subject to CCPA, use this checklist as a starting point:

  • Determine whether your business meets the CCPA definition and thresholds
  • Identify California consumers whose information you process
  • Create a personal information inventory
  • Map how personal information moves through your systems
  • Review your privacy notice
  • Document processing purposes
  • Review data retention practices
  • Establish consumer request procedures
  • Review opt-out mechanisms
  • Identify sensitive personal information where applicable
  • Review third-party vendors and contracts
  • Implement appropriate security safeguards
  • Document privacy responsibilities
  • Train relevant employees
  • Review compliance regularly

This checklist is a practical starting point, not legal advice. Businesses should obtain qualified legal guidance when determining their specific obligations.

CCPA Compliance Is an Ongoing Process

One mistake startups make is treating privacy compliance as a one-time project.

Your data environment changes constantly.

You might:

  • Launch a new feature
  • Add a marketing tool
  • Change cloud providers
  • Enter a new market
  • Acquire another company
  • Start collecting new information
  • Introduce AI-powered functionality
  • Add new analytics or advertising technologies

Each change can affect your privacy posture.

The CPPA’s updated regulations that took effect January 1, 2026 also introduced additional requirements for certain businesses, including requirements related to risk assessments, cybersecurity audits, and automated decisionmaking technologies, with phased compliance timelines for some requirements.

That makes ongoing monitoring increasingly important for growing SaaS companies.

How SOCLY.io Helps With CCPA Compliance

Managing privacy requirements, policies, risks, controls, evidence, and compliance tasks across spreadsheets can become difficult as a SaaS startup grows.

SOCLY.io helps startups bring compliance activities into a more structured and centralized workflow.

With SOCLY.io, teams can:

  • Organize compliance requirements and tasks
  • Track risks and security controls
  • Manage policies and documentation
  • Monitor compliance gaps
  • Centralize evidence
  • Improve visibility into their compliance posture
  • Reduce repetitive manual compliance work

This can help SaaS companies maintain a more consistent approach to CCPA compliance as their business and data environment grow.

Privacy is not meant to be a one-time project; it is meant to be incorporated into the operations of the business.

This checklist is not a substitute for legal advice.

However, it can provide a useful starting point for building a structured privacy program.

Frequently Asked Questions About CCPA Compliance

1. Who needs to comply with CCPA?

For-profit businesses that do business in California, collect personal information from California consumers, determine the purposes and means of processing that information, and meet at least one applicable statutory threshold may be subject to the CCPA.

2. Does CCPA apply to small businesses?

Yes, potentially. CCPA applicability is not based solely on the size of a business. A small business may still be covered if it meets one of the applicable statutory thresholds and other requirements.

3. Does CCPA apply to businesses outside California?

Yes, because a company does not have to be situated within California for it to be subject to the law. A business operating outside California but doing its business in California could be subject to the law.

4. What businesses need to comply with CCPA?

Covered entities usually comprise companies that conduct business in California, gather personal data from California residents, control the purposes and means of processing, and meet at least one statutory criterion.

5. Does CCPA apply to SaaS companies?

It could. SaaS firms could fall under CCPA, provided their business operations fit the requirements of the legislation. SaaS firms need to review their users, data flows, income, sharing, and vendors.

6. Do nonprofits have to comply with CCPA?

The CCPA generally applies to qualifying for-profit businesses and does not generally apply to nonprofits or governmental agencies. However, organizations should assess their specific structure and activities to determine whether any provisions apply.

7. Is CCPA compliance the same as GDPR compliance?

No, CCPA and GDPR are distinct legal regimes having their own scope, definition, and requirements. If a company is compliant with CCPA, it cannot be assumed to be compliant with GDPR.

Conclusion: Who Needs to Comply With CCPA?

CCPA applicability depends on your company’s structure, activities in California, handling of personal information, revenue, and whether the business meets one or more applicable statutory thresholds.

SaaS companies must realize that waiting for enterprise customers to ask about privacy can create unnecessary challenges.

They should understand what personal information they handle, how it is used, where it is transferred, what consumer rights apply, and whether the CCPA applies to their business.

The privacy program of your company will grow along with it.

Ready to build a more organized privacy and compliance program for your SaaS startup?
Categories
ISO 27001 SOC 2

SOC 2 vs ISO 27001: What’s The Difference and Which Does Your SaaS Company Need?

SOC 2 vs ISO 27001: What’s The Difference and Which Does Your SaaS Company Need?

SOC 2 vs ISO 27001: What’s The Difference and Which Does Your SaaS Company Need?

SOC 2 vs ISO 27001: What’s The Difference and Which Does Your SaaS Company Need?

>SOC 2 vs ISO 27001: What’s The Difference and Which Does Your SaaS Company Need?

SOC 2 vs ISO 27001: What’s The Difference and Which Does Your SaaS Company Need?

Learn the key differences between SOC 2 and ISO 27001, compare their benefits, costs, and certification requirements, and discover which security framework best aligns with your SaaS company's customers and growth goals.

SOC 2 vs ISO 27001: What’s The Difference and Which Does Your SaaS Company Need?

SOC 2 vs ISO 27001

You can build a genuinely secure SaaS product and still lose weeks to one thing: proving it.

So, now you have two acronyms, a security questionnaire, an engineering team already stretched thin and a compliance budget that definitely did not magically appear overnight.

This creates an extremely tricky question for a startup company: where should you spend your time and money?

Do you do SOC 2 compliance because all your US-based prospects are demanding it? Do you work toward getting an ISO 27001 certification since you are targeting an international customer base? Will you need both at some point? And, if so, will you be paying for essentially the same thing twice?

While there are some key similarities between the two frameworks, they cannot be used interchangeably due to differences in their structure and assessment models. The more effective framework will depend entirely on who you are selling to, in what regions, and at what stage of security maturity you are at.

What Are SOC 2 and ISO 27001 Actually For?

SOC was initially defined as Service Organization Controls, but the American Institute of Certified Public Accountants has now adopted a new name for its SOC series called System and Organization Controls.

SOC 2 is based on the Trust Services Criteria for the Assurance and Reporting Standard as developed by the AICPA. These criteria are used to evaluate and report on controls related to security, availability, processing integrity, confidentiality and privacy.

For ISO 27001, the official name is SO/IEC 27001 since it has been jointly developed by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC).

The standard’s main goal is to set specified requirements for an ISMS to identify security risks, how to treat those risks, put controls in place so that they don’t happen in the first place, and then continue to improve these security measures.

In simpler words:

SOC 2: “Prove to me that your controls are in place and are working.”

ISO 27001: “Prove to me that you have a system for managing information security risks.”

They both can be very useful, just in different ways. Here’s how:


SOC 2

ISO 27001

What is it?

Independent attestation report

International management-system standard

Certification?

It’s a report, not a certification

Yes, you get ISO 27001 certification

Best known in

US focused B2B SaaS

Global markets

Core focus

Controls & trust criteria

Information security management system

Audit outcome

SOC 2 report

ISO 27001 certificate

Scope

Defined system and selected Trust Services Criteria

Defined ISMS scope

Type 1 / Type 2

Yes

No equivalent Type 1 / 2 naming

Best for

Proving controls to customers

Demonstrating a mature, structured security program

If You’re A US-Focused Startup, SOC 2 Compliance Makes More Sense First

SOC 2 Type II attestation gives your customer more visibility regarding the controls implemented and audited on the controls over a period of time.

For an entrepreneur starting his journey in the world of SaaS, that would mean:

Less explaining. Less back-and-forth. More evidence for the security team reviewing your product.

If an enterprise customer has come to you and said, “We have to see your SOC 2 report before we move forward,” well, you know what to do. Get ready for SOC 2 compliance.


If You’re Selling Globally, ISO 27001 Certification Is a Stronger Option
ISO 27001 Certification

This is an internationally accepted standard, and the certification can show your dedication and capacity in information management.

In addition to that, it gives you what SOC 2 cannot. A formal certification against an international standard. This can be especially useful if your business is trying to enter markets where ISO certifications are already familiar to procurement and security teams.

And unlike SOC 2, ISO 27001 isn’t only about demonstrating a set of controls. It requires you to establish, maintain and continually improve an ISMS.

For a growing SaaS company, that’s a bigger operational commitment, but it can also give you a more structured foundation for managing security as the company scales.

But Which One Is Cheaper?
SOC 2 compliance or ISO 27001 certification

There isn’t a universal price point for SOC 2 compliance or ISO 27001 certification. The cost varies heavily based on the size of your organization, scale, already existing security controls, how much remediation is required and more.

The bigger question is:

How Much of The Work Have You Already Done?

If your SaaS company already has a solid IAM system, logging, incident response, vendor management, secure development and evidence collection, either of these options is simple.

If you’re starting from scratch, the expensive part isn’t the certificate or report.

It is the engineering, the tools, the documentation, the process adjustments needed to make your controls real.

In a time when one out of four attacks is perpetrated using AI technology, a 56% rise from the previous year, while the cost for each attack on average is $6 million, about $1 million higher than the worldwide average of $4.99 million per attack, as reported in IBM’s 2026 Cost of a Data Breach Report, the most economical choice is not necessarily the one that has the lowest cost of compliance.

It’s the one that gives you useful assurance without creating unnecessary operational overhead.

SOC 2 or ISO 27001? Make The Decision With A Few Points in Mind

Go for SOC 2 compliance first when:

  • Your target customers are in the US
  • Enterprise prospects are explicitly requesting a SOC 2 report
  • You want to move through SaaS vendor checks quicker
  • Your buyers care heavily about evidence of operating controls.
  • You want a clear first security win that’s practical

Pick ISO 27001 first when:

  • You are selling in multiple countries
  • Buyers ask for ISO 27001 certification specifically
  • You want a formal international credential
  • You are trying to run a wider security program based on risk
  • Your customer base sits across multiple regions and industries


Sometimes You May Need Both

It does not necessarily have to be an either-or decision.

Once your security program is mature enough, the work you do for one can help support the other. There is overlap across areas such as access control, risk management, incident response, supplier management, policies and security monitoring.

The exact mapping isn’t one-to-one, though. SOC 2 compliance and ISO 27001 certification have different requirements, structures and assessment approaches, so having one does not automatically mean you have the other.

Build The Right Compliance Path with SOCLY.io

You don’t need to choose between SOC 2 and ISO 27001 based on whichever acronym sounds more impressive.

SOCLY.io helps SaaS companies understand where they stand, identify what’s missing and build a practical path toward the compliance frameworks their customers actually require.

From gap analysis and control implementation to evidence collection, audit preparation and ongoing compliance, we combine automation with expert support so your team can spend less time wrestling with compliance and more time building the company. Sounds like what you’re looking for? We’re just a call away.

Because the right compliance strategy isn’t about doing more. It’s about doing what your business and its clients actually need.

Ready to Simplify Your Compliance Journey?
Categories
DPDPA

Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

>Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

Why the DPDP Act Matters for Indian Startups and SaaS Companies?

Learn how the DPDP Act helps Indian Start-ups and SaaS companies protect customer data, strengthen privacy practices, reduce data security risks, and build trust with customers.

Why the DPDPA Act Matters for Indian Startups and SaaS Companies?

DPDP Act Matters for Indian Startups

For Indian startups, customer data is one of their most valuable business assets. It is also a major responsibility.

The DPDP Act for startups makes data privacy an important business priority. Startups shouldn’t wait until they grow into big businesses to handle privacy.

It is more important for SaaS companies. An average SaaS company could be collecting data such as customer names, emails, phone numbers, employee details, payment methods, and other forms of data.

The startups who have knowledge about Digital Personal Data Protection Act early will benefit in terms of good privacy practices and risk reduction.

What Is the DPDP Act?

Digital Personal Data Protection Act 2023 (DPDP Act) is the primary legislation in India for regulating digital personal data.

This Act specifies the obligations of enterprises for processing digital personal data. Besides, it establishes individual rights over their personal data.

In plain language, the DPDP Act obliges enterprises to know:

  • What personal data they collect
  • Why they collect it
  • How they use it
  • How they protect it
  • Who they share it with
  • How long they keep it
  • What they do when something goes wrong

The above issues should form part of business practice. This is more so to startups who handle customer information in bulk.

Why Is the DPDP Act Important for Indian Startups?

Many startups believe that data privacy is mainly a concern for large companies. That approach is becoming difficult to maintain.

Startups may start off with just a few people using the product. But soon enough, they may have thousands or even millions of users.

As the organization expands, the personal information increases. Fixing privacy problems later can be costly.

The DPDP Act for startups matters for several key reasons.

1. Startups Handle More Personal Data Than They Realize

A SaaS startup may collect personal data through many different systems.

For example:

  • Website forms
  • Product registrations
  • User accounts
  • Customer support
  • Marketing campaigns
  • HR systems
  • Analytics tools
  • Payment systems
  • CRM platforms

Data collection may not be the main purpose of the business. Still, personal data can exist across different parts of the technology stack. Knowing where this data exists is the first step toward protecting it.

2. Privacy Builds Customer Trust

Consumers want to know how organizations treat their personal information. It may influence their purchasing decisions. It becomes especially relevant in the case of SaaS startups offering products to other enterprises.

Enterprise buyers may ask vendors about:

  • Data management
  • Security controls
  • Breach response
  • Compliance practices

Strong privacy practices can therefore become a competitive advantage for Indian startups.

3. Privacy Risks Can Become Business Risks

A data privacy issue can create problems beyond regulatory concerns.

For a startup, a personal data incident could lead to:

  • Customer complaints
  • Loss of customer trust
  • Contractual problems
  • Higher security costs
  • Business disruption
  • Reputation damage

Building privacy practices early can help startups reduce these risks.

Key DPDP Act Requirements Startups Should Understand

The Act introduces several concepts that SaaS companies should understand when building their privacy programs.

Consent and Lawful Processing

Organizations need a valid legal basis to process personal data. This may include obtaining consent where required.

There must be meaningful consent related to an intended use.

For instance, when a software-as-a-service firm collects an individual’s email address to create a user account, there must be a specific reason for doing this.

Notice and Transparency

Organizations need to communicate to individuals how their personal data will be used.

The privacy notice provided by organizations needs to be understandable.

A startup should clearly explain:

  • What data it collects
  • Why it collects the data
  • How it uses the data
  • How individuals can exercise applicable rights

Data Security

Organizations should use reasonable security safeguards to protect personal data.

For SaaS companies, these safeguards may include:

  • Access controls
  • Authentication
  • Encryption
  • Security monitoring
  • Vulnerability management
  • Employee security training
  • Incident response procedures
  • Secure software development practices

The right controls will depend on the company’s size, systems, risks, and data processing activities.

Data Retention

Startups should not keep personal data forever without a valid reason.

A practical data retention process should define:

  1. What data is stored
  2. Why the data is needed
  3. How long the data should be kept
  4. When the data should be deleted or disposed of

This is especially important for SaaS companies.

They may keep information from former customers or inactive accounts. Clear retention rules can help prevent unnecessary data storage.

DPDP Compliance for SaaS Companies

DPDP compliance for SaaS companies involves more than publishing a privacy policy.

A SaaS application can use many systems and third-party vendors. Each system may process personal data.

For example, customer information may move through:

Website
CRM
SaaS applications
Cloud infrastructure
Analytics platform
Analytics platform
Customer support system

Each part of this data flow should be considered when building a privacy program.

Map Your Data

Start by identifying the personal data your business collects.

Then, identify where that data goes.

Create a simple data inventory that includes:

  • Data type
  • Data source
  • Processing purpose
  • Storage location
  • Access permissions
  • Third-party recipients
  • Retention period

A data inventory gives your team a clearer view of its data environment.

Review Third-Party Vendors

SaaS companies often rely on third-party vendors for:

  • Hosting
  • Analytics
  • Payments
  • Communications
  • Customer support
  • Other business activities

Review each vendor that processes personal data.

Check:

  • What data the vendor receives
  • Why the vendor processes it
  • What security measures it uses
  • What contractual protections apply
  • What happens when the relationship ends

Vendor management should be part of your overall privacy and security program.

How Indian Startups Can Comply With the DPDP Act

Indian startups can become compliant with DPDPA on a phased basis.

Start with getting an idea of the kind of personal data collected by your firm. Next, examine the processes involved with such personal data.

Step 1: Identify Personal Data

Create a list of the personal data your organization processes, stores, or transfers.

Include data managed through:

  • Employees
  • Applications
  • Databases
  • Vendors
  • Marketing systems

This gives your team a starting point for its privacy program.

Step 2: Understand Why You Collect It

The purpose of every main type of personal data should be known.

Ask a basic question:

Is this data needed at all? And if some data is not needed, think about whether it is necessary to collect it. Reduced data collection will decrease privacy threats as well.

Step 3: Review Your Privacy Notices

Check your privacy notices from time to time. Ensure that they provide clear information about your processing operations.Don’t use confusing terminologies which might be difficult for the users to comprehend.

Step 4: Establish Data Retention Rules

Establish time frames for keeping each category of personal data. Develop policies on deleting information once it is no longer required. This will involve the processes for handling data in the systems and through the vendors using the data.

Step 5: Strengthen Security Controls

Review the technical and organizational measures used to protect personal data.
Depending on your environment, these may include:

  • MFA
  • Role-based access
  • Encryption
  • Logging
  • Vulnerability management
  • Backup procedures
  • Security awareness training

Review these controls as your startup grows and your systems change.

Step 6: Prepare for Data Breaches

Create an incident response process for personal data breaches.
Your team should know what to do when an incident occurs.

Define:

  • Who investigates the incident
  • Who makes key decisions
  • Who communicates internally
  • How affected systems are contained
  • What regulatory or contractual notifications may be required

A clear process can help your team respond faster and more consistently.

Step 7: Document Your Compliance Program

Keep records of important privacy and security activities.
Your documentation may include:

  • Privacy policies
  • Risk assessments
  • Vendor evaluations
  • Security measures
  • Compliance activities
  • Other relevant records

Good documentation can help demonstrate that your startup actively manages privacy risks.

DPDP Act Compliance for Indian Startups: Common Challenges

Startups often face similar challenges when they begin their privacy journey.

DPDP Act Compliance for Indian Startups

DPDP Act vs. GDPR: Are They the Same?

The DPDP Act and the European Union’s GDPR both focus on protecting personal data. However, there are different laws.

They differ in areas such as:

  • Scope
  • Terminology
  • Individual rights
  • Organizational responsibilities
  • Regulatory requirements

Therefore, GDPR compliance does not automatically mean DPDPA compliance.

Companies should review their existing privacy framework against the requirements that apply to their Indian operations. They should then identify and address any gaps.

For SaaS companies that operate in multiple countries, a privacy program should consider the requirements of each relevant jurisdiction. This can also make customer due diligence easier.

What Happens If Startups Ignore Data Privacy?

Ignoring privacy can create problems as a startup grows.

A company may initially think:

“We’re too small for this to matter.”

However, customers, investors, enterprise procurement teams, and business partners may expect evidence of responsible data handling.

Poor privacy practices can also create operational problems.

For example, a startup may suddenly need to:

  • Respond to a customer data request
  • Investigate a data incident
  • Remove data from multiple systems
  • Review a vendor’s data access
  • Explain its data practices to an enterprise customer

Building a privacy foundation early is usually easier than fixing gaps later.

How SOCLY.io Helps With DPDP Act Compliance

Managing privacy policies, risks, controls, evidence, and compliance tasks in spreadsheets can become difficult as a SaaS startup grows.

SOCLY.io helps startups organize these activities through a more structured and centralized workflow.

With SOCLY.io, teams can:

  • Organize compliance requirements and tasks
  • Track risks and security controls
  • Manage policies and documentation
  • Monitor compliance gaps
  • Centralize evidence
  • Improve visibility into their compliance posture
  • Reduce repetitive manual compliance work

This can help startups maintain more consistent compliance processes as they grow.

The goal is not to treat compliance as a one-time project.

Instead, privacy and security should become part of regular business operations.

A Practical DPDPA Compliance Checklist for SaaS Startups

Before considering your privacy program mature, check whether your startup has addressed the following:

This checklist is not a substitute for legal advice.

However, it can provide a useful starting point for building a structured privacy program.

Frequently Asked Questions

1. Why is the DPDP Act important for Indian startups?

Indian startups usually deal with personal information of their customers, employees, prospects, and other users. Applying proper privacy principles could be beneficial for startups when dealing with such information.

2. What is DPDPA compliance for Indian startups?

The adherence to DPDPA will entail the establishment of processes in relation to collecting, utilizing, safeguarding, storing and managing digital personal data. This will depend on the organization and its operations.

3. Does the DPDP Act apply to SaaS companies in India?

The DPDP Act may be relevant to the firms managing digital personal data in India based on the applicability of the Act. SaaS firms need to consider the type of personal data that is handled by them and its processing.

4. How can Indian startups comply with the DPDP Act?

These startups can start with checking on their personal data and the use of it. They will need to check on privacy notices, consents, security, data retention, vendors, incident response, and compliance documents.

5. What kind of data does the DPDP Act protect?

The DPDP Act is concerned with personal data in a digital environment. Personal data is defined as information that is identifiable to a person. Start-ups must take into consideration their methods of collecting, storing, processing, and utilizing personal data.

6. Does DPDPA compliance require a dedicated privacy team?

Not necessarily. The requirements could vary based on the company’s size, activities, data processing techniques, and duties. For smaller startups, they can start by delegating their responsibilities for privacy and security and setting processes in place.

7. How is DPDPA compliance different from GDPR compliance?

DPDP Act and GDPR are two different regulations with different obligations and terminologies. If organizations are required to comply with both, they need to analyze each regulation independently. Adherence to one regulation does not guarantee adherence to another.

Conclusion: 

The DPDP Act for startups is not only a legal or compliance issue. It can affect product development, customer data, vendor selection, system security, and customer trust. For Indian startups, starting early is important.As your startup grows, your data environment will grow too.

Building a strong privacy foundation early can make compliance easier in the future.

Ready to organize your compliance efforts in a SaaS startup?

Let's Talk

Tell us about your compliance needs and we’ll get back to you within 24 hours.

By submitting, you agree to our Privacy Policy and Terms of Service