

DPDP Rules 2025: Key Requirements and What Businesses Need to Know
DPDP Rules 2025: Key Requirements and What Businesses Need to Know
DPDP Rules 2025: Key Requirements and What Businesses Need to Know
>DPDP Rules 2025: Key Requirements and What Businesses Need to Know
DPDP Rules 2025: Key Requirements and What Businesses Need to Know
DPDP Rules 2025: Key Requirements and What Businesses Need to Know
Table of Contents
- Understanding the DPDP Rules 2025
- How the DPDP Rules 2025 Relate to the DPDP Act 2023
- DPDP Act 2023 vs. DPDP Rules 2025: What's the Difference
- When Were the DPDP Rules 2025 Notified? Full Timeline
- Key Highlights of the DPDP Rules 2025
- Core Compliance Requirements Under DPDP Rules 2025
- Special Provisions for Children's Data and Persons with Disabilities
- Data Retention Requirements Under the Third Schedule
- Operational Steps Businesses Must Take Immediately
- Penalties and Enforcement Businesses Must Prepare For
- How SOCLY.io Simplifies DPDP Rules 2025 Compliance
- Frequently Asked Questions
India’s Digital Personal Data Protection Rules 2025 are finally here, and if you run a business that handles personal data of Indian users, this directly affects you.
The DPDP Rules 2025 are meant to bridge any shortcomings in the DPDP Act 2023, translating vague provisions into something actionable. Think of the Act as the “what” and the Rules as the “how.” With the DPDP Rules 2025 now in effect, there is no more excuse for businesses to delay figuring out what compliance entails.
This document will provide compliance professionals, legal advisors, startup founders and business owners with a comprehensive and practical understanding of DPDP Act Rules 2025.
Here’s what you’ll find inside:
- What the DPDP Rules 2025 actually say – an overview of the main points covered, including the need for consent, data retention policies, and how the Rules are different from the Act
- Special obligations you may not have heard about – including specific protections for children’s data and persons with disabilities that carry their own compliance requirements
- What to do right now – the operational steps your business needs to take before enforcement kicks in, plus a look at the penalties if you don’t
Let’s get into it.
Understanding the DPDP Rules 2025
What the DPDP Rules 2025 Are and Why They Were Notified
The DPDP Rules 2025 are the set of operational rules released by the Ministry of Electronics and Information Technology (MeitY) that make the DPDP Act, 2023 functional. Consider them to be the guidelines that convert broad principles from legislation into concrete, actionable procedures of data protection that include data collection, processing, security, retention, and deletion.
This was not an initiative taken in isolation by the Ministry. The MeitY received 6,915 public submissions and organized consultations in Delhi, Mumbai, Guwahati, Kolkata, Hyderabad, Bengaluru, and Chennai before releasing them, which makes it one of the most consultative processes of regulation in India. With DPDP Rules 2025 explained through this level of public engagement, the framework carries significant institutional weight.
Source: Digital Personal Data Protection Rules, 2025 — full text (MeitY)
How the DPDP Rules 2025 Relate to the DPDP Act 2023
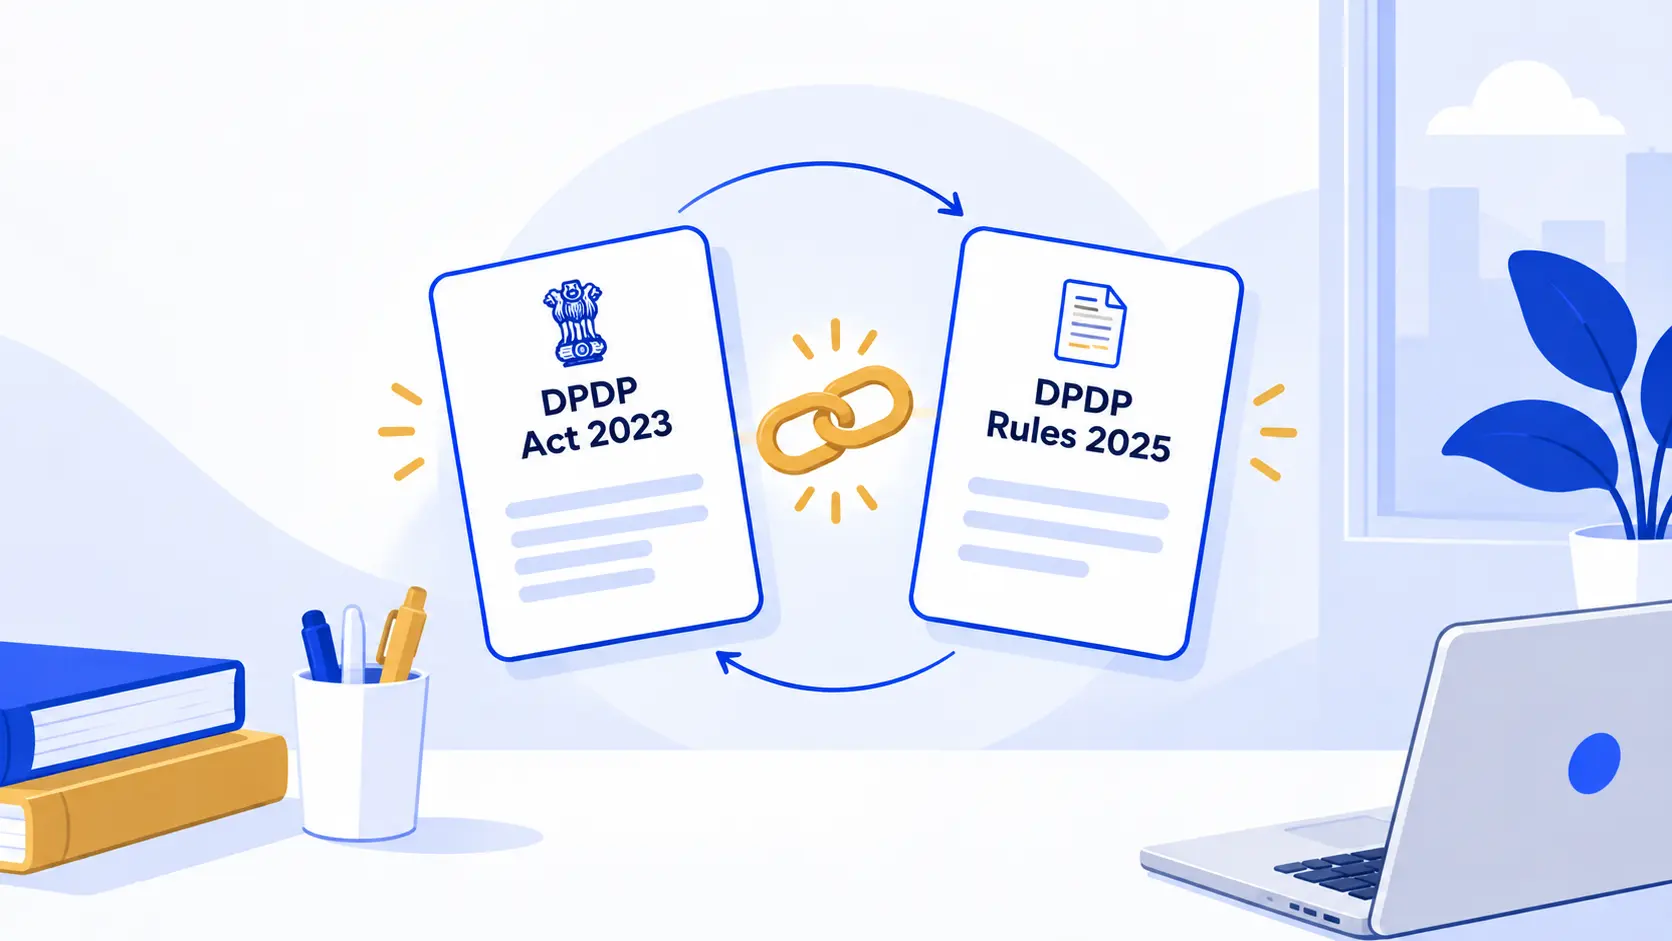
The Act sets out the principles; the Rules set the mechanics. While the Act defines rights and obligations at a high level, the Rules specify how those obligations must actually be met, a distinction explored in greater depth in the next section.
Why These Rules Matter for Businesses Operating in India
The New DPDP Rules 2025 make compliance non-negotiable. Enforcement is no longer theoretically defined, deadlines now exist. Crucially, these Rules apply equally to Indian and foreign businesses serving Indian users, regardless of where they’re incorporated.
DPDP Act 2023 vs. DPDP Rules 2025: What’s the Difference
A. Key Distinctions Between the Act and the Rules
DPDP Act 2023 | DPDP Rules 2025 |
Passed August 2023; Presidential assent 11 August 2023 | Notified 13 November 2025 via G.S.R. 846(E) |
Defines rights of Data Principals | Specifies how those rights are operationalised |
Establishes penalty structure (up to ₹250 crore) | Defines consent notice formats (Rule 3) |
Sets principles: purpose limitation, data minimisation | Details breach notification procedures (Rule 7) |
Creates the Data Protection Board | Prescribes data retention periods (Third Schedule) |
Think of the DPDP Act 2023 as the “what” — the legal framework, rights, and consequences. The Rules are the “how” — the practical mechanisms your organisation must implement.
Sources: DPDP Act, 2023 — full text (MeitY) · DPDP Rules, 2025 — full text (MeitY)
B. Why You Need Both to Achieve Full Compliance
Reading only the Act tells you that consent is required but not the exact format, language requirements, or approved verification methods. Reading only the Rules without the Act leaves you without the legal context for penalties and rights.
“DPDP Act Rules 2025” and “DPDP Rules 2025” are different ways to describe the exact same set of rules, and are interchangeable in all official communications.Now that this naming confusion is resolved, understanding both documents together gives your compliance programme its complete legal and operational foundation.
When Were the DPDP Rules 2025 Notified? Full Timeline
Official Notification Date
When were the DPDP Rules 2025 notified? The DPDP Rules 2025 were notified in the Official Gazette on 13 November 2025, via Gazette notification G.S.R. 846(E), with MeitY’s public announcement following the next day, on 14 November 2025. This marks India’s formal entry into a structured, rights-driven data protection era.
Source: DPDP Rules, 2025 official notification (PIB press release)
Phase I – What’s Effective Immediately
The DPDP Rules 2025 effective date begins from the notification date itself. Rules 1, 2, and 17–21 came into force immediately, establishing the Data Protection Board’s purpose, appointment process, and operational functioning. You don’t get a grace period here — these obligations apply from day one.
Phase II – Consent Manager Registration (~12 Months)
Approximately one year from publication (~November 2026), Rule 4 activates. This is your DPDP Rules 2025 implementation date for Consent Manager registration, eligibility criteria, and oversight requirements. If your business involves managing user consent at scale, this deadline directly affects your operating model.
Full Compliance Obligations (~18 Months)
Around 18 months from publication (~May 2027), Rules 3, 5–16, 22, and 23 come into full effect covering the bulk of day-to-day Data Fiduciary obligations. This is the deadline you should anchor your compliance roadmap around.
Phase | Timeline | Key Rules Activated |
Phase I | Immediate (13 Nov 2025) | Rules 1, 2, 17–21 |
Phase II | ~12 months (~Nov 2026) | Rule 4 |
Full Compliance | ~18 months (~May 2027) | Rules 3, 5–16, 22, 23 |
Please note that a proposal to reduce the 18-month period to 12 months has informally been made by MeitY. At the time of writing, there is no formal notification of this through the Gazette. Please take the 18-month timeframe into account, but watch out for any official communication in case it changes.
Key Highlights of the DPDP Rules 2025
A. Who the Rules Apply To
Understanding DPDP Rules 2025 applicability is your first step toward compliance. The Rules apply to:
- Data Fiduciaries – entities that determine the purpose and means of processing personal data
- Data Processors – entities processing data on behalf of fiduciaries
- Significant Data Fiduciaries (SDFs) – those designated by the government, carrying heightened obligations
Critically, there is no turnover or company-size threshold. Whether you are a startup or an enterprise, the Rules apply equally to your organization based on your processing activities.
B. Consent Notice Requirements
Each Data Fiduciary needs to provide a separate and distinct notice of consent, which shall be drafted in language that is clear and simple to understand by the Data Principal. This notice cannot be buried inside your general terms of service or privacy policy. It must itemize the specific purposes for which personal data is being collected and processed.
C. Data Protection Board Structure and Functioning
The Data Protection Board is an office functioning digitally wherein everything from filing of complaints to conducting proceedings would take place online. This streamlined structure makes it accessible and efficient for handling grievances under the DPDP Rules 2025.
D. Appellate Tribunal and Appeal Process
If you disagree with a Board decision, the Rules establish a structured appeal procedure through a designated Appellate Tribunal, a procedural detail most compliance guides overlook but one that significantly affects your risk management strategy.
Core Compliance Requirements Under DPDP Rules 2025
A. Data Fiduciary Obligations and Responsibilities
As a Data Fiduciary, you must collect only the personal data necessary for a clearly defined purpose, nothing beyond that. The DPDP Rules 2025 hold you accountable for ensuring data is used strictly within that stated purpose and deleted once it is no longer needed.
B. Consent Management and Lawful Basis for Processing
Your consent mechanisms must meet a high standard. Consent under DPDP Rules 2025 must be:
- Free – no coercion or conditional access
- Specific – tied to a defined purpose
- Informed – clearly explained before collection
- Unconditional and unambiguous – no bundled or implied consent
- Easy to withdraw – as simple as it was to give
C. Data Principal Rights Businesses Must Uphold
You are obligated to honour the following rights for every individual whose data you process:
- Access – provide data summaries upon request
- Correction – update inaccurate personal data
- Erasure – fulfil erasure requests within 90 days (Rule 14), including data held by your Data Processors
- Grievance Redressal – maintain a functional complaint mechanism
D. Cross-Border Data Transfer Restrictions and Approvals
With this in mind, cross-border transfers are permitted by default under DPDP Rules 2025. No countries are restricted yet, but the Government retains authority to block specific destinations. You should monitor official notifications regularly to stay ahead of any future restrictions.
Special Provisions for Children’s Data and Persons with Disabilities
A. Verifiable Parental Consent Requirements
Before processing personal data of any child under 18 or a person with a disability who has a lawful guardian you must obtain verifiable parental or guardian consent. This is a non-negotiable prerequisite under the DPDP Rules 2025, not a best-practice recommendation. Non-compliance here carries penalties of up to ₹200 crore.
B. DigiLocker-Based Identity Verification
Here’s a detail most compliance guides overlook: Rule 10 of the DPDP Rules 2025 explicitly permits DigiLocker-based verification as a mechanism to confirm a parent’s identity and establish the parent-child relationship. This gives you a practical, government-backed method to meet the verifiability requirement without building complex custom verification infrastructure.
C. Prohibited Practices: Tracking, Profiling, and Targeted Ads
As a Data Fiduciary, you are strictly prohibited from:
- Tracking children’s online behaviour
- Profiling children for any purpose
- Serving targeted advertisements directed at children
In addition to the above constraints on processing, you need to implement technical age-gate measures to ensure that children do not access services inappropriate for their age group. This is not an optional set of controls but one expected by regulators to be backed up with technical solutions.
Data Retention Requirements Under the Third Schedule
Sector-Specific Retention Periods
The Third Schedule of the DPDP Rules 2025 lays out clear data retention timelines for large-scale platforms. Once the purpose for which data was collected is fulfilled, these platforms must erase personal data within the defined period with no exceptions.
Here’s what the current retention periods look like:
Platform Type | User Threshold | Retention Period |
E-commerce platforms | 2 crore+ registered users | 3 years from last transaction or login |
Online gaming platforms | 50 lakh+ registered users | 3 years from last transaction or login |
Social media platforms | 2 crore+ registered users | 3 years from last interaction |
Note: Always verify these figures against the latest official gazette notification before building your compliance calendar, as rules may be updated.
Which Businesses This Applies To
This schedule does not apply to every business operating in India. Your obligations under the Third Schedule kick in only if your platform crosses the user thresholds specified above.
If you run a small or mid-sized operation well below these numbers, this particular schedule doesn’t bind you though your general data minimization and erasure duties under DPDP Rules 2025 still apply.
Operational Steps Businesses Must Take Immediately
A. Conducting a Data Audit and Mapping Exercise
To begin with, it is necessary to create a comprehensive list of all the personal data collected, stored, processed, and disclosed by the organization. The process will provide an understanding of all the areas where there are vulnerabilities. The inventory created is going to serve as the basis for all the further actions related to compliance with the DPDP Rules 2025.
B. Updating Privacy Notices and Consent Mechanisms
Your privacy notices should now be written in clear language and not be too general and vague. You need to review all data gathering points and ensure that consent is sought for purposes which are clearly stated prior to any processing. It should also be easy to withdraw consent.
C. Establishing a Grievance Redressal System
Establish an exclusive communication channel through which data principals can communicate their concerns and requests for correction. The DPDP Rules 2025 have specified specific deadlines for the response to such queries. This can be as simple as a ticketing system with an escalation route.
D. Appointing a Data Protection Officer Where Required
A DPO is mandatory only for Significant Data Fiduciaries as designated by the government. That said, many businesses voluntarily appoint one to manage compliance proactively and build trust with customers, a smart move even if you’re not legally required to do so.
Penalties and Enforcement Businesses Must Prepare For
Financial Penalties for Non-Compliance
The DPDP Rules 2025 come with a sharp penalty structure you cannot afford to ignore. Here’s what’s at stake:
Violation Type | Maximum Penalty |
Security safeguard failures | ₹250 crore |
Breach notification failures | ₹200 crore |
Children’s data violations | ₹200 crore |
Significant Data Fiduciary failures | ₹150 crore |
General non-compliance | ₹50 crore |
These aren’t theoretical numbers, they’re the actual caps defined under Schedule I of the DPDP Act, 2023.
Source: Schedule I, DPDP Act, 2023 (full text, MeitY)
Regulatory Authority Powers and Oversight Mechanisms
The Data Protection Board of India holds real teeth. It can investigate complaints, summon records, conduct inquiries, and issue binding decisions against your organization. The Board also has the authority to impose penalties and direct remediation all without requiring a court order.
How to Reduce Risk of Enforcement Action
Getting your compliance in order now costs a fraction of what a breach investigation or penalty proceeding will. When you build data governance practices proactively consent management, breach response, retention policies, you’re not just avoiding fines; you’re protecting your customers and your reputation. Waiting until something goes wrong is always the more expensive option.
How SOCLY.io Simplifies DPDP Rules 2025 Compliance
Automating Consent Tracking and Data Subject Requests
Manually tracking consent across thousands of users is a nightmare waiting to happen especially when the DPDP Rules 2025 require you to respond to erasure and access requests within a 90-day window.
SOCLY.io replaces those messy spreadsheets and email chains with automated consent logs that update in real time. When a Data Principal submits a request, the platform routes, tracks, and timestamps it automatically, so you never miss a deadline.
Integrating DPDP Requirements into Existing Security Frameworks
If your organization already runs on SOC 2 or ISO 27001 controls, you don’t need a separate compliance stack for DPDP. SOCLY.io maps DPDP Act Rules 2025 obligations directly onto your existing security framework, giving you a single dashboard to manage data protection requirements alongside your current controls. This means less duplication, fewer gaps, and a cleaner audit trail.
For a deeper look at how SOCLY.io handles end-to-end DPDP compliance automation from breach notifications to Data Fiduciary obligations.
check out our dedicated DPDP compliance guide.
If you’re also working on ISO 42001, SOC 2, or ISO 27001, those guides cover how each framework overlaps with your DPDP obligations.
Frequently Asked Questions
When Were the DPDP Rules 2025 Notified?
The DPDP Rules 2025 were notified in the Official Gazette on 13 November 2025, via Gazette notification G.S.R. 846(E), with MeitY’s public press release following on 14 November 2025. (The draft Rules were published for consultation to the public on 3 January 2025. This was the draft stage, and not the final notice of rules.) The Rules will now be implemented through three phases up to May 2027.
What Are the Requirements for Compliance with the DPDP Act in India?
Your compliance checklist starts with obtaining free, informed, and specific consent before processing personal data. You also need robust security safeguards, a clear grievance redressal mechanism, and a process to honor data principal rights including the right to access, correct, and erase personal data. Head back to the Core Compliance Requirements section for a full breakdown.
Can You Provide a Summary of the DPDP Rules 2025?
The Digital Personal Data Protection Rules, 2025 further elaborate on the workings of the DPDP Act, 2023. The Rules deal with issues related to the management of consent, data protection for children, security, and retention of personal data. Significant Data Fiduciaries have to adhere to additional requirements such as conducting audits and DPIAs.
What’s the Difference Between the DPDP Act and DPDP Rules?
The DPDP Act 2023 sets the legal framework and broad principles. The DPDP Rules 2025 are the operational rulebook spelling out exactly how your business must implement those principles day to day.
Who Is a Significant Data Fiduciary?
Significant Data Fiduciary is an organization that is designated by the government as a data fiduciary due to the nature, quantity, or risks associated with the data being processed. If your business qualifies for being a significant data fiduciary, you have the obligation of appointing a Data Protection Officer and conducting DPIAs every year.
The DPDP Rules 2025 represent a major change in the way that businesses functioning within the Indian jurisdiction need to deal with personal data. From getting explicit consent to handling data about children, creating retention timelines, and facing stringent fines – the requirements of compliance are very real, very detailed, and very non-negotiable. If you are a business in India – regardless of your size – you cannot ignore this anymore.
Getting compliant doesn’t have to be difficult. It’s all about being aware of the requirements of the laws, taking the appropriate actions, and leveraging platforms built for this purpose. You can build a strong data privacy framework that protects your users and your business.
Tools like SOCLY.io are designed to simplify exactly this journey, helping you stay on top of your DPDP obligations without losing focus on what matters most: running your business with trust and accountability at its core.
Our Recent Posts
-
DPDP Rules 2025: Key Requirements and What Businesses Need to Know
-
ISO 27001 Risk Treatment Plan: How to Identify, Evaluate and Treat Security Risks
-
How to Define Your SOC 2 Scope: A Practical Guide for Startups
-
ISO 42001 Certification: 2026 Guide to Requirements, Cost, Timeline & Process
-
Who Needs to Comply With CCPA? A Guide for SaaS Businesses