System and Organization Controls
Information Security Management System
Artificial Intelligence Management System
General Data Protection Regulation
Health Insurance Portability and Accountability Act
California Consumer Privacy Act
Digital Personal Data Protection Act
An information security strategy that is effective is only possible if one knows what can go wrong and how the company should respond. The ISO 27001 Risk Assessment process will enable the SaaS startup to identify risks and know how to deal with them to ensure protection of sensitive data.
The purpose of risk assessment in this scenario is not just to ensure that the ISO 27001 is complied with but also a pragmatic way through which it becomes easier to identify the vulnerabilities before they lead to any incident.
ISO 27001 risk assessment can be defined as an approach that entails the identification of security threats, assessing their likelihood and impact, and determining which risks need to be managed.
Risk assessment is an integral element of the organization’s ISMS.
The following are some of the questions that need to be answered by performing a risk assessment:
As an example, a start-up that creates software as a service may detect the threat of unauthorized access to its production database.
ISO 27001 follows a risk-based approach to information security. Instead of applying every possible security control regardless of circumstances, organizations identify their specific risks and determine appropriate controls.
Effective ISO 27001 risk management can help SaaS startups:
The framework will be most useful for start-ups since they have limited resources and should concentrate their efforts on the things that really matter.
How can we perform a risk assessment for ISO 27001 compliance?
Though various firms adopt different strategies to achieve this, one practical approach is to start by defining the scope, then identifying, analyzing, evaluating, and finally treating the risks.
Step 1: Define the Scope
Prior to the identification of risks, it is necessary to define the scope. The scope definition for a SaaS company could be:


Clearly defining the scope prevents the assessment from becoming too broad or disconnected from your actual ISMS.
Step 2: Identify Your Information Assets
Next, identify the information and assets that need protection.
Examples include:
An inventory of assets could help in comprehending the location of sensitive data.
Step 3: Identify Potential Risks and Threats
Now ask: What could happen to these assets?
Common information security risks for SaaS startups include:
Don’t limit the assessment to technical threats. Human and operational risks can be equally important.
The case in which an employee makes an accidental revelation of customer-sensitive data to an unintended recipient can be seen as a legitimate information security risk.
Step 4: Analyze the Risks
After identifying risks, the next step is to assess each risk based on criteria such as likelihood and impact.
A basic risk score can be calculated using:
Risk Score = Likelihood × Impact
For example:
Risk | Likelihood | Impact | Risk Level |
Phishing attack | 4 | 4 | 16 – High |
Cloud misconfiguration | 3 | 5 | 15 – High |
Lost employee laptop | 2 | 3 | 6 – Medium |
Minor website outage | 2 | 2 | 4 – Low |
The exact scoring methodology can vary. What matters is that your organization uses a consistent and documented approach.
Step 5: Evaluate and Prioritize Risks
However, not all risks identified have to receive the same treatment.
After scoring them, rank the risks using your organization’s risk criteria.
Some high-priority risks will need immediate attention, while low-level risks may simply be monitored.
A good example can be the risk of unauthorized production access for a new business venture, where the customers’ personal information could be exposed.
Prioritizing helps avoid wasting valuable resources on every single risk.
After evaluating risks, the next stage is ISO 27001 risk treatment.
Organizations generally have several options for dealing with identified risks.
1. Reduce the Risk
Implement controls that lower the likelihood or impact of the risk.
For example:
Risk: Unauthorized access to production systems.
Possible controls:
2. Avoid the Risk
Sometimes, it would be most appropriate to avoid an activity altogether due to an unacceptably high level of risk involved.
For instance, a business could decide not to collect certain kinds of sensitive information which are not required for their service.
3. Share or Transfer the Risk
An organization may transfer some risk through mechanisms such as contracts or insurance.
However, transferring risk doesn’t necessarily eliminate the organization’s responsibility for managing it.
4. Accept the Risk
Some risks may be low enough that the organization decides to accept them.
This decision should be documented and approved according to the organization’s risk management process.
The selected treatment options should also inform the Statement of Applicability (SoA), which documents the necessary controls and their justification.
After deciding how to handle each significant risk, create a risk treatment plan.
The plan should make it clear:
For example:
Risk: Former employees retain access to company systems.
Treatment: Automate employee offboarding and revoke access immediately.
Owner: IT/Security
Target: Implement within 30 days.
This turns your risk assessment from a document into an actionable security program.
Maintain a Risk Register
A risk register provides a centralized record of identified risks and their treatment status.
A typical register might include:
Field | Example |
Risk ID | R-001 |
Asset | Customer database |
Risk | Unauthorized access |
Likelihood | High |
Impact | High |
Risk rating | Critical |
Treatment | Reduce |
Control | MFA + access reviews |
Owner | Security Lead |
Status | In Progress |
Keep the register updated as your systems, threats, vendors, and business processes change.
An ISO 27001 risk assessment for SaaS companies should reflect the realities of cloud-based businesses.
SaaS startups commonly need to consider risks involving:
Cloud Infrastructure
Misconfigurations of storage, exposure of services, excessive permissions, and insecure cloud infrastructure pose substantial security challenges.
Application Security
Potential vulnerabilities of applications, APIs, dependencies, and developer pipelines could be harmful to both the company and its clients.
Identity and Access Management
Incorrect authentication mechanisms and too much employee privileges may cause threats for the organization.
Third-Party Vendors
SaaS businesses often depend on numerous vendors. A security issue within a critical third-party service can affect your own operations.
Employee Security
Remote work, personal devices, phishing, weak passwords, and accidental data exposure should also be considered.
The assessment should reflect your actual environment rather than simply copying a generic risk register.
For startups, the biggest mistake is making the risk assessment unnecessarily complicated.
A practical ISO 27001 risk assessment process for startups can follow these principles:
You don’t have to do a huge risk assessment with hundreds of risks you can think of.
You need to conduct an accurate risk assessment that helps your organization make better decisions.
The ISO 27001 risk assessment process is not a one-off exercise.
It needs to be repeated regularly and whenever there is a major change.
Consider reassessing risks when:
Regular reviews help ensure your risk register remains relevant.
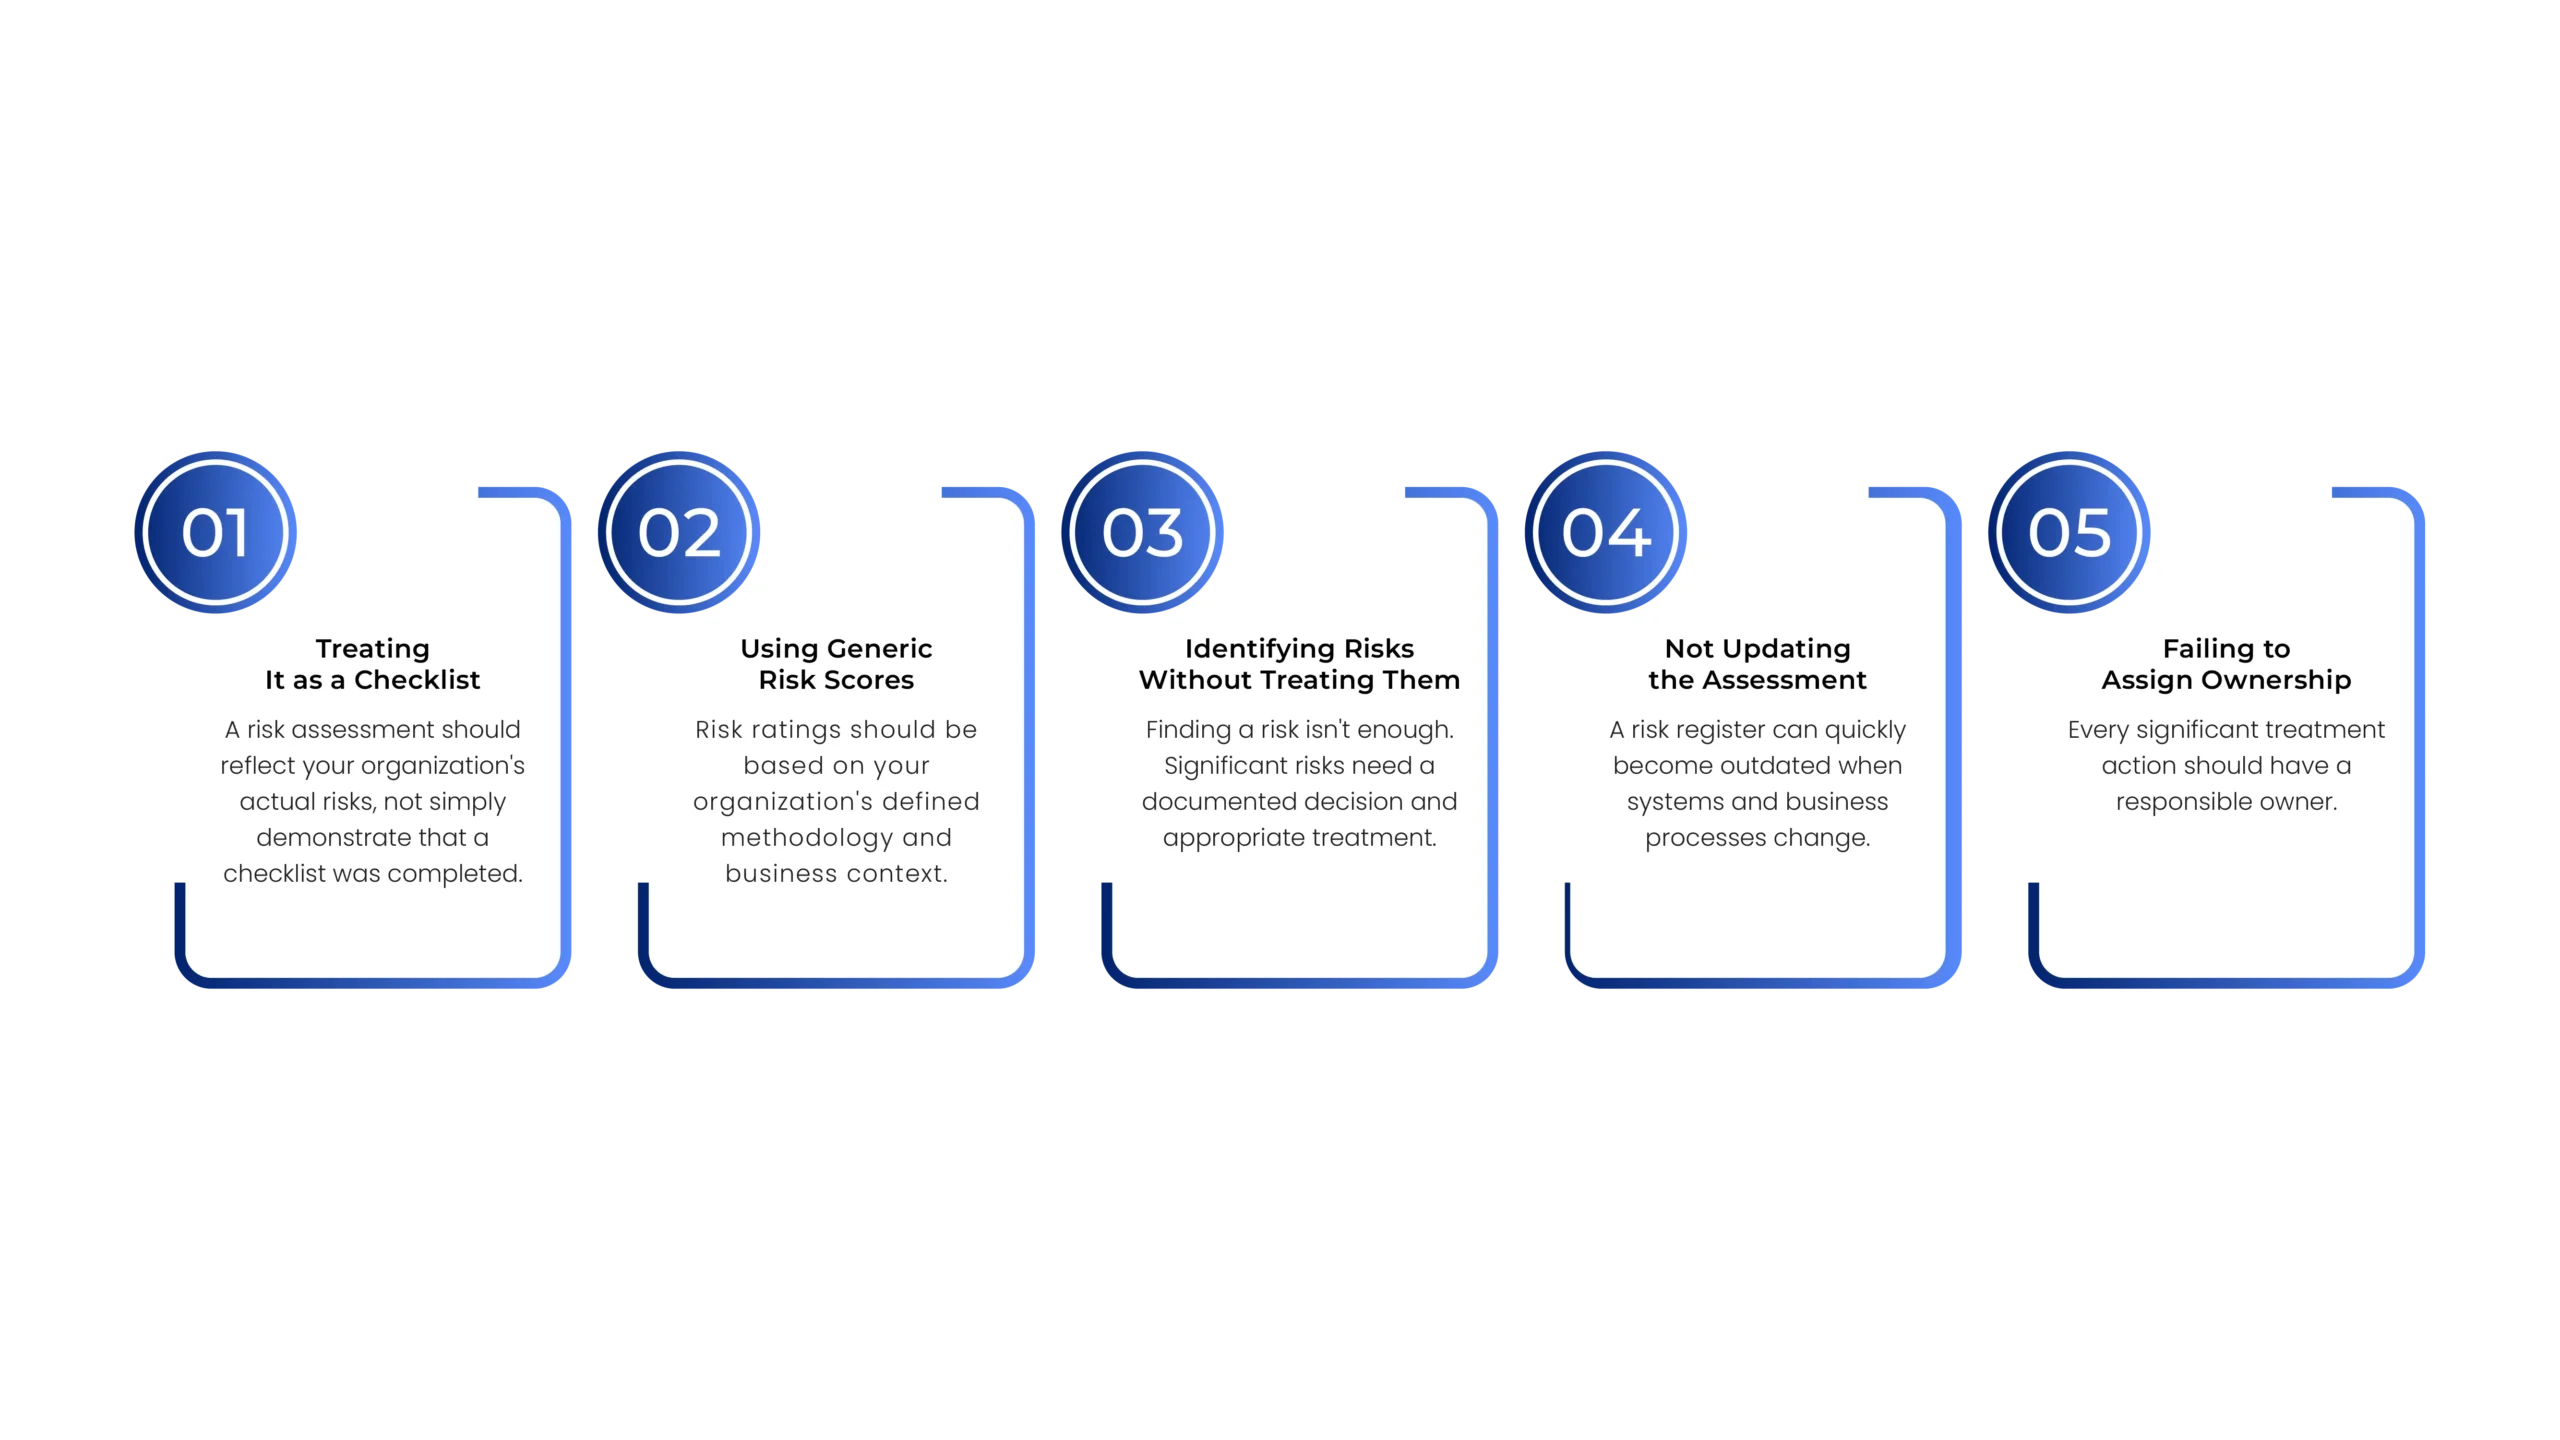
When conducting an ISO 27001 risk assessment, avoid these common problems:
Managing risks, controls, evidence, and compliance tasks manually can become difficult as a SaaS startup grows. SOCLY.io helps streamline the process by bringing key compliance activities into a centralized workflow.
With SOCLY.io, teams can:
Instead of maintaining risk management information across disorganized spreadsheets and documents, startups can adopt a more systematic approach to managing their ISO 27001 activities.
Risk management should not be considered as an end-of-the-year activity, but rather as an organizational process.
It is quite time-consuming for SaaS companies to manage SOC 2 manually. SOCLY.io allows you to streamline compliance management by integrating the whole process of evidence, control, task, and audit management.
With SOCLY.io, startups can:
SOCLY.io eliminates spreadsheets, scattered information, and manual tracking allowing SaaS companies to focus more on their product and growth than on compliance management.
1. What is an ISO 27001 risk assessment?
An ISO 27001 risk assessment is a systematic approach to identifying the risks associated with information security, assessing their probability and impacts, ranking and then determining risk treatment strategies.
2. How do you conduct an ISO 27001 risk assessment?
For performing an ISO 27001 risk assessment, the scope should be determined, information assets should be identified, threats and vulnerabilities should be identified, likelihood and impact should be analyzed, risks should be prioritized, and a risk treatment plan should be developed.
3. What are the key stages of a risk assessment according to ISO 27001?
The key stages are setting the scope of the assessment, asset identification and risk identification, risk analysis and evaluation, selection of risk treatment, decision recording, and risk monitoring over time.
4. What is ISO 27001 risk treatment?
ISO 27001 risk treatment is the determination of how an organization will respond to its risks. This may involve any combination of risk reduction, avoidance, transfer, and acceptance.
5. How does ISO 27001 risk assessment apply to SaaS companies?
For SaaS companies, risk assessment should consider cloud infrastructure, customer data, application security, APIs, employee access, third-party vendors, development environments, and business continuity.
6. How often should an ISO 27001 risk assessment be performed?
Risk assessments need to be reviewed on a regular basis as well as in the case of any major changes to the information security environment of the organization.
7. Do startups need a formal ISO 27001 risk assessment?
Yes. In the case of ISO 27001, if a startup wants to achieve the said certification, then it must have an established process for information security risk assessment.
A good ISO 27001 risk assessment helps SaaS companies understand where information security risks exist and what actions they should take.
The approach does not need to be complex: scope definition, asset identification, realistic risk evaluation, prioritization of those risks, and action plan development with designated owners of those actions.
What is most critical is not allowing your risk assessment to turn into another document that you update once a year when preparing for an audit. Your risk assessment needs to be dynamic and integral to your security management process.
Your risks will evolve along with your company; your risk assessment needs to keep up with them.
Get started with ISO 27001 today with SOCLY.io.
Your trusted partner in compliance automation. Turn complex regulations into clear, automated workflows.
By submitting, you agree to our Privacy Policy and Terms of Service

