System and Organization Controls
Information Security Management System
Artificial Intelligence Management System
General Data Protection Regulation
Health Insurance Portability and Accountability Act
California Consumer Privacy Act
Digital Personal Data Protection Act
CCPA is California’s privacy law, and it applies to many businesses you wouldn’t expect, including ones that have never had a presence in the state. If you collect the data of Californians and you exceed specific thresholds, you must give Californians control over their data. This includes giving them the ability to access, delete, fix, or opt out of having their data sold or shared.
This California CCPA guide 2026 is intended to give you an understanding of who the CCPA applies to, how the CCPA impacts your business, and changes that took place on 1 January 2026. It is written with compliance and the founder in mind. When referencing a figure from the regulator, we give credit and a citation.
The California Consumer Privacy Act is an act of the state of California which grants Californians their rights with respect to the collection of personal information by business organizations. The Act became effective in 2020 and has been amended since then. There are two enforcement agencies for the Act, namely, the California Attorney General and the California Privacy Protection Agency (CPPA).
“Personal information” means something more than just names and email addresses. Personal information includes all such data that identify an individual or household or reasonably could be linked to an individual: IP address, cookies, device ID, purchases, browsing behavior, even the inferences drawn by business organizations from the consumer’s preferences. Employees and prospective employees are considered as consumers from 1 January 2023.
You can read the law itself in the CCPA statute (Civil Code §1798.100 et seq.) and the CCPA regulations as amended, effective 1 January 2026.
They are described as two distinct pieces of legislation, but that is not true. The California Privacy Rights Act (CPRA), passed in a vote by the citizens in 2020, amended the CCPA, and most of its amendments have become applicable as of 1 January 2023. When one refers to “CCPA,” it means CCPA as amended by the CPRA.
| Area | Original CCPA | After the CPRA |
|---|---|---|
| Regulator | Attorney General | Attorney General plus the new CPPA |
| Rights | Know, delete, opt out of sale | Adds correct, limit use of sensitive data, opt out of “sharing” |
| Data volume test | 50,000 consumers, households, or devices | 100,000 consumers or households |
| Sensitive data | Not a separate category | “Sensitive personal information” defined |
| Cure period | 30 days to fix a violation | No automatic right to cure for regulator enforcement |
| Employee and B2B data | Temporarily exempt | Exemptions ended 1 January 2023 |
The simple test: You are a profit-making entity conducting business in California; collecting personal information about California residents and deciding how it will be used; and meeting any one of the following three criteria. Government entities and many nonprofits are excluded from this definition. An entity that controls or is controlled by a covered business, shares its branding, and receives its customers’ personal information can be covered too, as can certain joint ventures.
The Three Thresholds
| Test | Threshold |
|---|---|
| Annual gross revenue | Over $26,625,000 in the preceding calendar year |
| Data volume | Buy, sell, or share the personal information of 100,000 or more consumers or households a year |
| Revenue from data | 50% or more of annual revenue comes from selling or sharing personal information |
One is enough. The revenue figure is adjusted for inflation every odd-numbered year, so expect a new number in January 2027. The CPPA publishes the current amounts on its monetary thresholds page.
If You’re Based Outside the US
You don’t need an office, employees, or a US entity. If you serve Californians and cross a threshold, the law can reach you. The revenue test also isn’t constrained to revenue within California; it’s broadly interpreted to mean total gross revenue. Many non-US organizations are surprised to learn about this. If you are borderline and unsure, talk to your attorney.
Three Quick Examples
Hypothetical scenarios only to demonstrate how the tests are applied.
Exemptions
Exemptions apply to some categories of data, not organizations. Data regulated by HIPAA or Gramm-Leach-Bliley Act is exempted, for example, but the rest of the information is still covered.
Not sure where you land? Get a free CCPA applicability check.
The Core Rights
| Right | What it gives people |
|---|---|
| Know | See the categories and specific pieces of personal information you hold, where it came from, why you use it, and who gets it. For data collected on or after 1 January 2022, the look-back can go beyond 12 months, unless that is impossible or takes disproportionate effort. |
| Delete | Ask you to delete their data, subject to legal exceptions. |
| Correct | Ask you to fix inaccurate information. |
| Opt out | Stop the sale or sharing of their data, including through browser signals like Global Privacy Control. |
| Limit | Restrict use of sensitive personal information to what’s necessary. |
| Non-retaliation | Use any right without being penalized. |
| Step | Deadline |
|---|---|
| Confirm you received a request to know, delete, or correct | 10 business days |
| Respond | 45 calendar days, extendable by another 45 with a written explanation (90 maximum) |
| Honor an opt-out of sale or sharing | As soon as feasible, and within 15 business days |
There is no need for verification of one’s identity when opting out. However, other requests may require such verification, but ensure that it is appropriate, and not excessive. One 2025 enforcement case turned partly on exactly that.
The 45 days run from the day the request arrives, even if verification takes time. The same timing applies to ADMT access and appeal requests. An online-only business with a direct relationship with consumers can offer just an email address for requests; everyone else needs at least two methods, one of them a toll-free number.
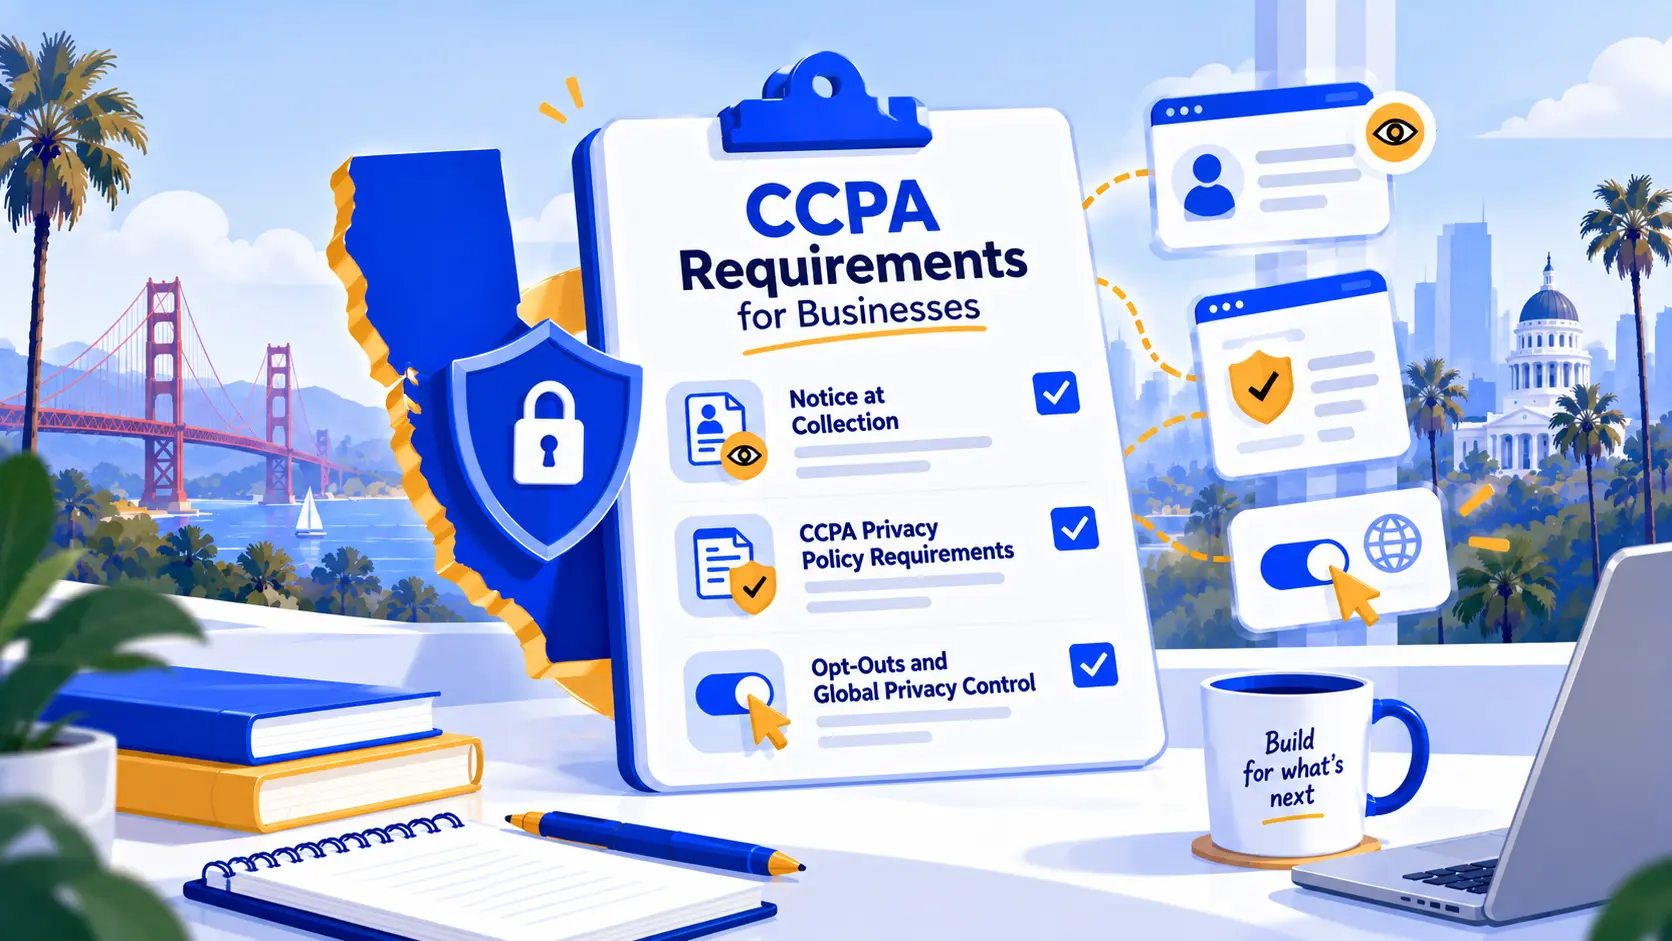
Notice at Collection
Inform individuals, prior to or during collection of their data, about the categories of data being collected, the purposes for collecting them, whether they are sold or shared, and how long each category is retained.
CCPA Privacy Policy Requirements
The privacy policy has to address the categories of personal information collected and disclosed in the last 12 months, source of the information, purpose of using it, recipients of the information, rights of individuals and how to exercise those rights, and whether information is sold or shared. It must be updated at least once every 12 months and is considered an ongoing effort tied to the data map, rather than a once-in-a-lifetime legal document.
Opt-Outs and Global Privacy Control
If you are selling or sharing personal information, then you have to provide a proper “Do Not Sell or Share My Personal Information” link (or its alternative) and respect opt-out preference signals, including Global Privacy Control, and treat them as opt-outs. From 1 January 2026, you also have to inform the visitor about the processing of their opt-out signal. Options should be symmetrical – opting out cannot require more clicks than opting in. California also passed a law in 2025 that requires browsers to support these signals from 1 January 2027.
CCPA Service Provider Contract Requirements
Handing personal information to a vendor without the right contract can turn that handoff into a sale or share. A service provider or contractor agreement should:
The 2026 rules also lean on vendor cooperation, so it’s worth adding clauses that require vendors to help with audits, risk assessments, and ADMT. Missing contracts were one of the issues the CPPA raised in the 2025 Tractor Supply settlement. If you’re a SaaS company, you’re probably on the other end: your customers will send you a data processing addendum, so read it against this list.
Security, Minimization, and Records
Use reasonable means to secure the data you collect, and collect and use only that which is reasonably necessary for your disclosed purposes. Maintain records of consumers’ requests and your responses for a minimum of 24 months.
Amended regulations were passed by the CPPA board on 24 July 2025. The Office of Administrative Law, California approved these regulations on 22 September 2025, while their implementation began on 1 January 2026. These regulations revise existing ones and include three new subjects: risk assessment, cybersecurity audit, and automated decision-making technology (ADMT). It takes time to implement some changes, therefore here is the timetable for the CCPA regulations 2026 and CCPA 2026 changes.
| Requirement | Applies from | First deadline |
|---|---|---|
| Updated existing rules (opt-out signals, notices, requests) | 1 Jan 2026 | In effect |
| Risk assessments | 1 Jan 2026 | Attestation and summary to the CPPA by 1 Apr 2028, covering 2026 and 2027 |
| ADMT for significant decisions | 1 Jan 2027 | Pre-use notice, opt-out, and access rights in place |
| Cybersecurity audits | Phased by revenue | Certification due 1 Apr 2028 (over USD 100M), 1 Apr 2029 (USD 50M to 100M), 1 Apr 2030 (under USD 50M), based on 2026, 2027, and 2028 revenue |
CCPA Risk Assessment Requirements
A risk assessment is required prior to the commencement or continuation of processing which involves substantial risk to consumers. The conditions are selling or sharing personal information, processing sensitive personal information, using ADMT to make significant decisions or to train ADMT, and other processing the rules treat as high-risk (see §7150 of the regulations). Risk assessments take into account the advantages and disadvantages of processing with regard to the rights of consumers. Processing that began before 1 January 2026 and continues needs an assessment by 31 December 2027, new processing needs one before it starts, and the attestation and summary go to the CPPA by 1 April 2028.
Automated Decision-Making Technology (ADMT)
In the rules, “ADMT” refers to technology which substitutes or substantially substitutes human judgment such that its output is relied upon without any significant human involvement. The obligations will be triggered only in respect of a “significant decision,” defined as a decision that results in the provision or denial of financial or lending services, housing, education enrollment or opportunities, employment or independent contracting opportunities or compensation, or healthcare services.
From 1 January 2027, a business using ADMT this way must give a pre-use notice, honor opt-outs (unless it offers a qualifying human appeal route), and answer access requests about how the technology was used. If you build or deploy AI, our ISO 42001 guide covers the governance side.
CCPA Cybersecurity Audit Requirements
Annual Audits are used if there is high risk to security due to your process. It is either generating 50% or more of revenue from selling and sharing personal data or having more than the threshold revenue and processed personal information of 250,000 or more consumers or households, or 50,000 or more consumers’ sensitive personal information in the previous year.
This is conducted by a qualified, objective, and independent auditor – either internal or external – who evaluates 18 components of your cybersecurity program. You send a written certification to CPPA every April and retain your audit documentation for five years. For large companies, the first audit covers from 1 January 2027 to 1 January 2028.
A SOC 2 or ISO 27001 report can serve as good documentation, but do not rely on them to cover all components of the audit. Go through all the components of the audit line by line and see what controls you need to put in place.
Other 2026 Updates
The CPPA’s Delete Request and Opt-out Platform (DROP) is live too, though it matters mostly to data brokers.
Where to Read the Official Text
The CPPA’s CCPA updates page hosts the approved regulations. The consolidated regulations, effective 1 January 2026, are here, and the statute is here.
An 8-Step Process
CCPA Compliance Checklist
CCPA Compliance for SaaS Companies
You usually sit on two sides at once. For your own website visitors, trial users, and employees, you’re a business with the duties above. For your customers’ data, you’re typically a service provider, so what matters is the contract terms, support for deletion and access requests, and security. Enterprise buyers will ask for a data processing addendum and a security review. Have both ready before the deal reaches procurement.
Regulators and big customers don’t take your word for it. They ask for proof. Keep this for each obligation:
| Obligation | Evidence to keep |
|---|---|
| Data mapping | A current data inventory with review dates |
| Notices and policy | Dated versions of every notice and policy |
| Consumer requests | A request log with timestamps, verification steps, and outcomes (24 months minimum) |
| Opt-outs and signals | Test results showing signals are honored and confirmation is displayed |
| Vendors | Signed contracts, vendor classification, review notes |
| Risk assessments | Completed assessments, approvals, attestation drafts |
| Security | Control evidence and audit reports mapped to the audit components |
| Training | Attendance and completion records |
If you already run SOC 2 or ISO 27001, much of the required security and vendor evidence may already exist. However, the overlap between CCPA and these systems is only a broad one, which means that you should compare it with the audit requirements, rather than assuming. This is where many compliance programs fail, as it requires extensive manual work with spreadsheets. Talk to a compliance specialist about getting it automated.
If you sell in California, Europe, and India, these three laws land on the same desk.
| CCPA (as amended) | GDPR | DPDPA (India) | |
|---|---|---|---|
| Basic model | Notice, with opt-outs for sale and sharing | You need one of six lawful bases | Consent, plus limited "legitimate uses" |
| Who's covered | For-profit businesses over thresholds | Any organization processing EU personal data | Digital personal data processed in India or offered to people in India |
| Size thresholds | Yes | No | No |
| Core rights | Know, delete, correct, opt out, limit sensitive data | Access, rectify, erase, restrict, port, object | Access, correct, erase, grievance redressal, nominate |
| Maximum penalty | $2,663 per violation; $7,988 if intentional or involving known minors under 16 | €20 million or 4% of global turnover | ₹250 crore |
| Regulator | Attorney General and CPPA | EU data protection authorities | Data Protection Board of India |
One program covers most of the overlap: one data map, one notice procedure, one request procedure, one vendor list. The differences that matter are the legal basis under GDPR, thresholds and opt-outs under CCPA, and consent plus the Board under DPDPA. The DPDP Rules of India were notified on 13 November 2025, with full compliance requirements by May 2027. We have a DPDPA compliance guide covering that side.
Under the CPPA, the fine is up to $2,663 per violation, and up to $7,988 per intentional violation or violation involving consumers the business knows are under 16. This applies to each violation, which means that even just one failed process, that affects many people, may lead to a high fine. In addition, if a breach exposes unencrypted or unredacted personal information because of a failure to maintain reasonable security, consumers may sue for $107 to $799 per consumer per occurrence, or any actual damages if greater.
What Gets Enforced
The 2025 cases follow a pattern. Most are execution failures, not missing paperwork.
The lesson is practical. Test your opt-outs, don’t over-collect when verifying requests, and get contracts in place before data moves.
There’s no official CCPA compliance certificate to earn. What you need is proof that your program works, and keeping that proof current is the hard part. SOCLY.io collects evidence automatically, monitors your controls continuously, and maps CCPA alongside SOC 2, ISO 27001, GDPR, and DPDP in one place, with compliance specialists to help before and during audits. See how the platform works, or read our guides to SOC 2 and ISO 27001.
Does CCPA apply to my business? If you’re a for-profit business that does business in California and meets any one of three tests, yes: revenue over $26,625,000, buying, selling, or sharing data on 100,000 or more consumers or households, or earning 50% or more of revenue from selling or sharing personal information.
Does CCPA apply to companies outside the US? It can. You don’t need a US office or entity. If you serve California residents and cross a threshold, you’re in scope.
What’s the difference between CCPA and CPRA? The CPRA amended the CCPA. Today’s CCPA includes its changes: new rights, a dedicated regulator, and rules for sensitive data.
What are the new CCPA regulations for 2026? The revised regulations came into force on 1 January 2026. The revised regulations introduce new provisions for risk assessment, cybersecurity audit and ADMT. The deadlines range between 2026 and 2030.
What are the penalties for violating the CCPA? Up to $2,663 per violation and $7,988 per intentional violation or violation involving known minors under 16. Data breach claims can bring $107 to $799 per consumer per incident.
Is there a CCPA certification? No official one that we’re aware of. The certification you file with the CPPA after a cybersecurity audit is a different thing.
How long do I have to respond to a CCPA request? Confirmation must take place within 10 business days, followed by a response within 45 days, which can be extended for 45 days with reasons. Opt-outs must be respected within 15 business days.
Is SOC 2 enough for the CCPA cybersecurity audit? Not automatically. It helps as evidence, but compare your controls against the audit’s 18 components to find what’s missing.
CCPA compliance is less about reading the law than about keeping proof that your processes work. Start with applicability, fix the basics regulators keep catching (opt-outs, notices, vendor contracts), then plan for the 2026 deadlines. Get your free CCPA gap assessment, or see how the same approach works for DPDP, SOC 2, and ISO 27001.
Sources: CPPA monetary thresholds · CPPA CCPA updates page · CCPA regulations, effective 1 January 2026 · CCPA statute (Civil Code §1798.100 et seq.)
Your trusted partner in compliance automation. Turn complex regulations into clear, automated workflows.
By submitting, you agree to our Privacy Policy and Terms of Service

